Vigilant Device Control

Every Port Controlled. Every Threat Blocked.

Vigilant Device Control empowers your organization to monitor and regulate every peripheral device — from USB drives to Bluetooth accessories — connecting to your network, ensuring only trusted devices ever touch your endpoints.
Translucent USB drive and illuminated padlock representing peripheral device protection

Today's Reality

01
Man in gray sweater with white earbuds using an open dark laptop indoors; faint “4.5” marker and dotted panel overlay

Visibility

Watch Every Flow in Real Time

  • Continuously detect and log all USB and Bluetooth connections in real time

  • Gain complete visibility into every peripheral touching your network

  • Spot unauthorized activity the instant it happens
02
Security dashboard “Dashboards” with tabs (Vulnerabilities selected), “Last year” filter, three donut summary cards and a table of CVEs and scores

Control

Only Trusted Devices Get Through

Enforce precise, attribute-based policies from a single console — allowing only approved devices while automatically blocking everything else across your organization.

  • Set granular policies by vendor ID, product ID, and device class

  • Full control over USB and Bluetooth, including Bluetooth Low Energy

  • Manage every device policy centrally across all endpoints
03
Dark security dashboard in a browser showing “Vulnerabilities” with a filter bar, CVE/severity chips, and a table listing assets and “Critical” alerts

Enforcement

Automatic Response to Every Threat

The moment an unapproved device connects, Vigilant Device Control blocks it, logs the incident, and triggers instant alerts — containing risks before they ever spread.

  • Automatically block unapproved devices the instant they connect

  • Log every incident automatically for full accountability

  • Trigger immediate alerts to contain threats in real time
04
Man with laptop on light green sofa in bright lobby; translucent overlay lines and faint “Oct. 2014” text near right center

Compliance

Stay Compliant, Stay Protected

Meet workplace and regulatory standards by controlling exactly how data moves — ensuring only approved devices are ever used and reducing insider risk across the board.

  • Meet workplace and regulatory compliance requirements with ease

  • Control data transfer to prevent leaks and misuse

  • Minimize insider threats and accidental data breaches
Decorative background gradient

Get Started

Symmetrical 3D geometric open box of glossy translucent panels around a glowing light-blue cube on a white background

Use Cases

Your Endpoints. Your Rules.

Know what connects to your endpoints.

Review storage, accessories, and devices that have not been approved.
Abstract layered blocks representing security context

USB Storage Visibility

Understand which removable storage devices connect to your endpoints.

Explore the Platform
Purple smartphone protected by a translucent security shield

Peripheral Inventory

Review the accessories and peripheral types used across your organization.

Explore the Platform
Person working at a computer in an office

Restrict Unapproved Devices

Use configured policies to limit access for devices that have not been approved.
Explore the Platform

Device control in practice

Know what connects. Decide what gets access.

Vigilant Device Control helps security teams review peripherals and manage their access around the needs of the organization.

  1. 01

    Observe

    Review connected storage, accessories, and other peripherals in the context of the endpoint.
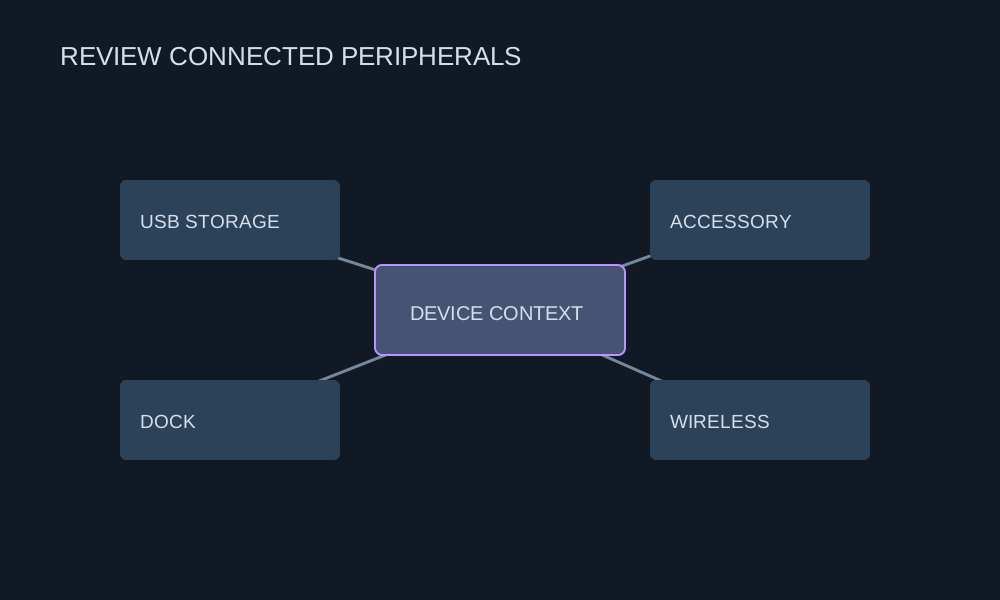
    Peripheral types connected to device context
  2. 02

    Review

    Use device ownership and business needs to guide access decisions and exceptions.
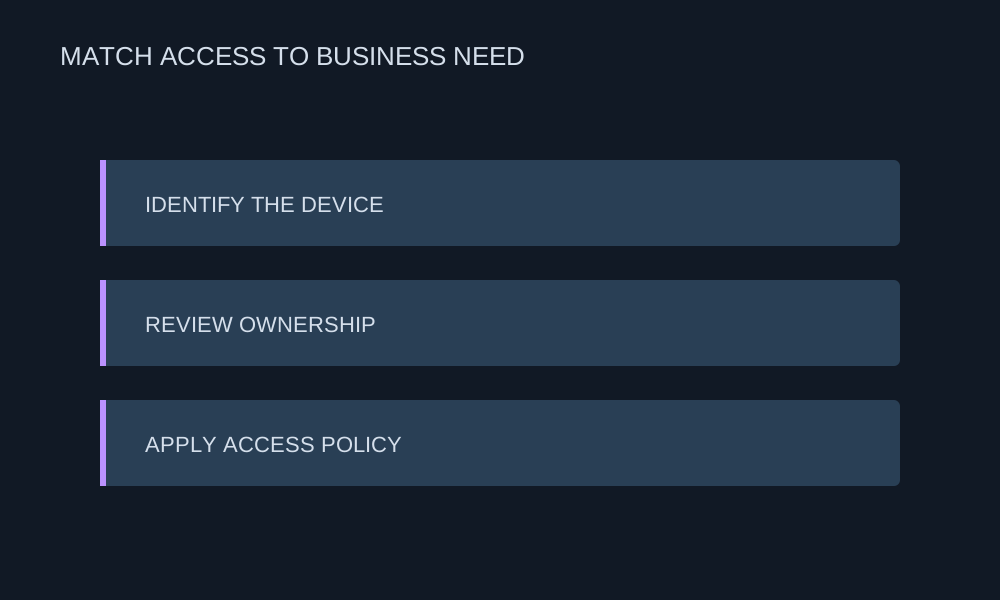
    Device identification, ownership review, and access policy workflow
  3. 03

    Control

    Apply peripheral access policies and review connection activity to support investigation.
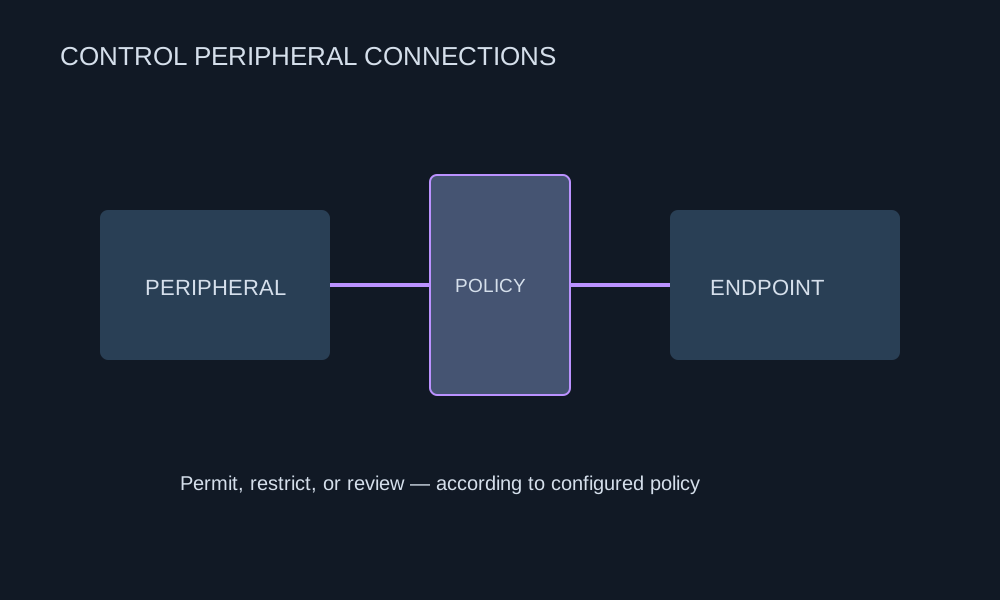
    Access policy boundary between a peripheral and an endpoint

Customer & industry focus

Security for the organizations that connect Yemen.

From telecom infrastructure to mobile services, explore local security priorities and the DeepSafer capabilities that address them.
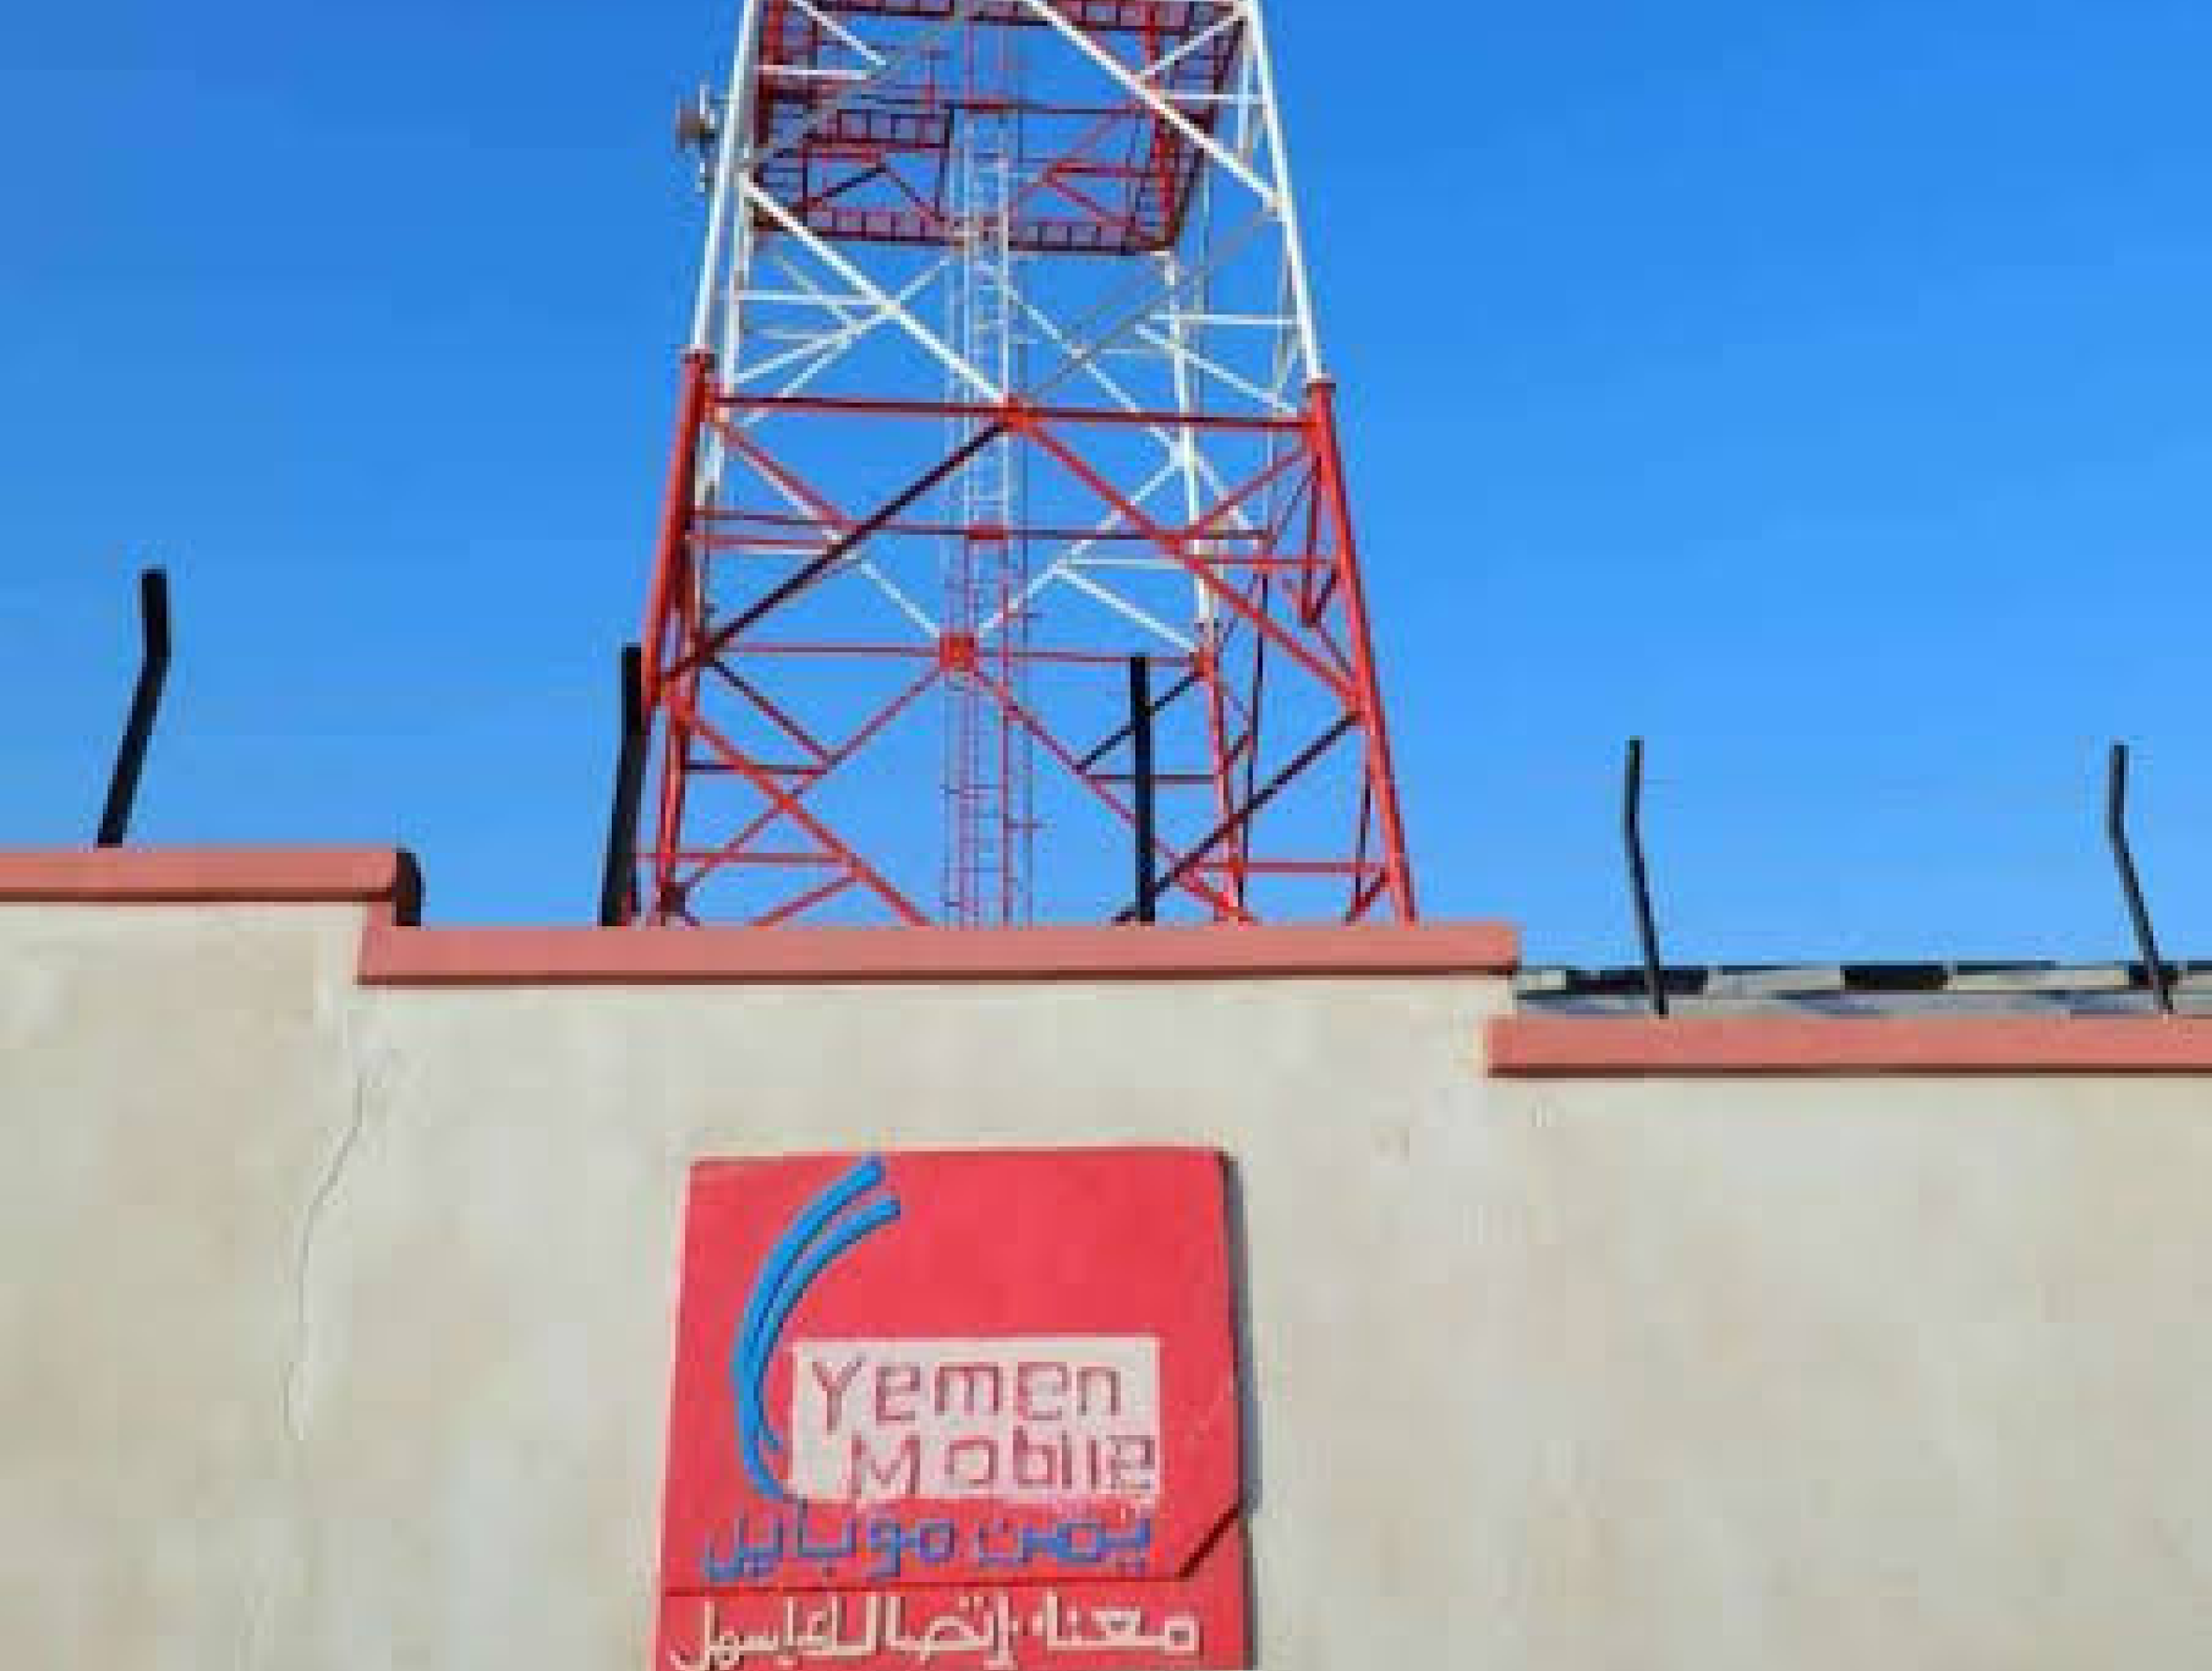
Yemen Mobile telecommunications tower and site

Visibility into connected peripherals.

Yemen Mobile

Mobile services & endpoint protection

Review the storage devices and accessories used with workforce endpoints and the context around their connections.
Explore the solution
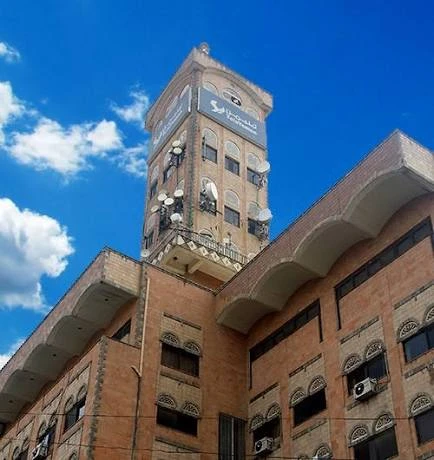
TeleYemen building and telecommunications tower

Device access around business needs.

TeleYemen

Telecommunications & infrastructure

Organize peripheral access decisions and exceptions to support the way the organization operates.

Explore the solution
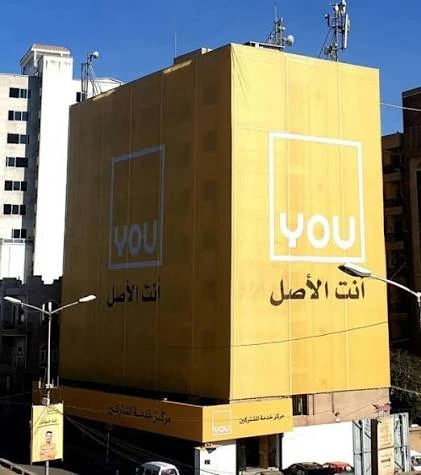
YOU company building with its yellow facade and logo

Context for review and follow-up.

YOU

Yemen Omani United telecommunications

Use device activity and asset ownership to guide policy reviews and access requests.


Explore the solution

Why DeepSafer

Access policies built around everyday work.

Review peripherals and access needs, and organize policies and exceptions to support the way teams work.
Consistent Peripheral Policies

Consistent Peripheral Policies

Bring device access decisions into a repeatable workflow across managed endpoints.

Support Distributed Work

Support Distributed Work

Review peripheral access for people working across office and remote environments.

Device Context Before Access

Device Context Before Access

Consider hardware and endpoint context before approving unfamiliar peripherals.

Practical Exception Handling

Practical Exception Handling

Help support teams review device access requests alongside everyday operations.

Connected Audit Context

Connected Audit Context

Use peripheral activity alongside endpoint and operational context during review.

Platform Integration

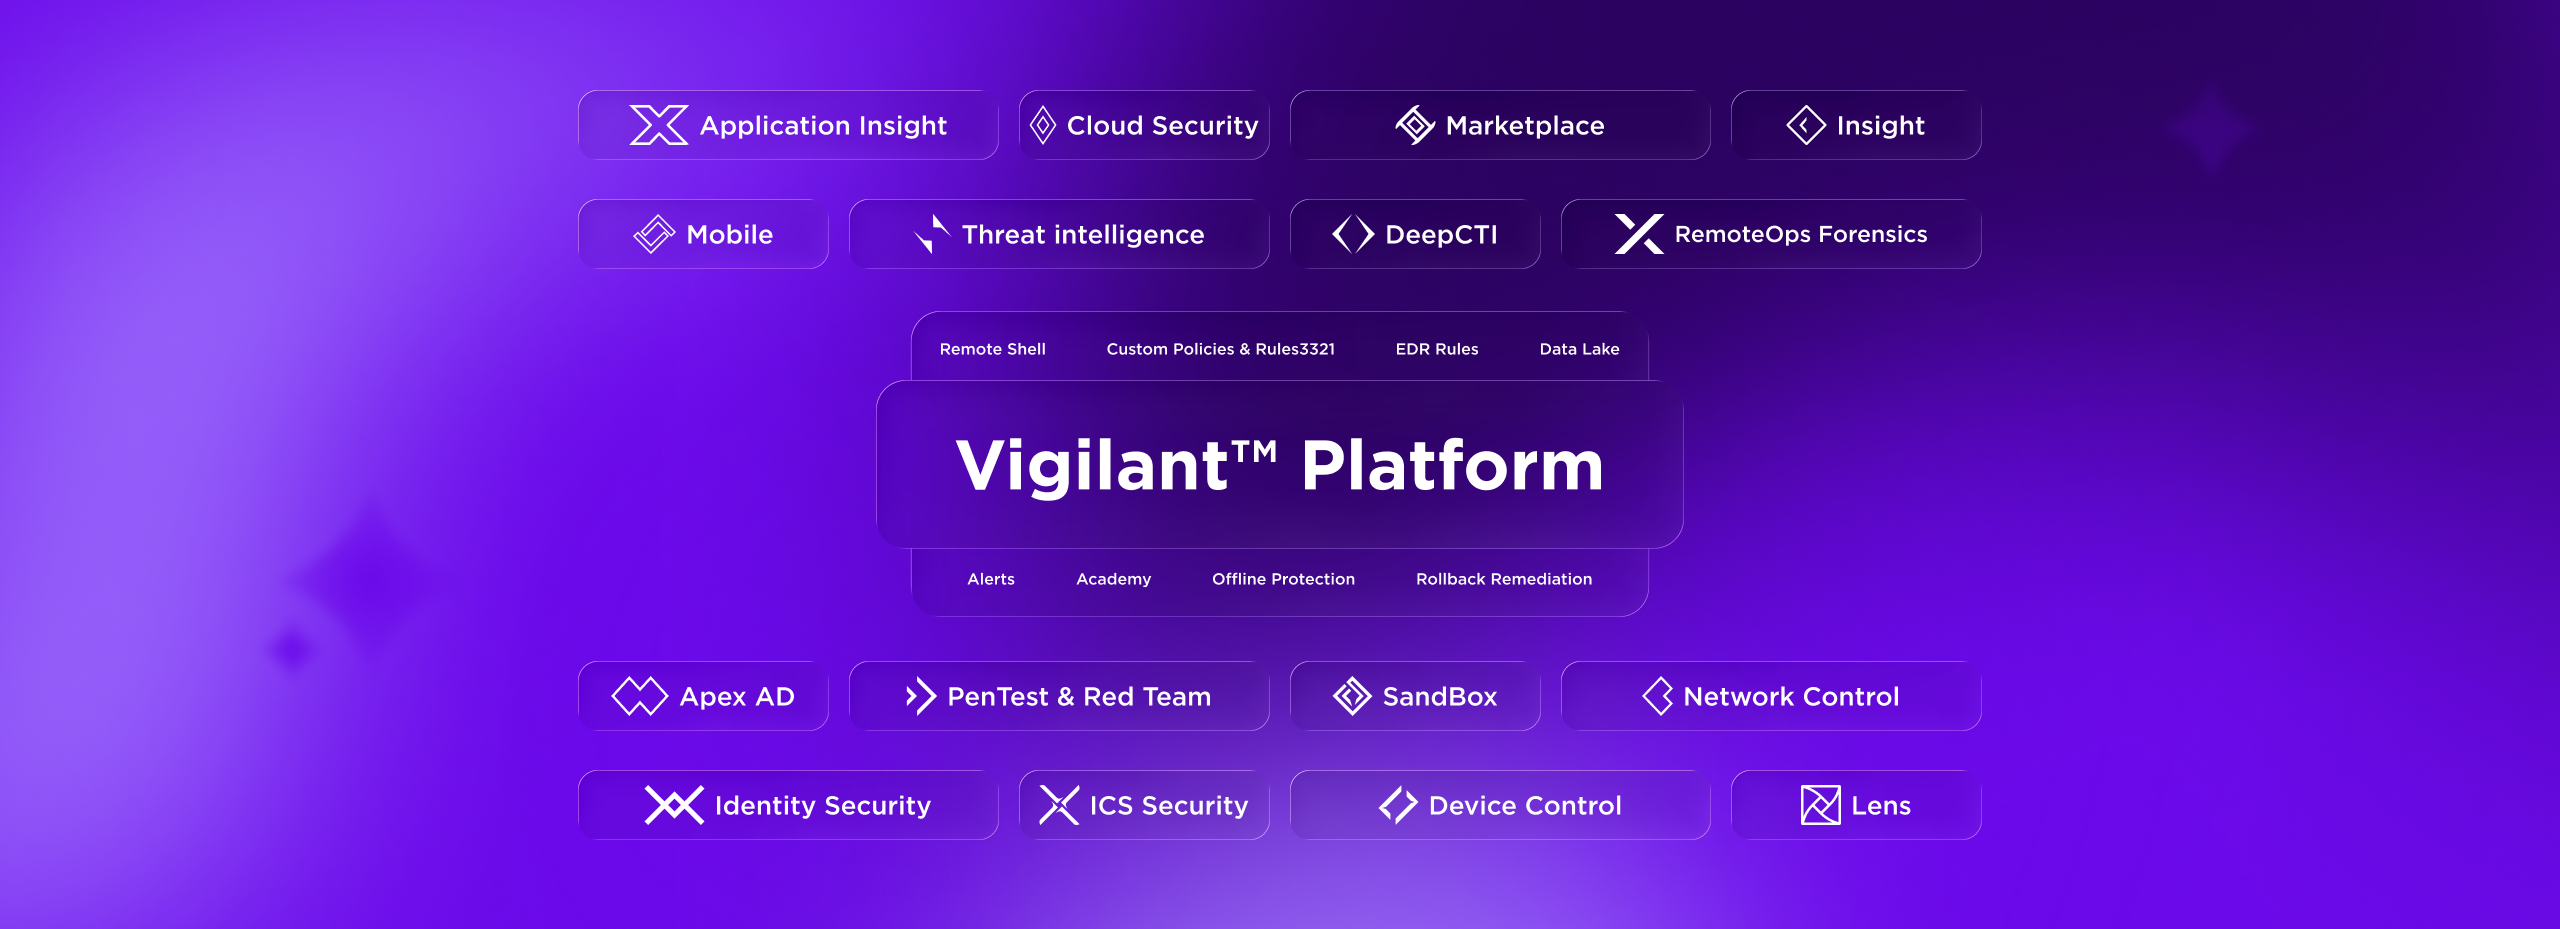
One Platform. A Singular Advantage.

Futuristic UI mockup titled “Vigilant Platform” with neon platform, orb, labeled sections, and sidebar “DeepSafer”
01

From Detection to Prevention

Find exposures and stop the threats targeting them. Same AI-native agent. Same console.

02

Context That Drives Faster Response

Correlate exploit attempts with known vulnerabilities to prioritize response by real-world risk.

03

Consolidated Workflows. Fewer Tools.

Manage endpoint protection and vulnerability scanning from a single console. One place to investigate, prioritize, and act. No tool switching required.

Need Answers?
Frequently Asked Questions

Vulnerability management is the ongoing process of identifying, assessing, prioritizing, and remediating security vulnerabilities across an organization's IT environment.

Unlike one-time vulnerability assessments, effective vulnerability management is ongoing, providing real-time visibility into exposure and helping teams reduce risk before attackers exploit known weaknesses.

Traditional scanners rely on scheduled scans, network appliances, and credentialed access to assess vulnerabilities periodically.

Vigilant Vulnerability Management uses your existing DeepSafer agents to run automated vulnerability scans, and on-demand scans when you need them, across Windows, macOS, and Linux with no additional infrastructure to deploy or maintain.

No. It uses the same DeepSafer agent already deployed on your endpoints. There is no additional agent to install, no scanner appliance to deploy, and no separate infrastructure to maintain. Enable it through a policy toggle in the Vigilant console and begin scanning immediately.

Vigilant Vulnerability Management ranks vulnerabilities using real-world exploitability signals including EPSS (Exploit Prediction Scoring System) scores, CISA Known Exploited Vulnerabilities (KEV) data, and business criticality factors specific to your environment.

This ensures remediation effort focuses on the vulnerabilities attackers are most likely to target, not just those with the highest CVSS score. S1 Risk Score synthesizes these signals into a single, actionable remediation priority for every vulnerability in your environment.

Yes, through Vigilant Network Control. Network Discovery identifies every device visible on your internal network, including unmanaged endpoints, IoT devices, and assets outside your managed inventory. Vulnerability scanning applies to DeepSafer-protected endpoints. Unmanaged devices can be brought under protection and scanning by deploying a DeepSafer agent directly from the discovery workflow.

Vulnerability management focuses on identifying and remediating known software vulnerabilities across protected assets. Exposure management is a broader discipline that also covers network discovery, asset inventory, and understanding what is visible on your network regardless of whether devices have agents deployed. Vigilant Vulnerability Management addresses the vulnerability layer. Vigilant Network Control extends that picture to the rest of your internal network, including unmanaged devices.

Decorative background gradient

Next Steps

Your Visibility Advantage Starts Here

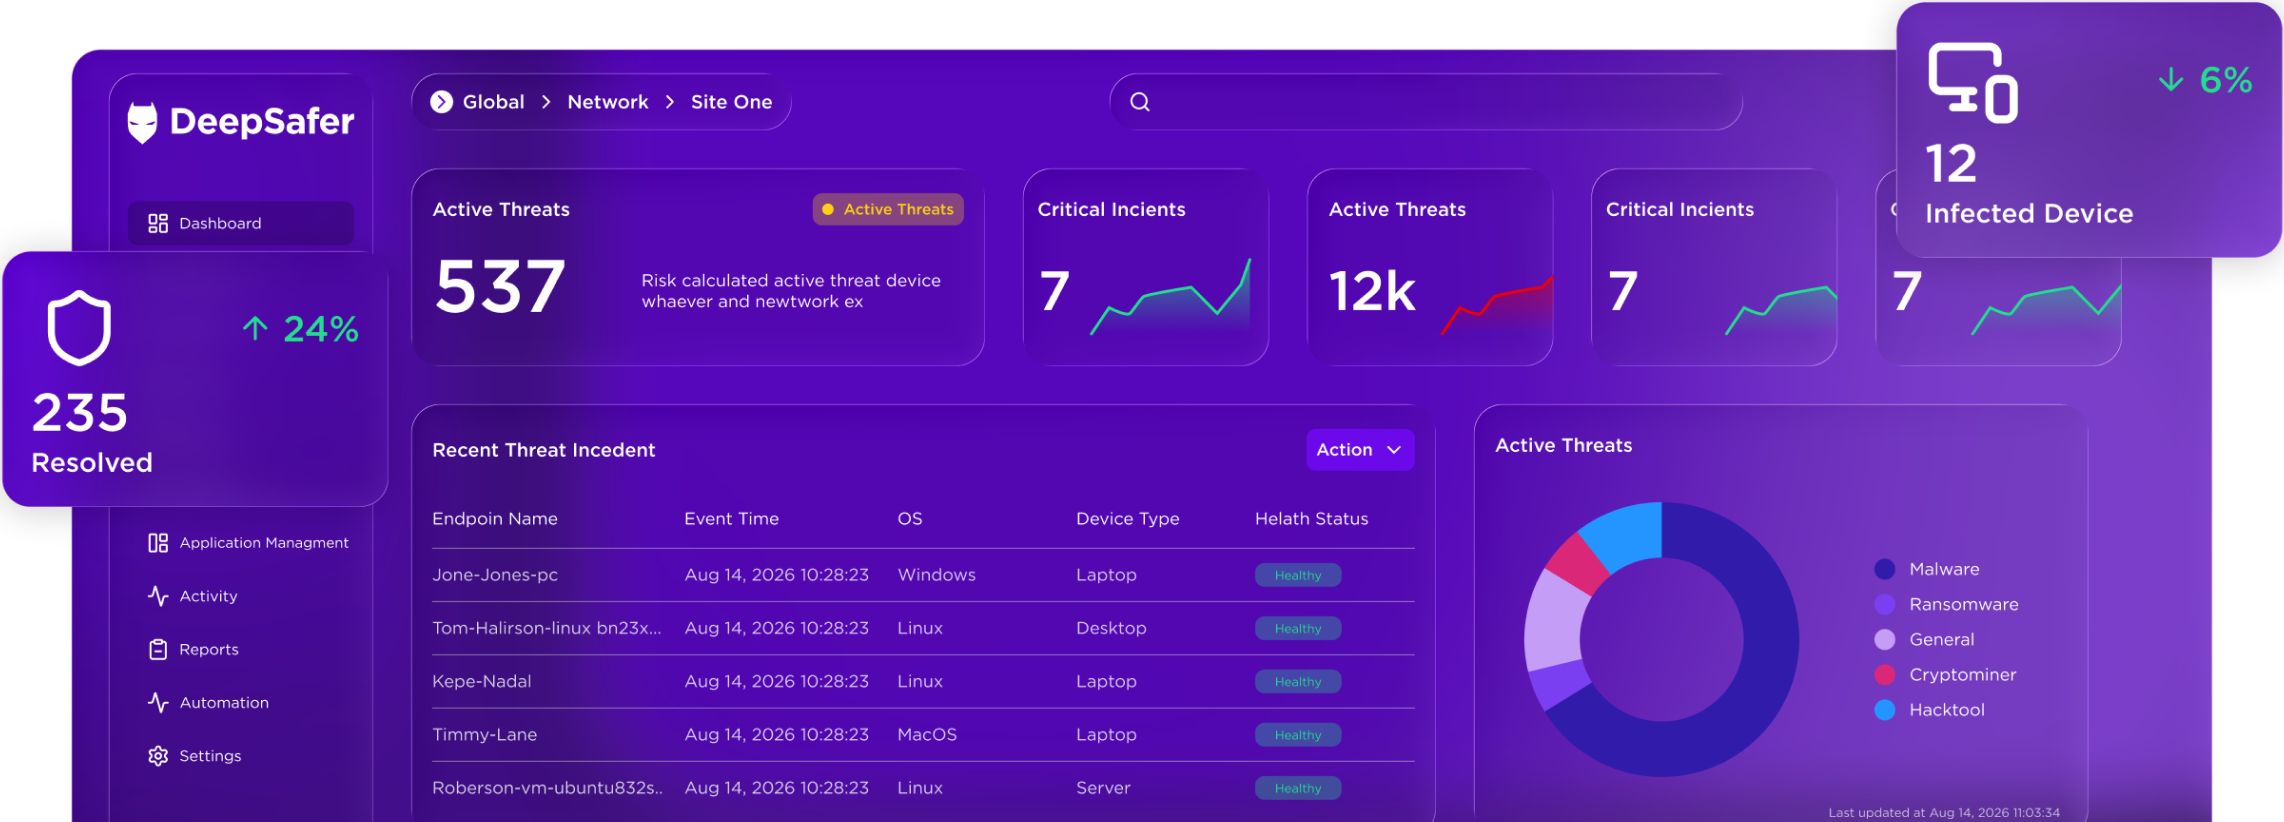
Dark dashboard UI with purple-highlighted nav, summary cards showing 149, 7, 78, 56, 1.2 h, and a status table with linked purple text