Vigilant Insight

Hunt Threats Others Never Even See.

Vigilant Insight is a threat hunting feature that empowers your security team to proactively uncover and investigate hidden threats across your entire digital environment. Leveraging advanced analytics and machine learning, it correlates data from endpoints to identify anomalies and suspicious behavior in real time.

Cybersecurity dashboard UI titled Dashboards; tabs include Overview… Vulnerabilities (selected). Open vulnerabilities chart and Top 10 risky apps table

Today's Reality

01
Man in gray sweater with white earbuds using an open dark laptop indoors; faint “4.5” marker and dotted panel overlay

Detection

Uncover Threats Others Miss

Vigilant Insight continuously monitors your entire environment — endpoints and networks alike — to surface sophisticated threats that traditional security tools overlook.

  • Continuous monitoring across endpoints and networks, with no blind spots

  • Proactively identify and neutralize threats before they escalate

  • Catch what signature-based tools were never built to see
02
Security dashboard “Dashboards” with tabs (Vulnerabilities selected), “Last year” filter, three donut summary cards and a table of CVEs and scores

Intelligence

Automated Hunting, Powered by AI

Advanced machine learning and behavioral analytics automatically detect and surface hidden threats — freeing your analysts to hunt the most covert attacks.

  • Machine learning surfaces anomalies and suspicious behavior in real time

  • Advanced analytics process massive data volumes to reveal hidden patterns

  • Reduce alert fatigue so your team focuses on what matters

03
Dark security dashboard in a browser showing “Vulnerabilities” with a filter bar, CVE/severity chips, and a table listing assets and “Critical” alerts

Response

Investigate and Respond, Faster

Real-time insights and detailed analytics let your team investigate incidents and respond in seconds — cutting response times and limiting damage before it spreads.

  • Real-time insights accelerate every investigation from alert to action

  • Reduce response times and mitigate damage before it grows

  • Design custom detection rules with advanced hunting queries

04
Man with laptop on light green sofa in bright lobby; translucent overlay lines and faint “Oct. 2014” text near right center

Visualization

See the Attack Unfold

The Vigilant Threat Map turns complex data into a clear visual story — tracing every attack sequence so analysts can pinpoint exactly where and how a threat took hold.

  • Visualize full attack sequences to trace how threats progress

  • Pinpoint critical points of compromise across the attack chain

  • Understand adversary tactics through a clear visual narrative

Decorative background gradient

Get Started

Symmetrical 3D geometric open box of glossy translucent panels around a glowing light-blue cube on a white background

Use Cases

One Agent. Multiple Outcomes.

Know What You Have. Protect What Matters.

Scheduled and on-demand vulnerability scanning across every protected endpoint, with Vigilant Network Controlo identify coverage gaps of unmanaged devices.

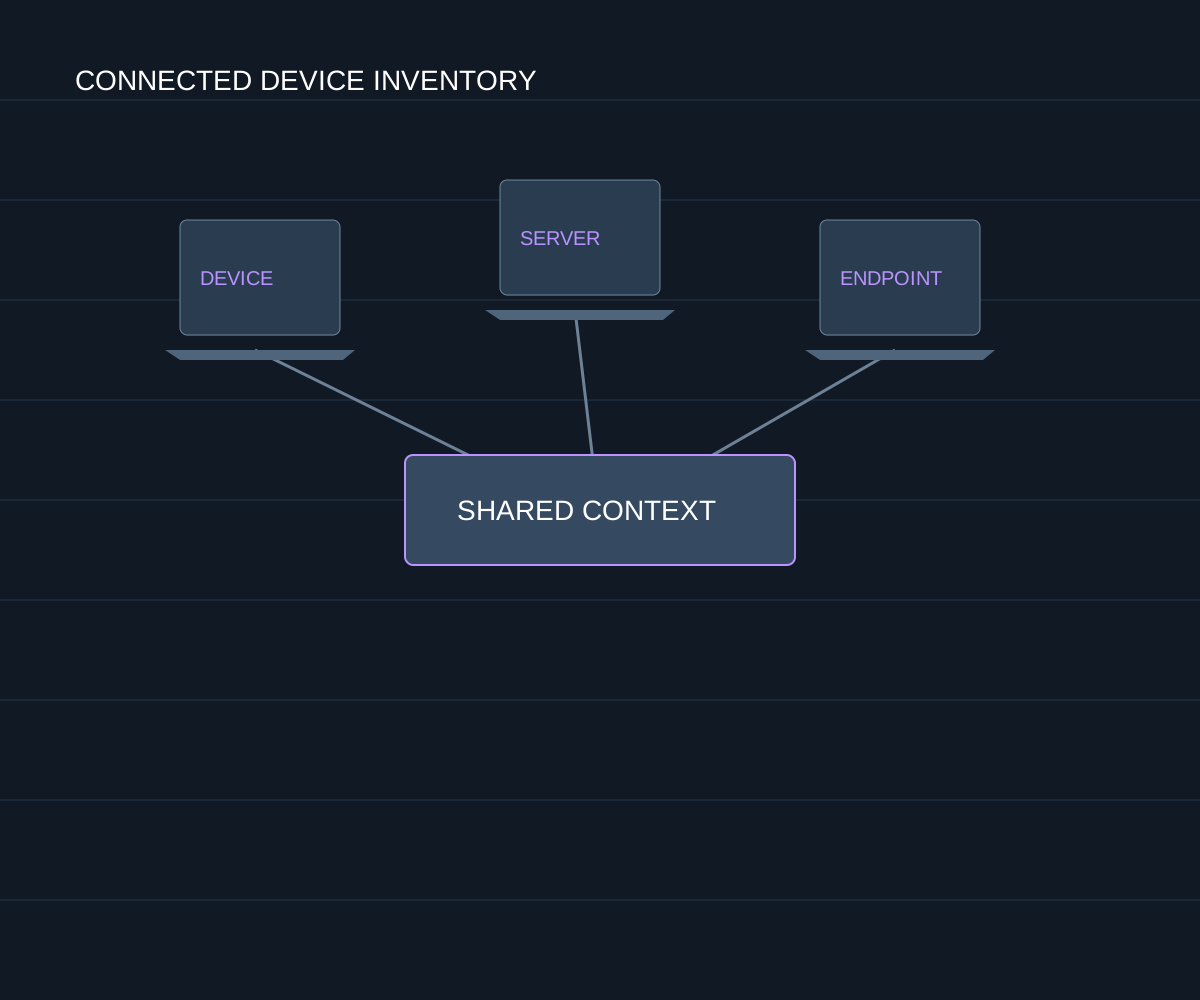
Connected device inventory and shared security context

Managed Endpoints

Assess application and OS vulnerabilities across your entire managed fleet with automated scans.

Explore the Platform
IT professional using a laptop in a distributed workspace

Distributed Environments

Cover remote, hybrid, and branch office endpoints with agent-based visibility that doesn't require network access or proximity to a scanner.

Explore the Platform
Router, switch and laptop representing devices on an enterprise network

Unmanaged Devices

Discover endpoints operating outside your managed inventory, including IoT devices, personal devices, and unknown assets.

Explore the Platform

Investigation outcomes

From scattered activity to a clearer investigation.

Vigilant Insight focuses on understanding events, connecting context, and supporting analyst decisions. Explore a workflow for reviewing suspicious activity.

  1. 01

    Trace

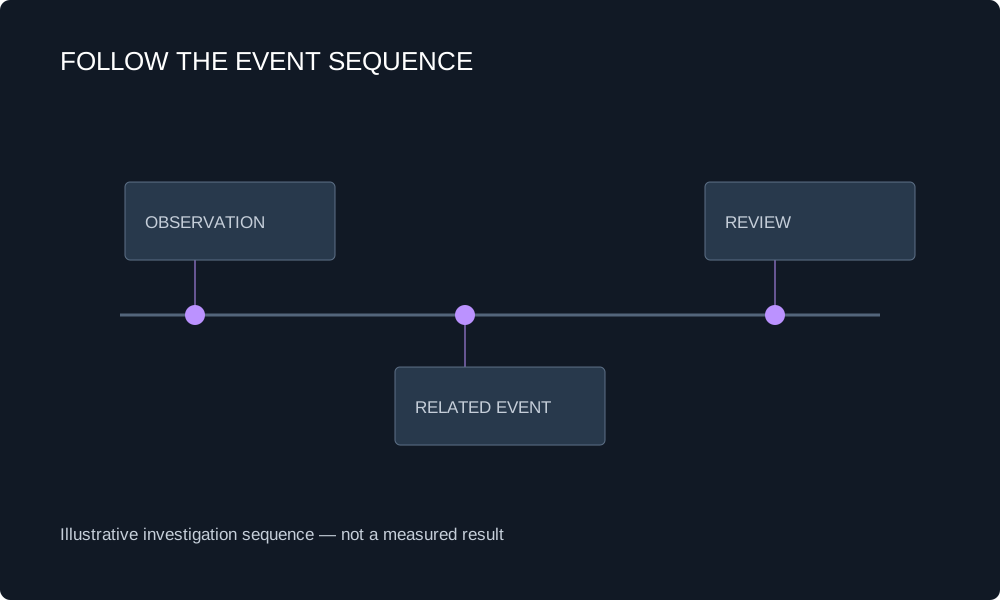
    Review the sequence around suspicious activity to understand what happened before and after an event.

    Illustrative timeline connecting observations, related events, and review
  2. 02

    Connect

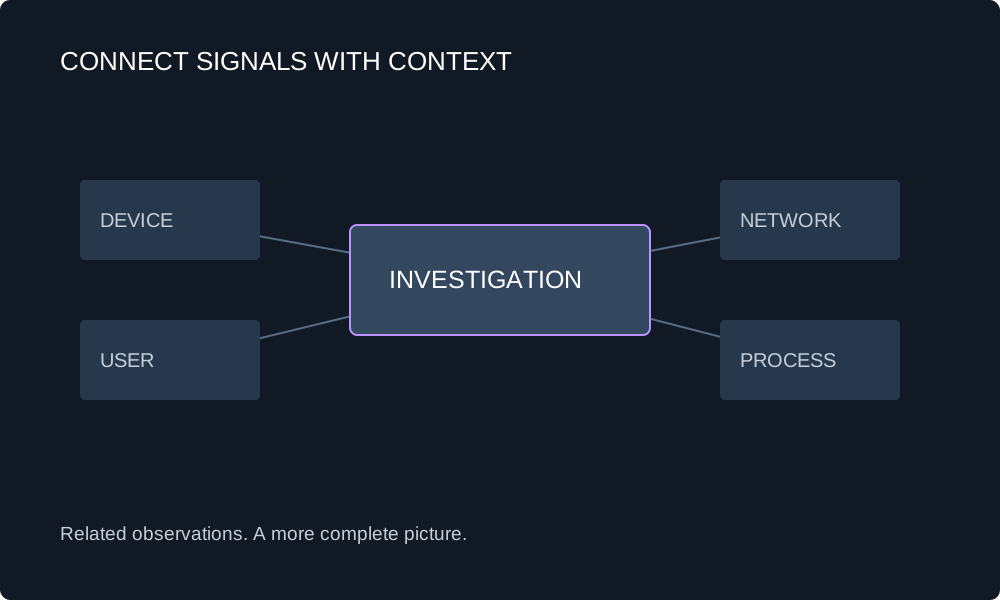
    Bring device, user, network, and process context together to build a clearer investigation picture.

    Device, user, network, and process context connected to an investigation
  3. 03

    Review

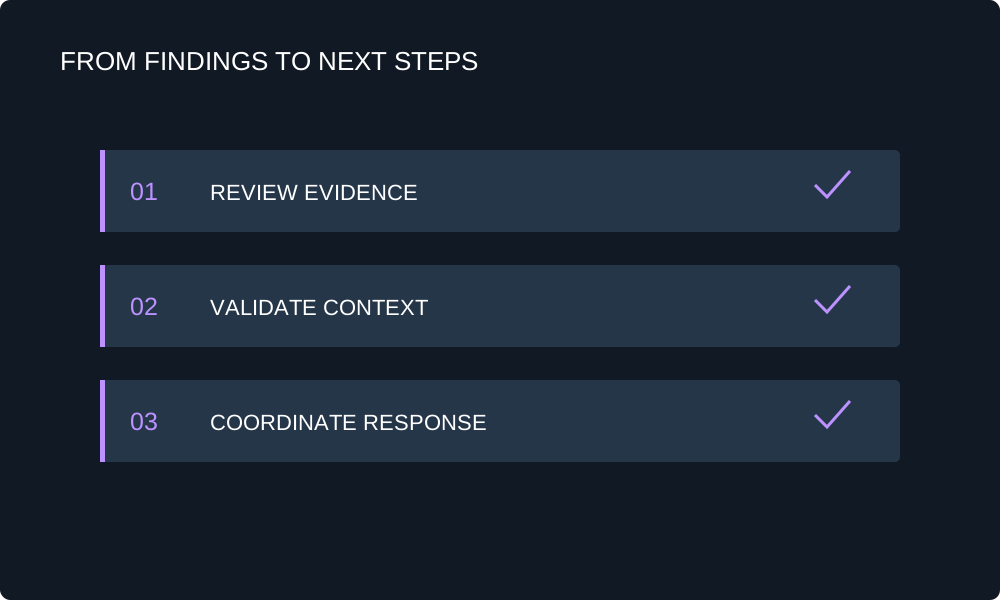
    Organize findings, validate the evidence, and share the context needed to coordinate next steps.

    Review queue for evidence, context validation, and coordinated response

Customer & industry focus

Security for the organizations that connect Yemen.

From telecom infrastructure to mobile services, explore local security priorities and the DeepSafer capabilities that address them.
Yemen Mobile telecommunications tower and site

Clearer context for endpoint investigations.

Yemen Mobile

Mobile services & endpoint protection

Connect device events and related activity to guide investigation and help security teams identify what needs follow-up.


Explore the solution
TeleYemen building and telecommunications tower

Trace events across telecom infrastructure.

TeleYemen

Telecommunications & infrastructure

Review event sequences and supporting context to understand suspicious activity across systems and services.


Explore the solution
YOU company building with its yellow facade and logo

Organize findings. Decide the next step.

YOU

Yemen Omani United telecommunications

Bring related evidence together and share context with operations teams to support review and coordinated response.


Explore the solution

Why DeepSafer

More Than Just a Scanner. A Built-In Advantage.

Vulnerability management built into the AI-native DeepSafer agent on every DeepSafer-protected endpoint. No separate scanner. No bolted-on tool.
IT professional working on an unbranded laptop beside an office window

Nothing New to Deploy. Nothing New to Manage.

Your existing DeepSafer agents become your vulnerability sensors. No new infrastructure required.

Flat technical diagram representing scheduled and on-demand checks

Automated Scanning. On-Demand When You Need It.

Automated vulnerability scans run across your protected fleet on a regular cadence. Trigger on-demand scans any time.

Hands using a laptop at a practical security operations workspace

Lower Cost of Ownership

Eliminate the licensing, infrastructure, and maintenance overhead of a standalone scanner. One vendor. One platform. One agent.

Illustrative review queue for exposure, context and next steps

Fix What Attackers Actually Target

Prioritize using EPSS scores, CISA KEV data, and business criticality to focus effort where it reduces the most risk.

Office network infrastructure and connected workspaces

Discover Your Full Internal Network

Discover unmanaged endpoints, IoT devices, and deployment gaps to map your true attack surface.

Platform Integration

One Platform. A Singular Advantage.

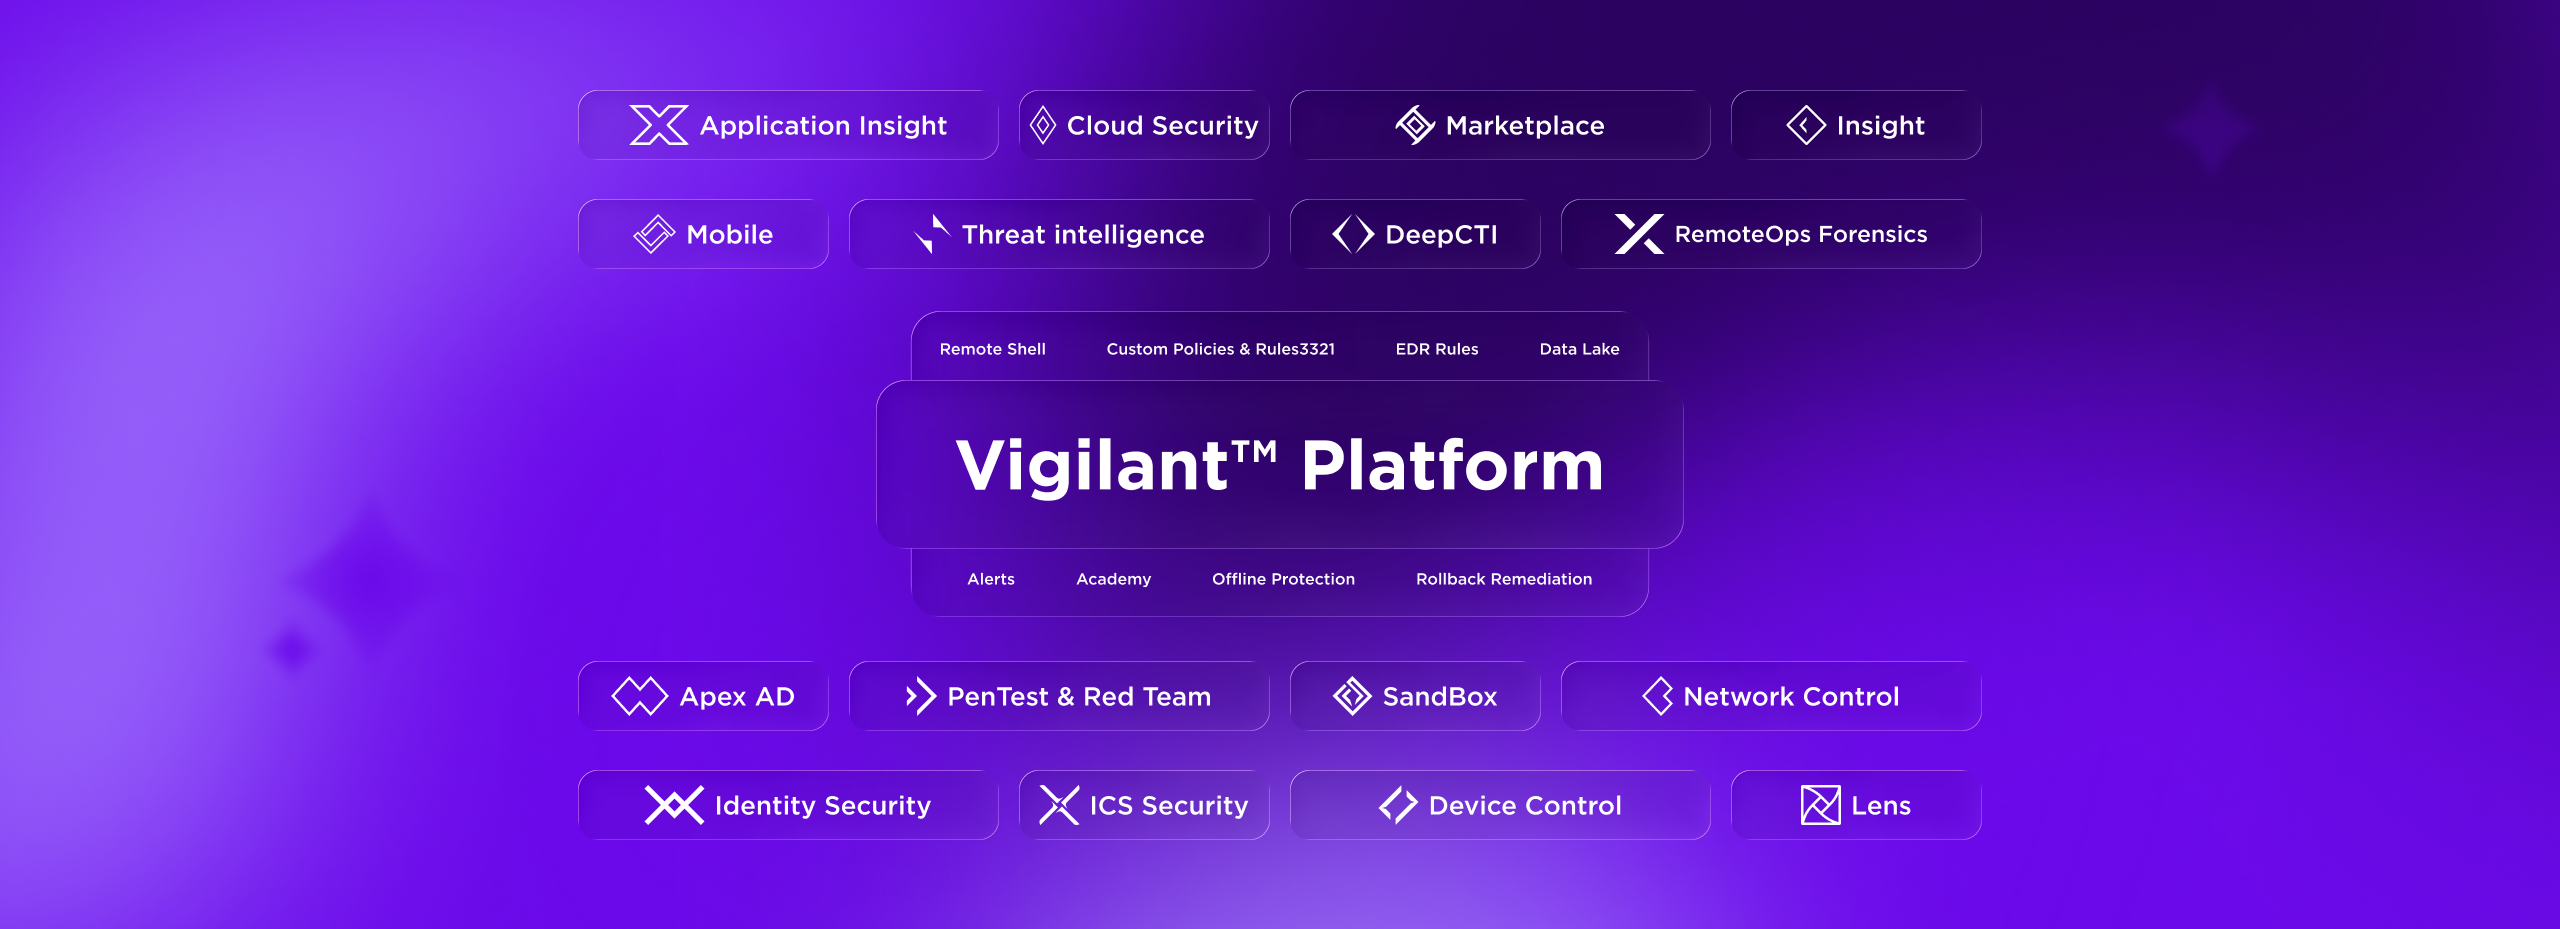
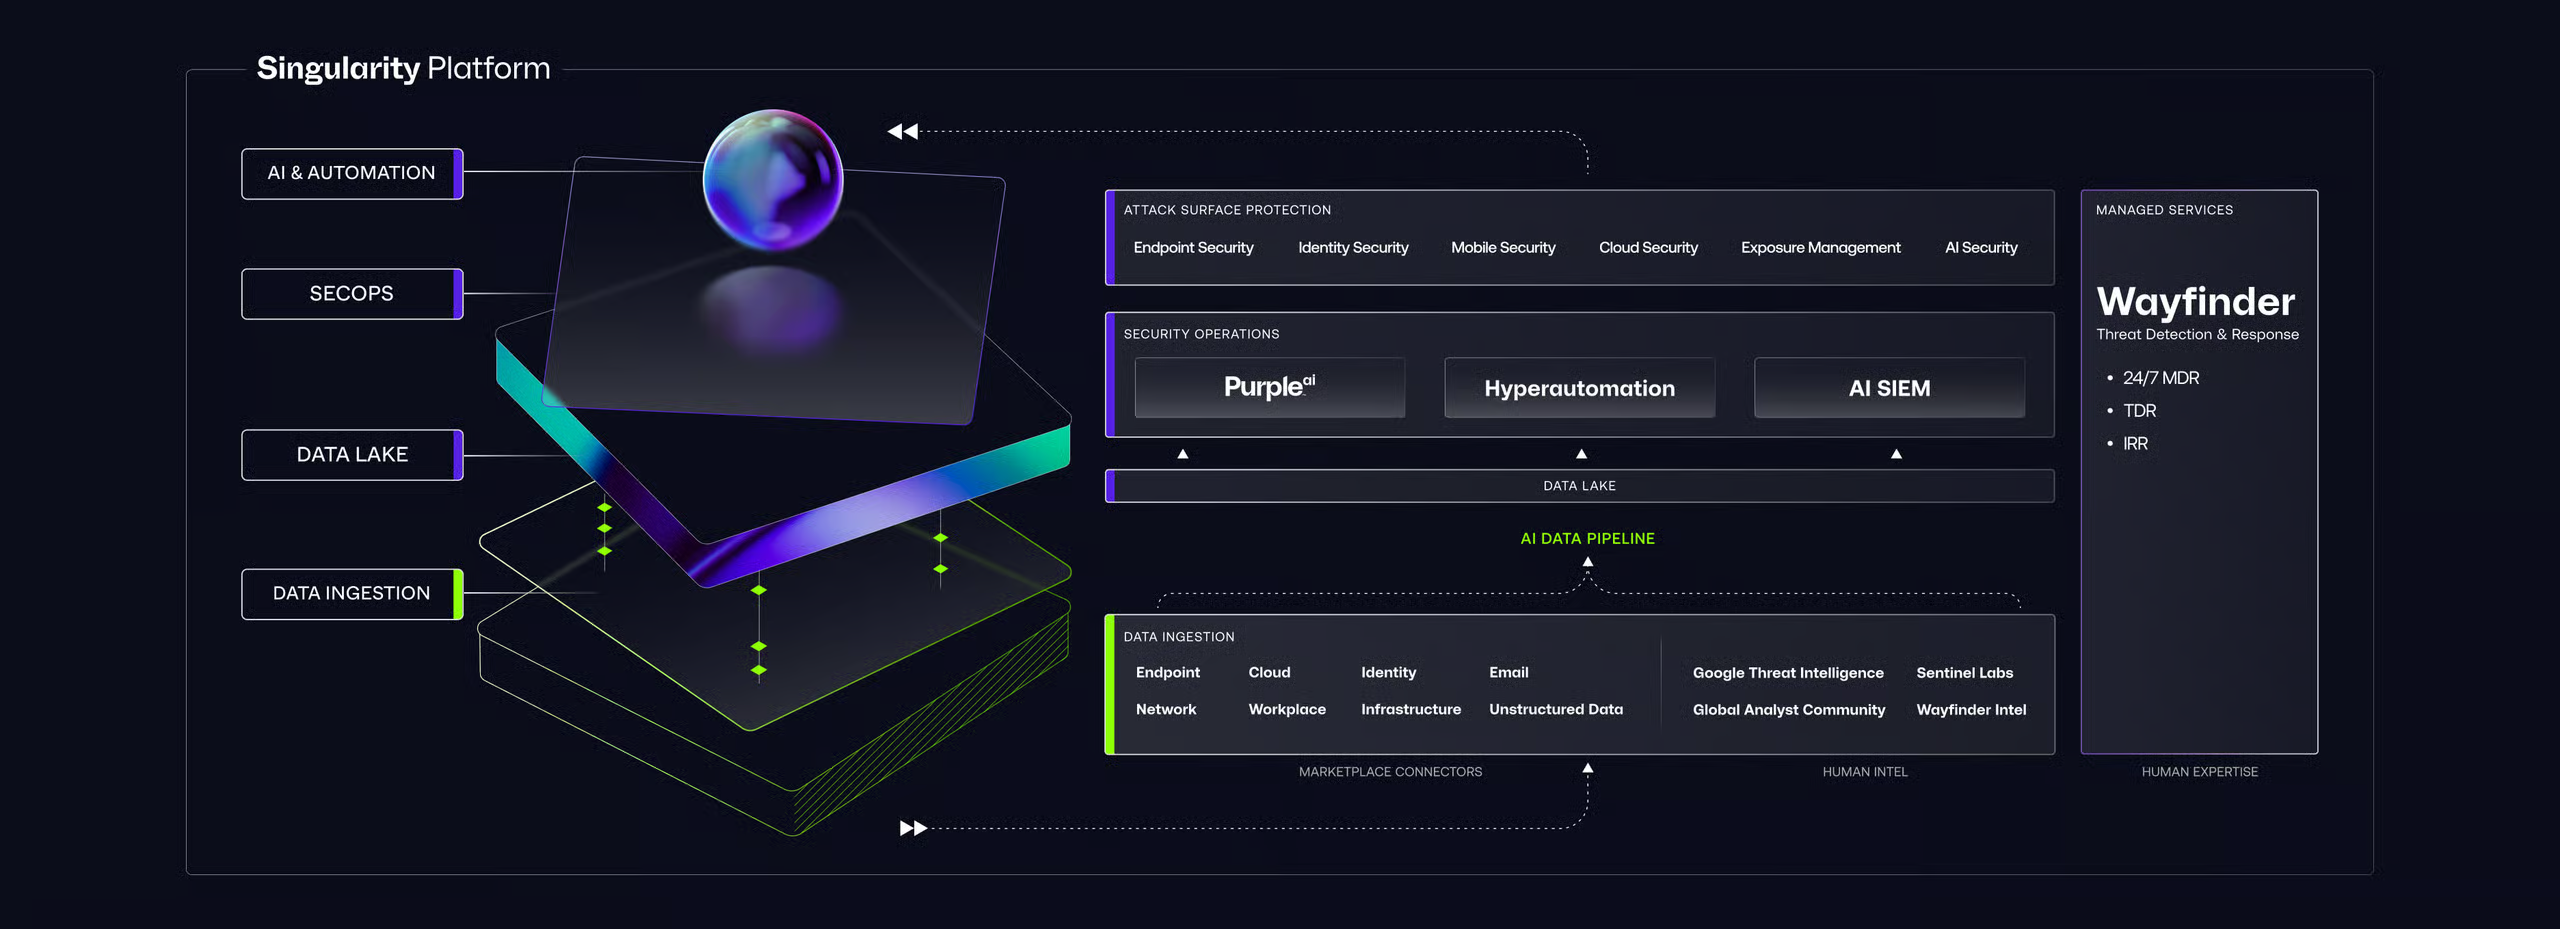
Futuristic UI mockup titled “Vigilant Platform” with neon platform, orb, labeled sections, and sidebar “DeepSafer”
01

From Detection to Prevention

Find exposures and stop the threats targeting them. Same AI-native agent. Same console.

02

Context That Drives Faster Response

Correlate exploit attempts with known vulnerabilities to prioritize response by real-world risk.

03

Consolidated Workflows. Fewer Tools.

Manage endpoint protection and vulnerability scanning from a single console. One place to investigate, prioritize, and act. No tool switching required.

Getting Started

Gain the Advantage from Day One

Futuristic UI mockup titled “Vigilant Platform” with neon platform, orb, labeled sections, and sidebar “DeepSafer”
Setup

Activate with the Agent You Already Have

Enable vulnerability management across your fleet with a policy toggle. No new agents, no appliances, no deployment project.

Build

Configure Policies. See Results Immediately.

Set scan depth, scope, and frequency by policy. Vulnerabilities surface in real time alongside your endpoint data.

Evolve

Expand Coverage. Focus on What Matters.

Discover unmanaged assets, close deployment gaps, and refine prioritization as your environment grows.

Need Answers?

Frequently Asked Questions

Vulnerability management is the ongoing process of identifying, assessing, prioritizing, and remediating security vulnerabilities across an organization's IT environment.

Unlike one-time vulnerability assessments, effective vulnerability management is ongoing, providing real-time visibility into exposure and helping teams reduce risk before attackers exploit known weaknesses.

Traditional scanners rely on scheduled scans, network appliances, and credentialed access to assess vulnerabilities periodically.

Vigilant Vulnerability Management uses your existing DeepSafer agents to run automated vulnerability scans, and on-demand scans when you need them, across Windows, macOS, and Linux with no additional infrastructure to deploy or maintain.

No. It uses the same DeepSafer agent already deployed on your endpoints. There is no additional agent to install, no scanner appliance to deploy, and no separate infrastructure to maintain. Enable it through a policy toggle in the Vigilant console and begin scanning immediately.

Vigilant Vulnerability Management ranks vulnerabilities using real-world exploitability signals including EPSS (Exploit Prediction Scoring System) scores, CISA Known Exploited Vulnerabilities (KEV) data, and business criticality factors specific to your environment.

This ensures remediation effort focuses on the vulnerabilities attackers are most likely to target, not just those with the highest CVSS score. S1 Risk Score synthesizes these signals into a single, actionable remediation priority for every vulnerability in your environment.

Yes, through Vigilant Network Control. Network Discovery identifies every device visible on your internal network, including unmanaged endpoints, IoT devices, and assets outside your managed inventory. Vulnerability scanning applies to DeepSafer-protected endpoints. Unmanaged devices can be brought under protection and scanning by deploying a DeepSafer agent directly from the discovery workflow.

Vulnerability management focuses on identifying and remediating known software vulnerabilities across protected assets. Exposure management is a broader discipline that also covers network discovery, asset inventory, and understanding what is visible on your network regardless of whether devices have agents deployed. Vigilant Vulnerability Management addresses the vulnerability layer. Vigilant Network Control extends that picture to the rest of your internal network, including unmanaged devices.

Decorative background gradient

Next Steps

Your Visibility Advantage Starts Here

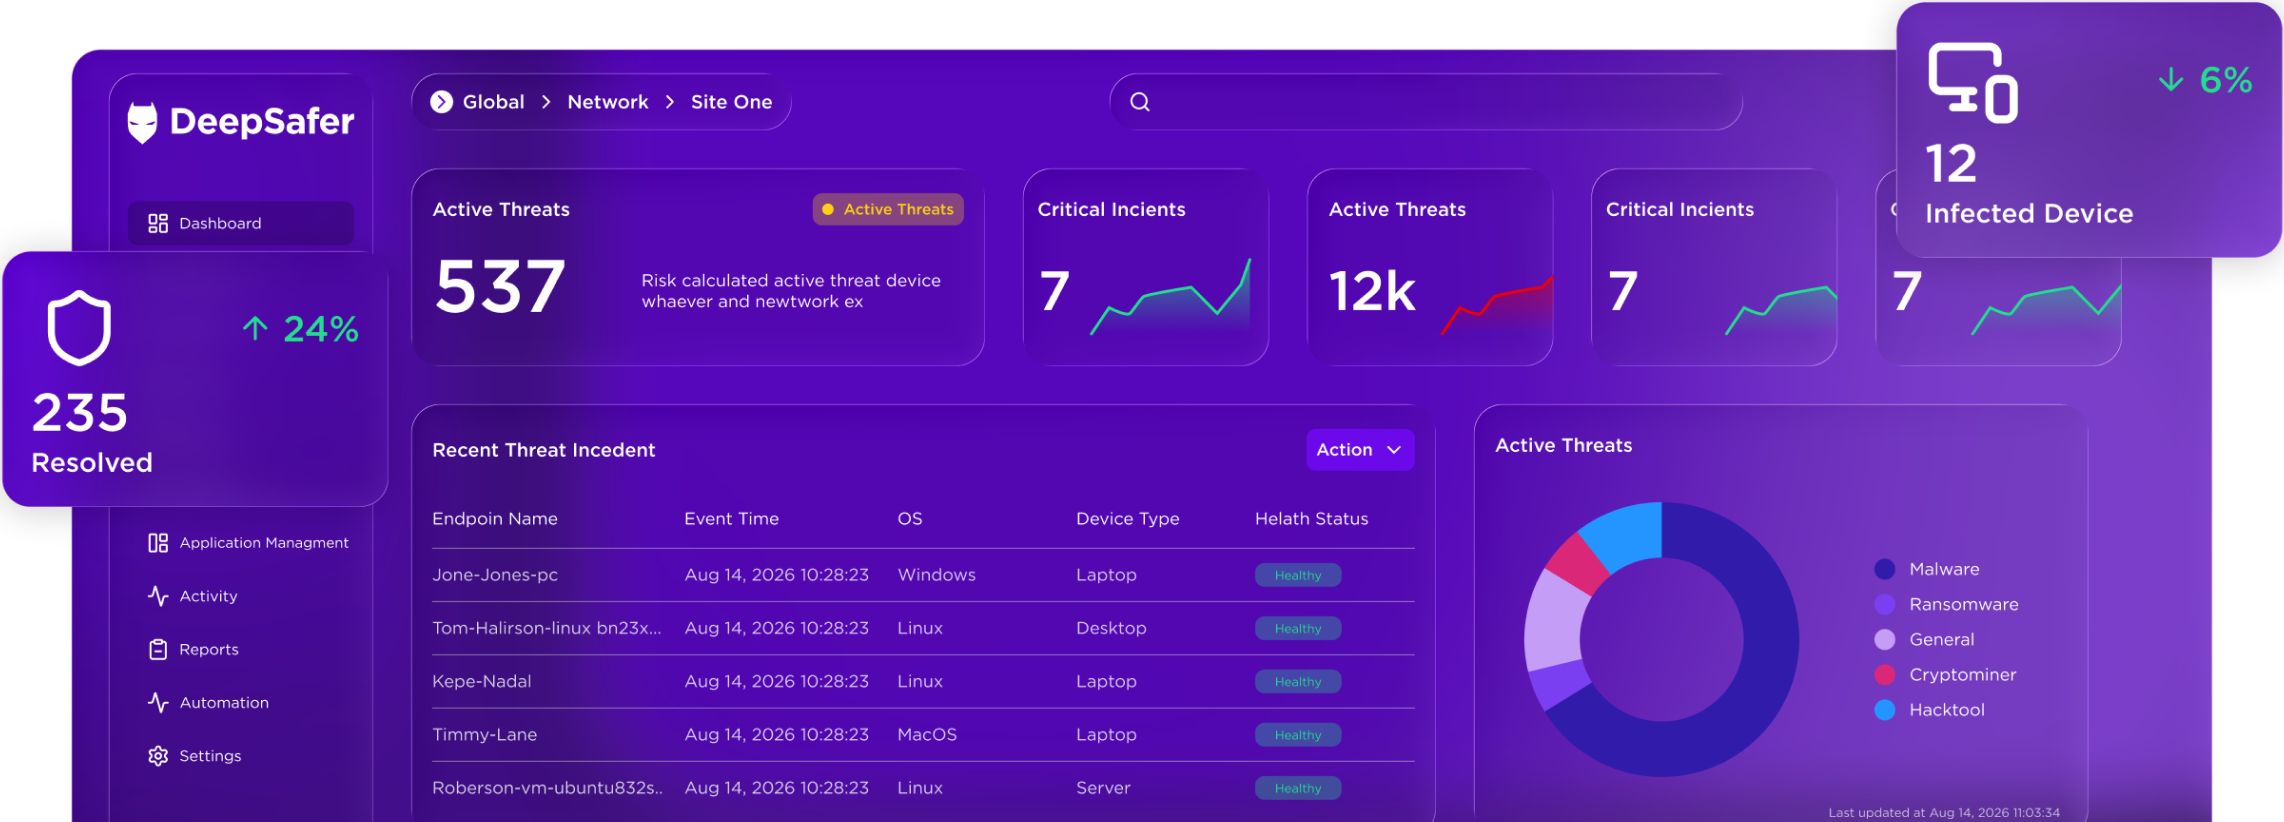
Dark dashboard UI with purple-highlighted nav, summary cards showing 149, 7, 78, 56, 1.2 h, and a status table with linked purple text