Advanced Malware Analysis & Virtual Detonation
Threats Revealed. Peace Secured. Upload. Analyze. Neutralize.
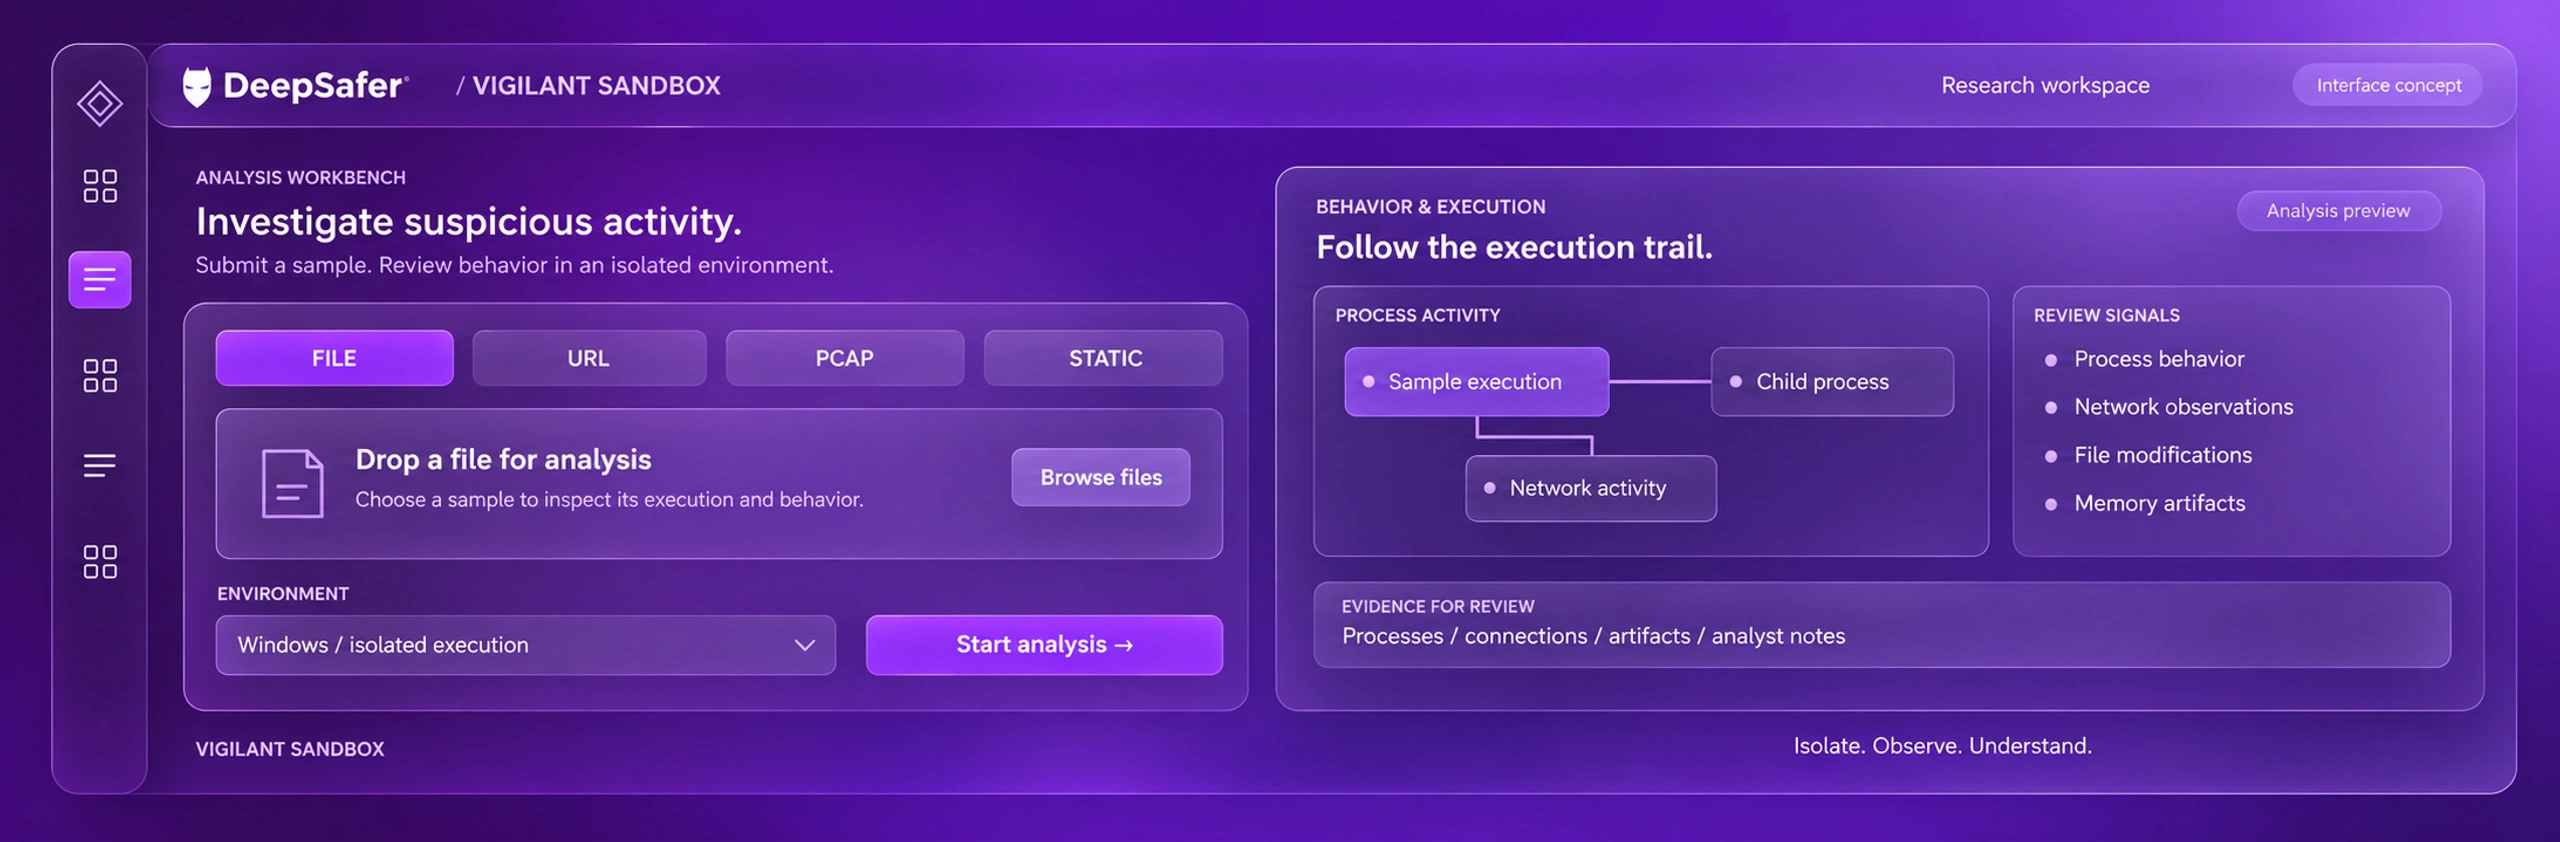
The Vigilant Sandbox is an airtight virtual detonation environment engineered to deconstruct suspicious files, weaponized documents, malicious URLs, and zero-day behaviors in real time. Empower your SOC, incident responders, and threat hunters with deep kernel visibility, memory dumping, and MITRE ATT&CK mapping with zero risk to enterprise infrastructure.
Trusted by


Advanced Analysis Engine
Intelligent Virtual Detonation for Complex Threats
Vigilant Sandbox combines multi-OS interactive detonation, hypervisor-level kernel
inspection, and automated MITRE ATT&CK mapping into one unified platform.
Kernel-Level Deep Memory Inspection
Automated MITRE ATT&CK & IOC Extraction
Use Cases
Actionable Intelligence for Every Security Team
From rapid SOC triage to deep forensic investigations and automated email scanning,
Vigilant Sandbox delivers instant clarity.
Accelerate SOC Triage & Incident Investigation
Phishing URL & Redirection Analysis
Digital Forensics & DFIR Investigations
Automated Pipeline & API Ingestion
The DeepSafer Advantage
Proactive Cyber Resilience & Autonomous Neutralization
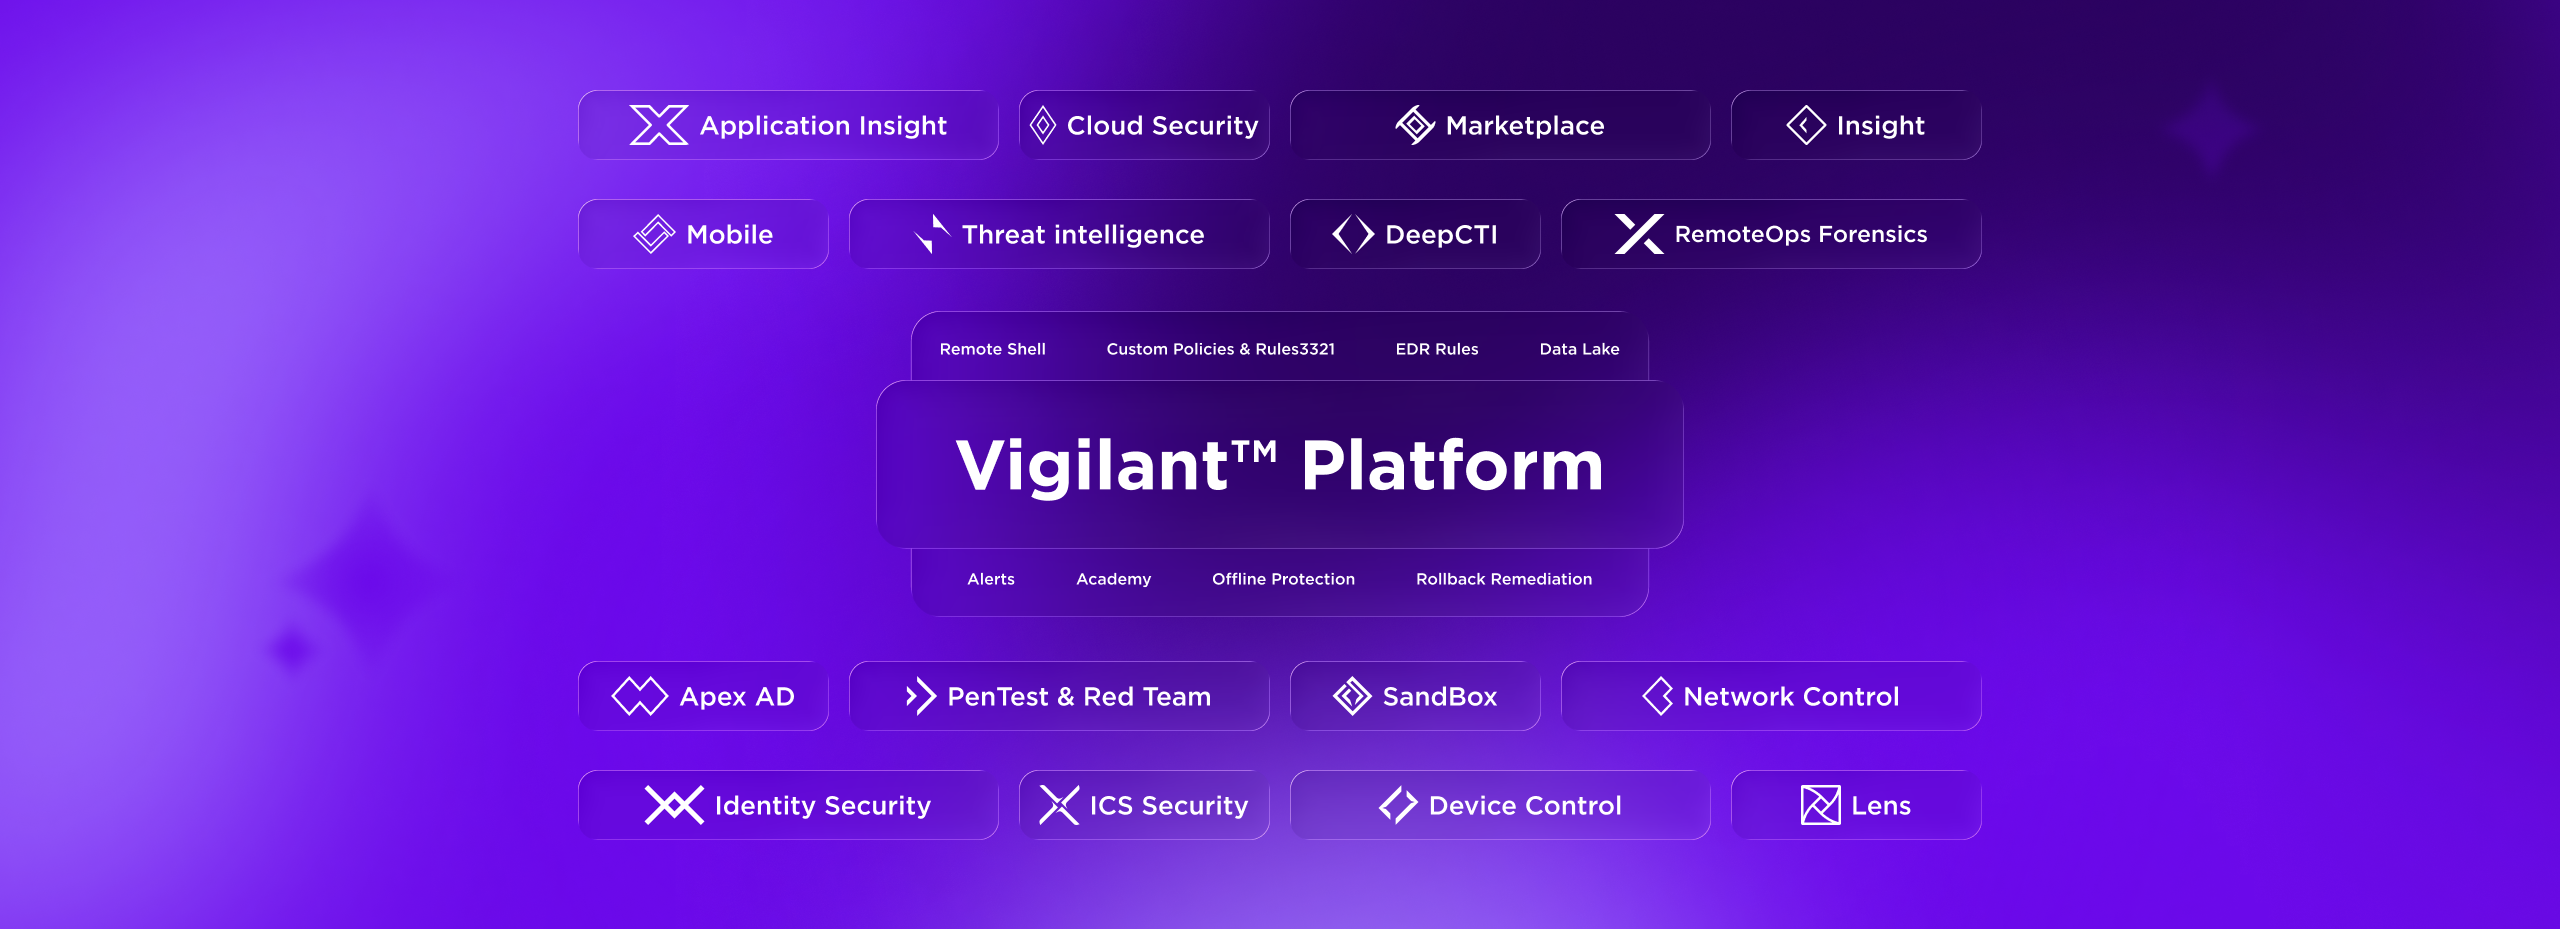
Airtight Anti-Evasion Hypervisor
Hypervisor-level deception and sleep-acceleration defeat sophisticated malware checks, forcing execution of true payload behaviors.
Enterprise-Wide Instant Response
Extracted IOCs and signatures are broadcasted across all Vigilant Platform endpoints in real time to prevent lateral infection enterprise-wide.
Comprehensive Forensic Artifact Exports
One-click export of YARA rules, Snort/Suricata signatures, STIX/TAXII threat feeds, and executive-ready forensic PDF summaries.
Got Questions?
Frequently Asked Questions about Vigilant Sandbox
Next Steps
Detonate Safely. Uncover Hidden Threats.