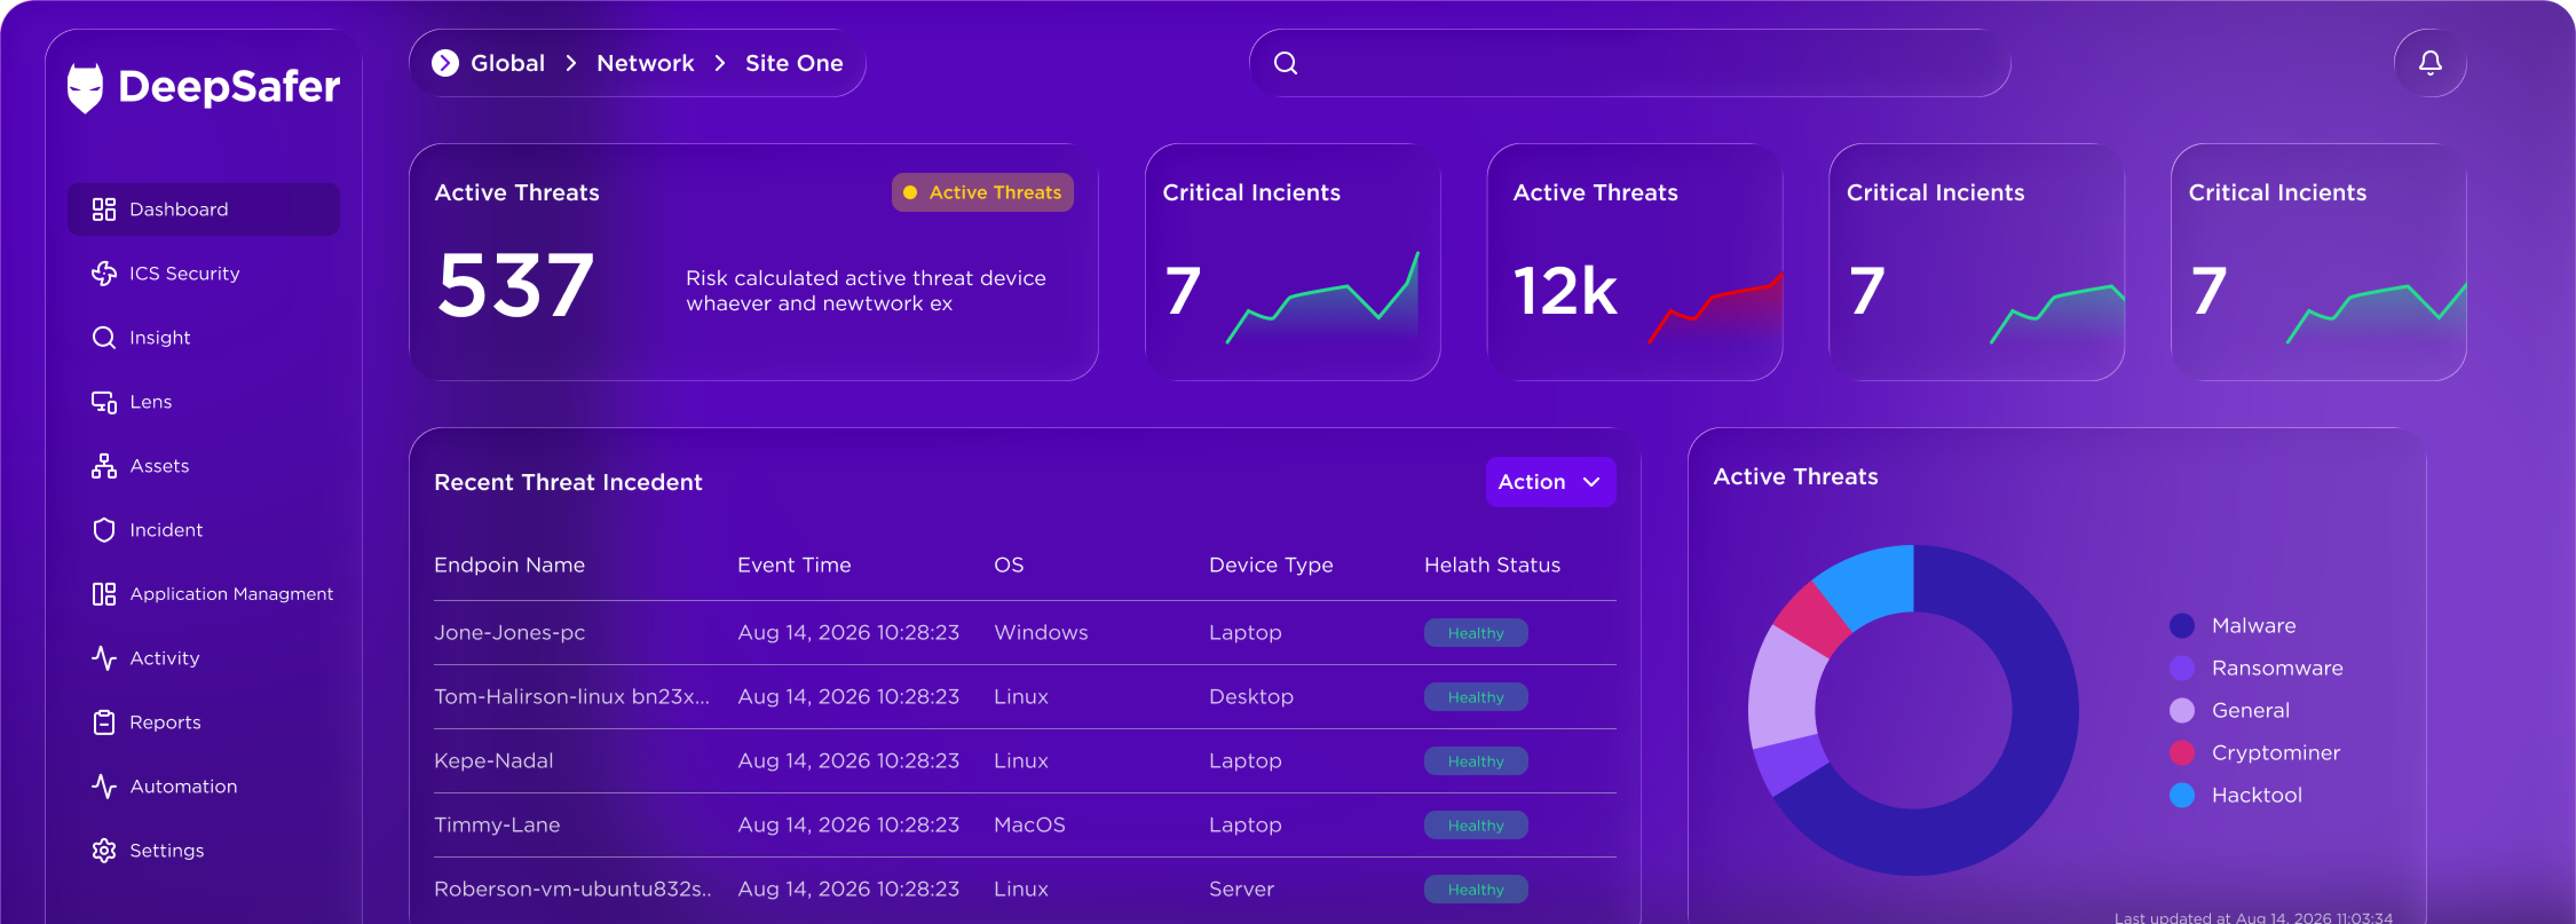
24/7 Real-Time Threat Detection
24/7 monitoring across endpoints, networks, and cloud environments using AI-powered threat detection.
Vigilant MDR + DFIR
In a world where cyber threats are constantly evolving, you need more than just detection—you need a partner who can respond, investigate, and protect. DeepSafer’s Vigilant MDR + DFIR combines 24x7 Managed Detection and Response (MDR) deliver end-to-end cybersecurity.
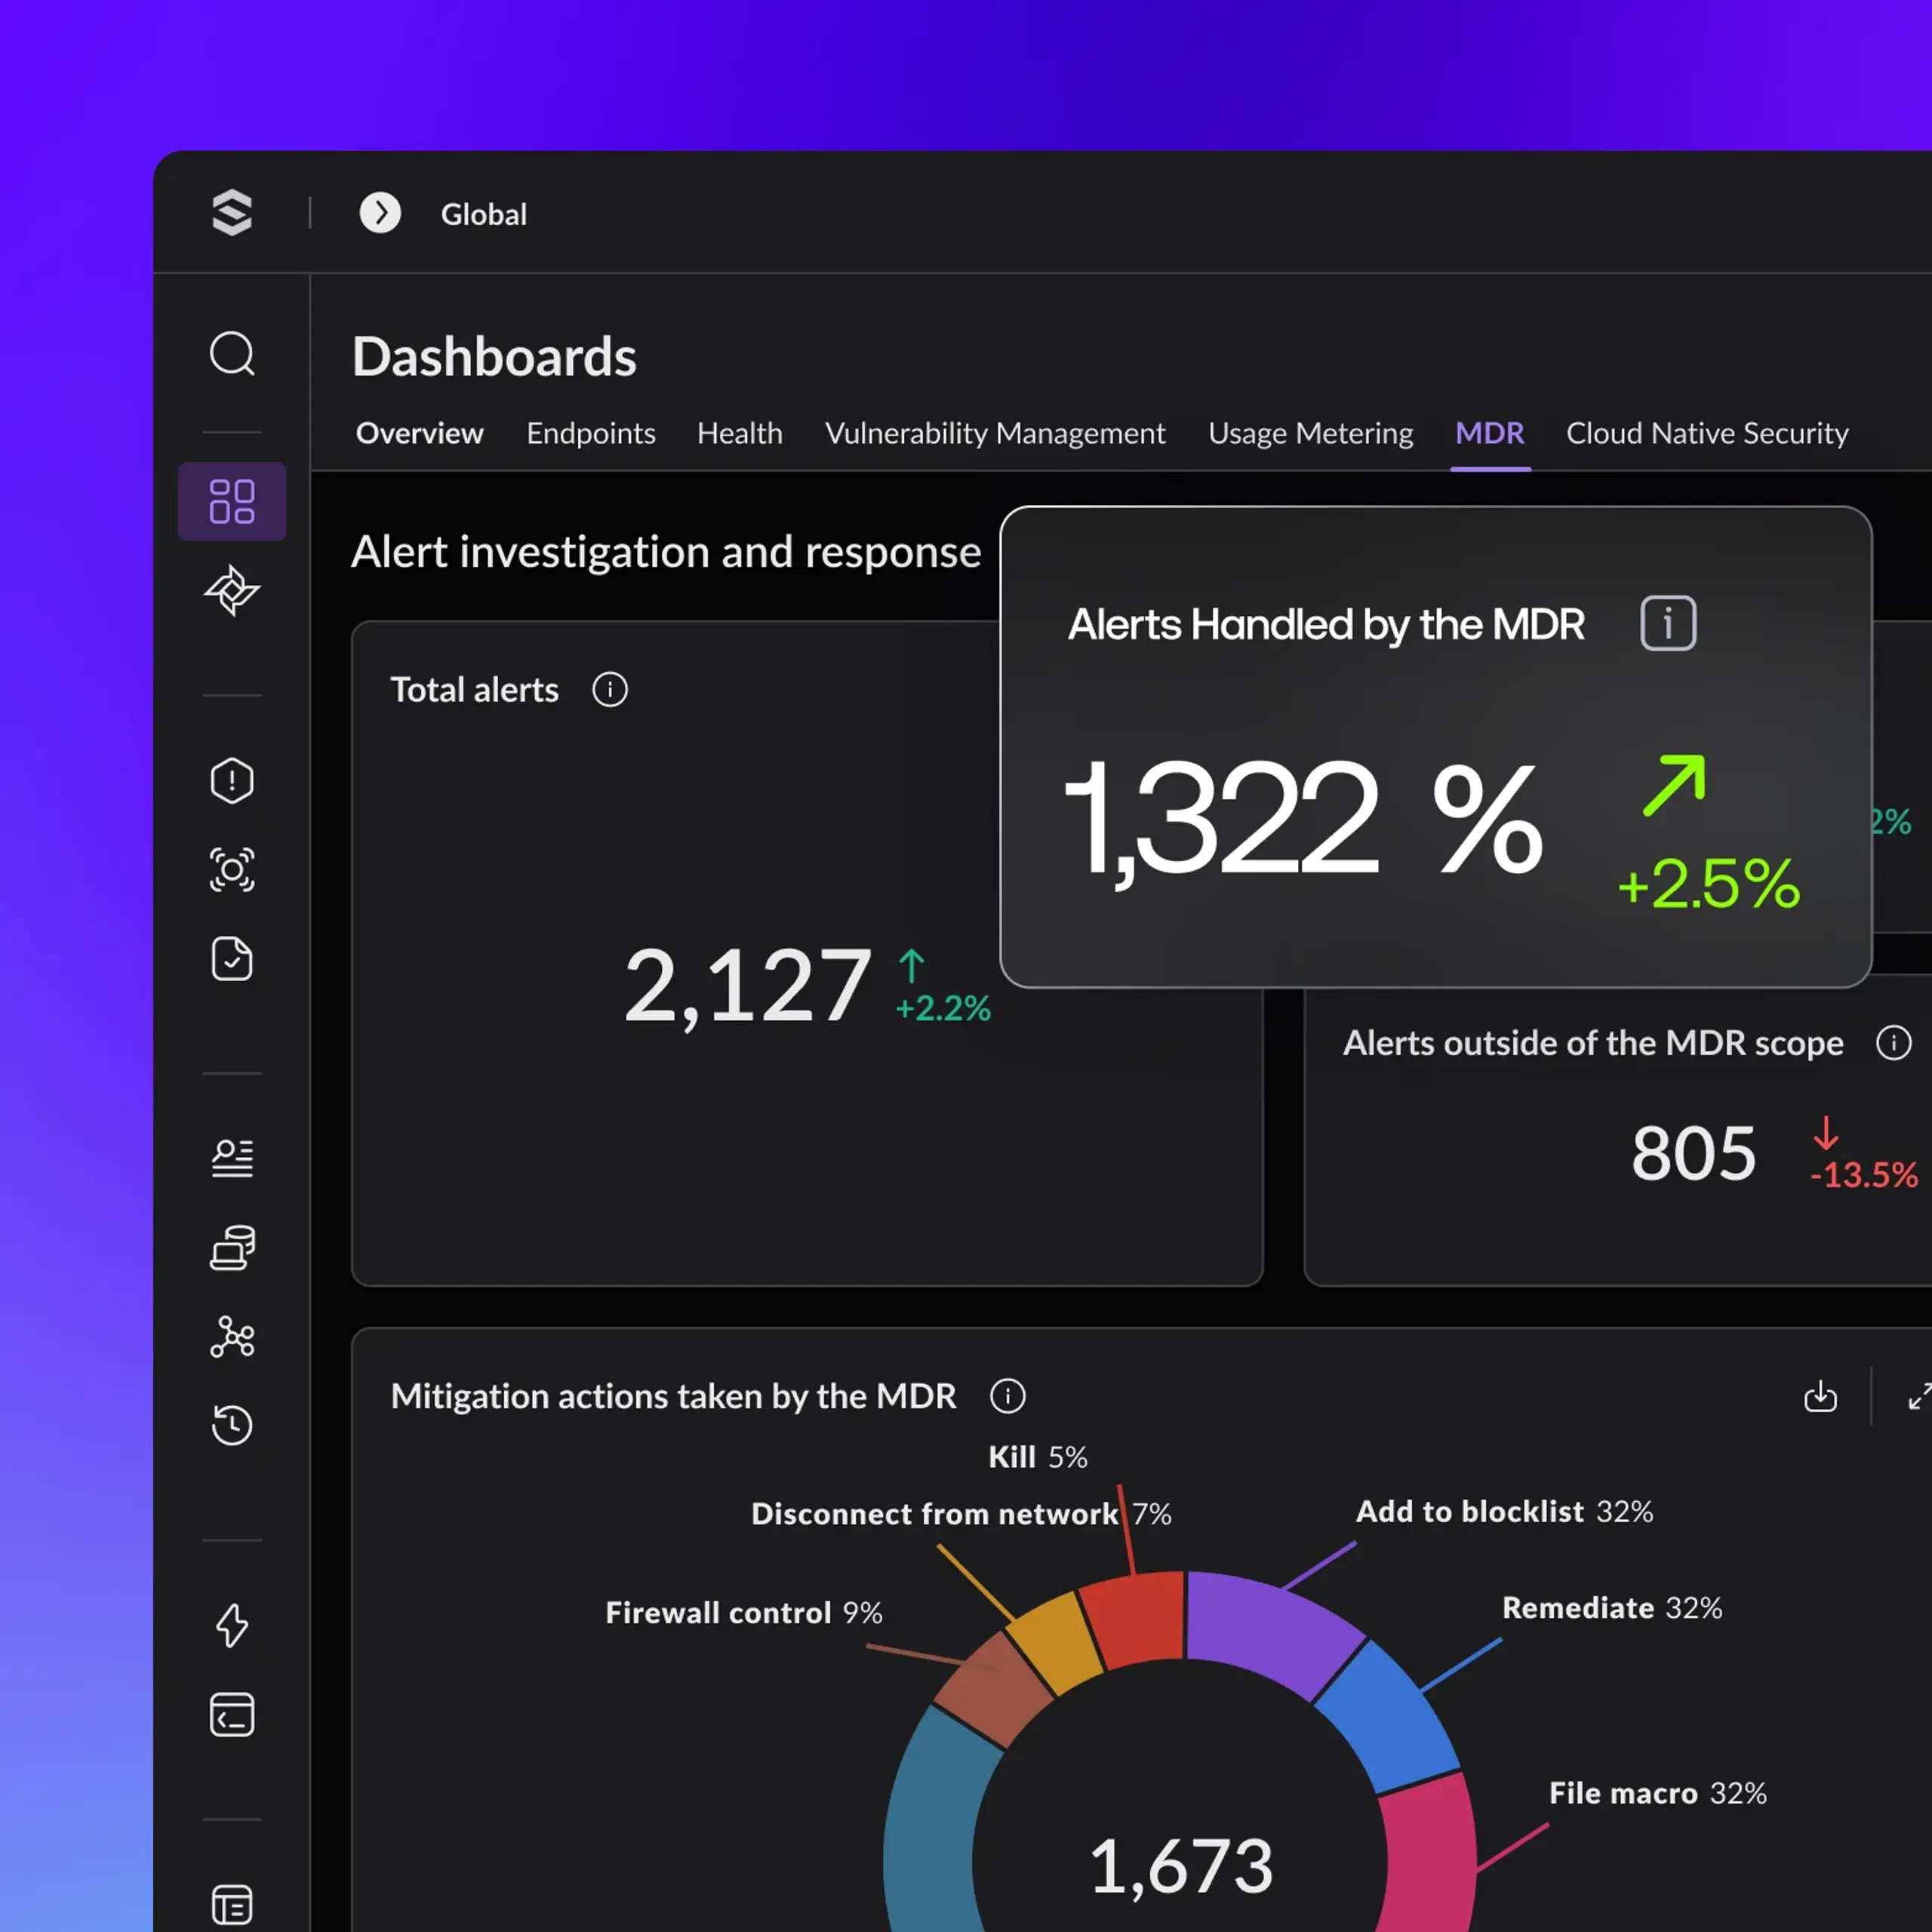
The MDR Advantage
24/7 monitoring across endpoints, networks, and cloud environments using AI-powered threat detection.
Elite experts hunt hidden threats, analyze patterns, and neutralize risks before they escalate.
Immediate containment, investigation, and remediation to minimize damage and ensure business resilience.
Discuss coverage, supported systems, escalation responsibilities, and response expectations with the DeepSafer team. The service scope should reflect your environment and operational requirements.
Why Choose Vigilant MDR+DIFR?
Proactive management of threat detection and response processes to ensure immediate protection and minimize damage.
Advanced digital investigations to analyze security incidents, delivering accurate responses and effective recovery plans to contain threats.
Round-the-clock monitoring by a specialized security team to identify threats and provide immediate response.
Proactive investigation of undetected threats using advanced analytical methods to uncover malicious activities.
Specialized technical support to resolve security issues quickly and efficiently, either on-site or remotely.
In-depth analysis of the quality and efficiency of your digital infrastructure, helping to identify strengths and weaknesses.
Getting Started
Vigilant MDR delivers round-the-clock monitoring across endpoints, cloud workloads, identities, and networks, giving you continuous visibility into your entire attack surface without a single blind spot.
24/7 monitoring across endpoints, cloud, and identity. Behavioral AI and Google Threat Intelligence surface threats in real time. Average time to detect: 3.3 minutes.
Every alert is investigated by certified analysts, not automated playbooks. Purple AI enriches context. Human experts confirm severity. False positives are filtered before they reach your team.
Confirmed threats are contained at machine speed. Malicious processes are killed, endpoints are isolated, and unauthorized changes are rolled back. Confirmed threats are contained at machine speed, according to your configured response policy.
Full incident context is delivered to your team with recommended next steps. For critical incidents, DFIR experts are available for rapid containment and forensic recovery.
The DeepSafer Portfolio
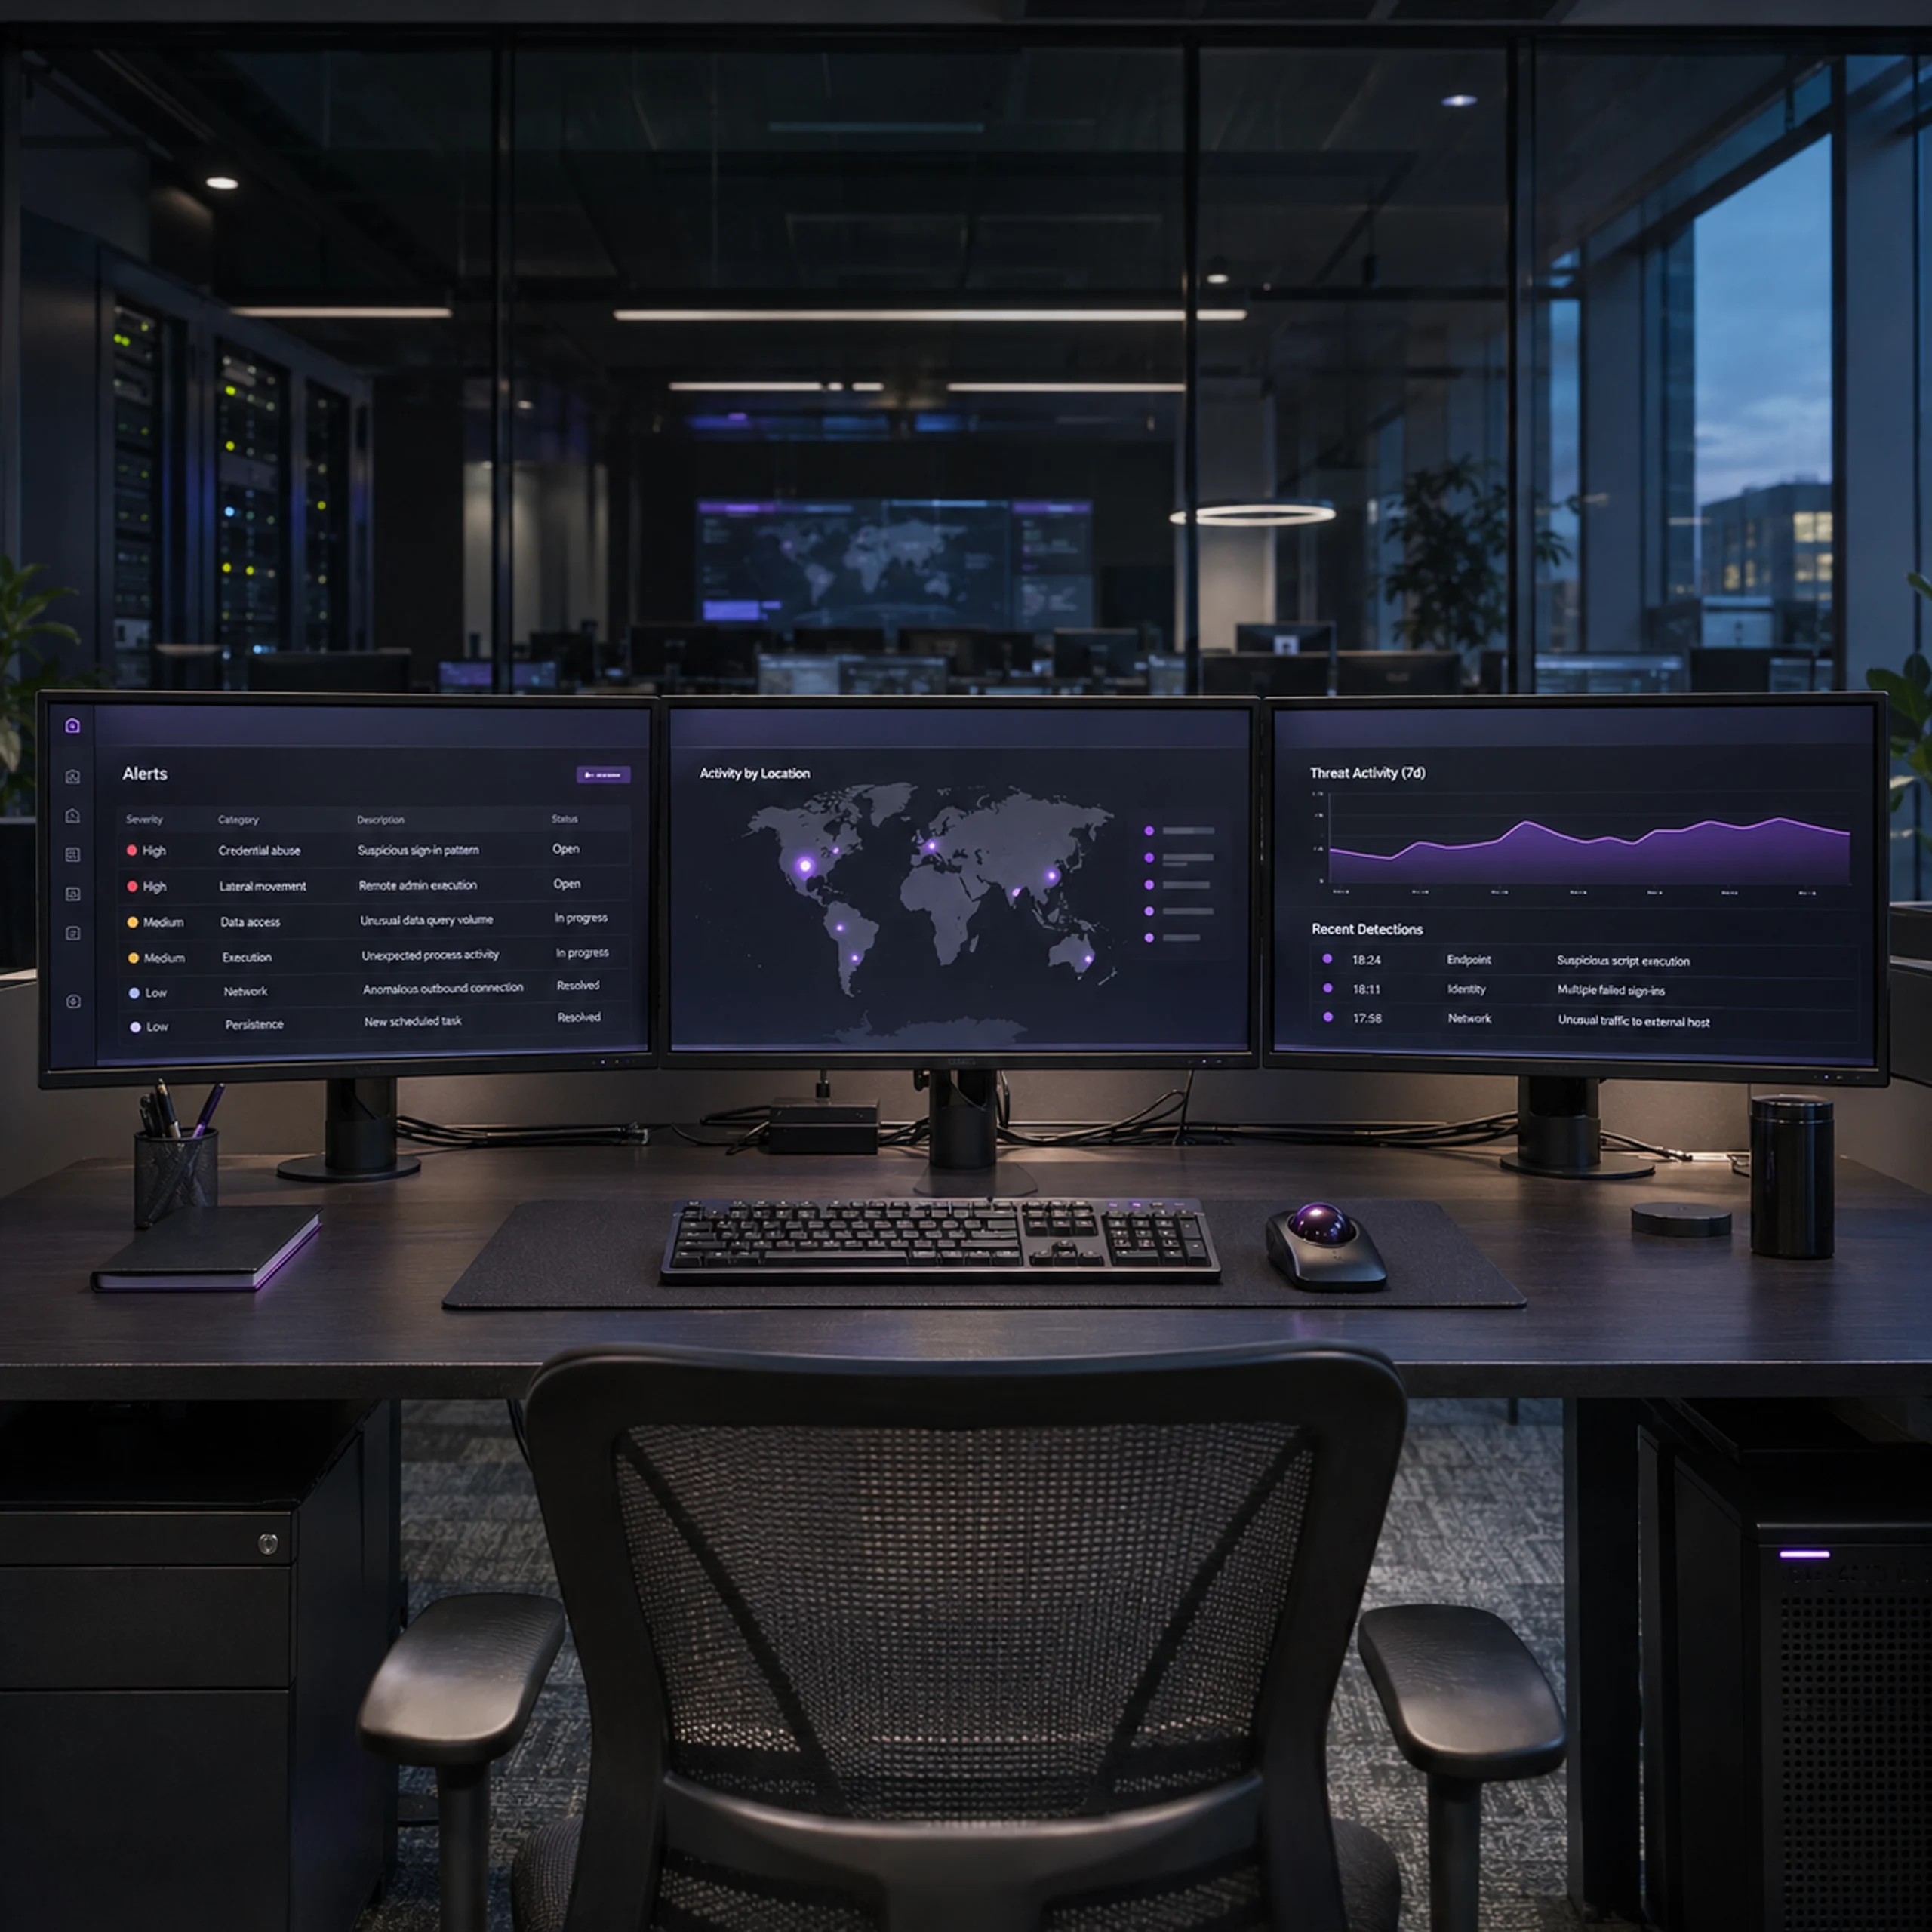
Discuss coverage, supported systems, escalation responsibilities, and response expectations with the DeepSafer team. The service scope should reflect your environment and operational requirements.
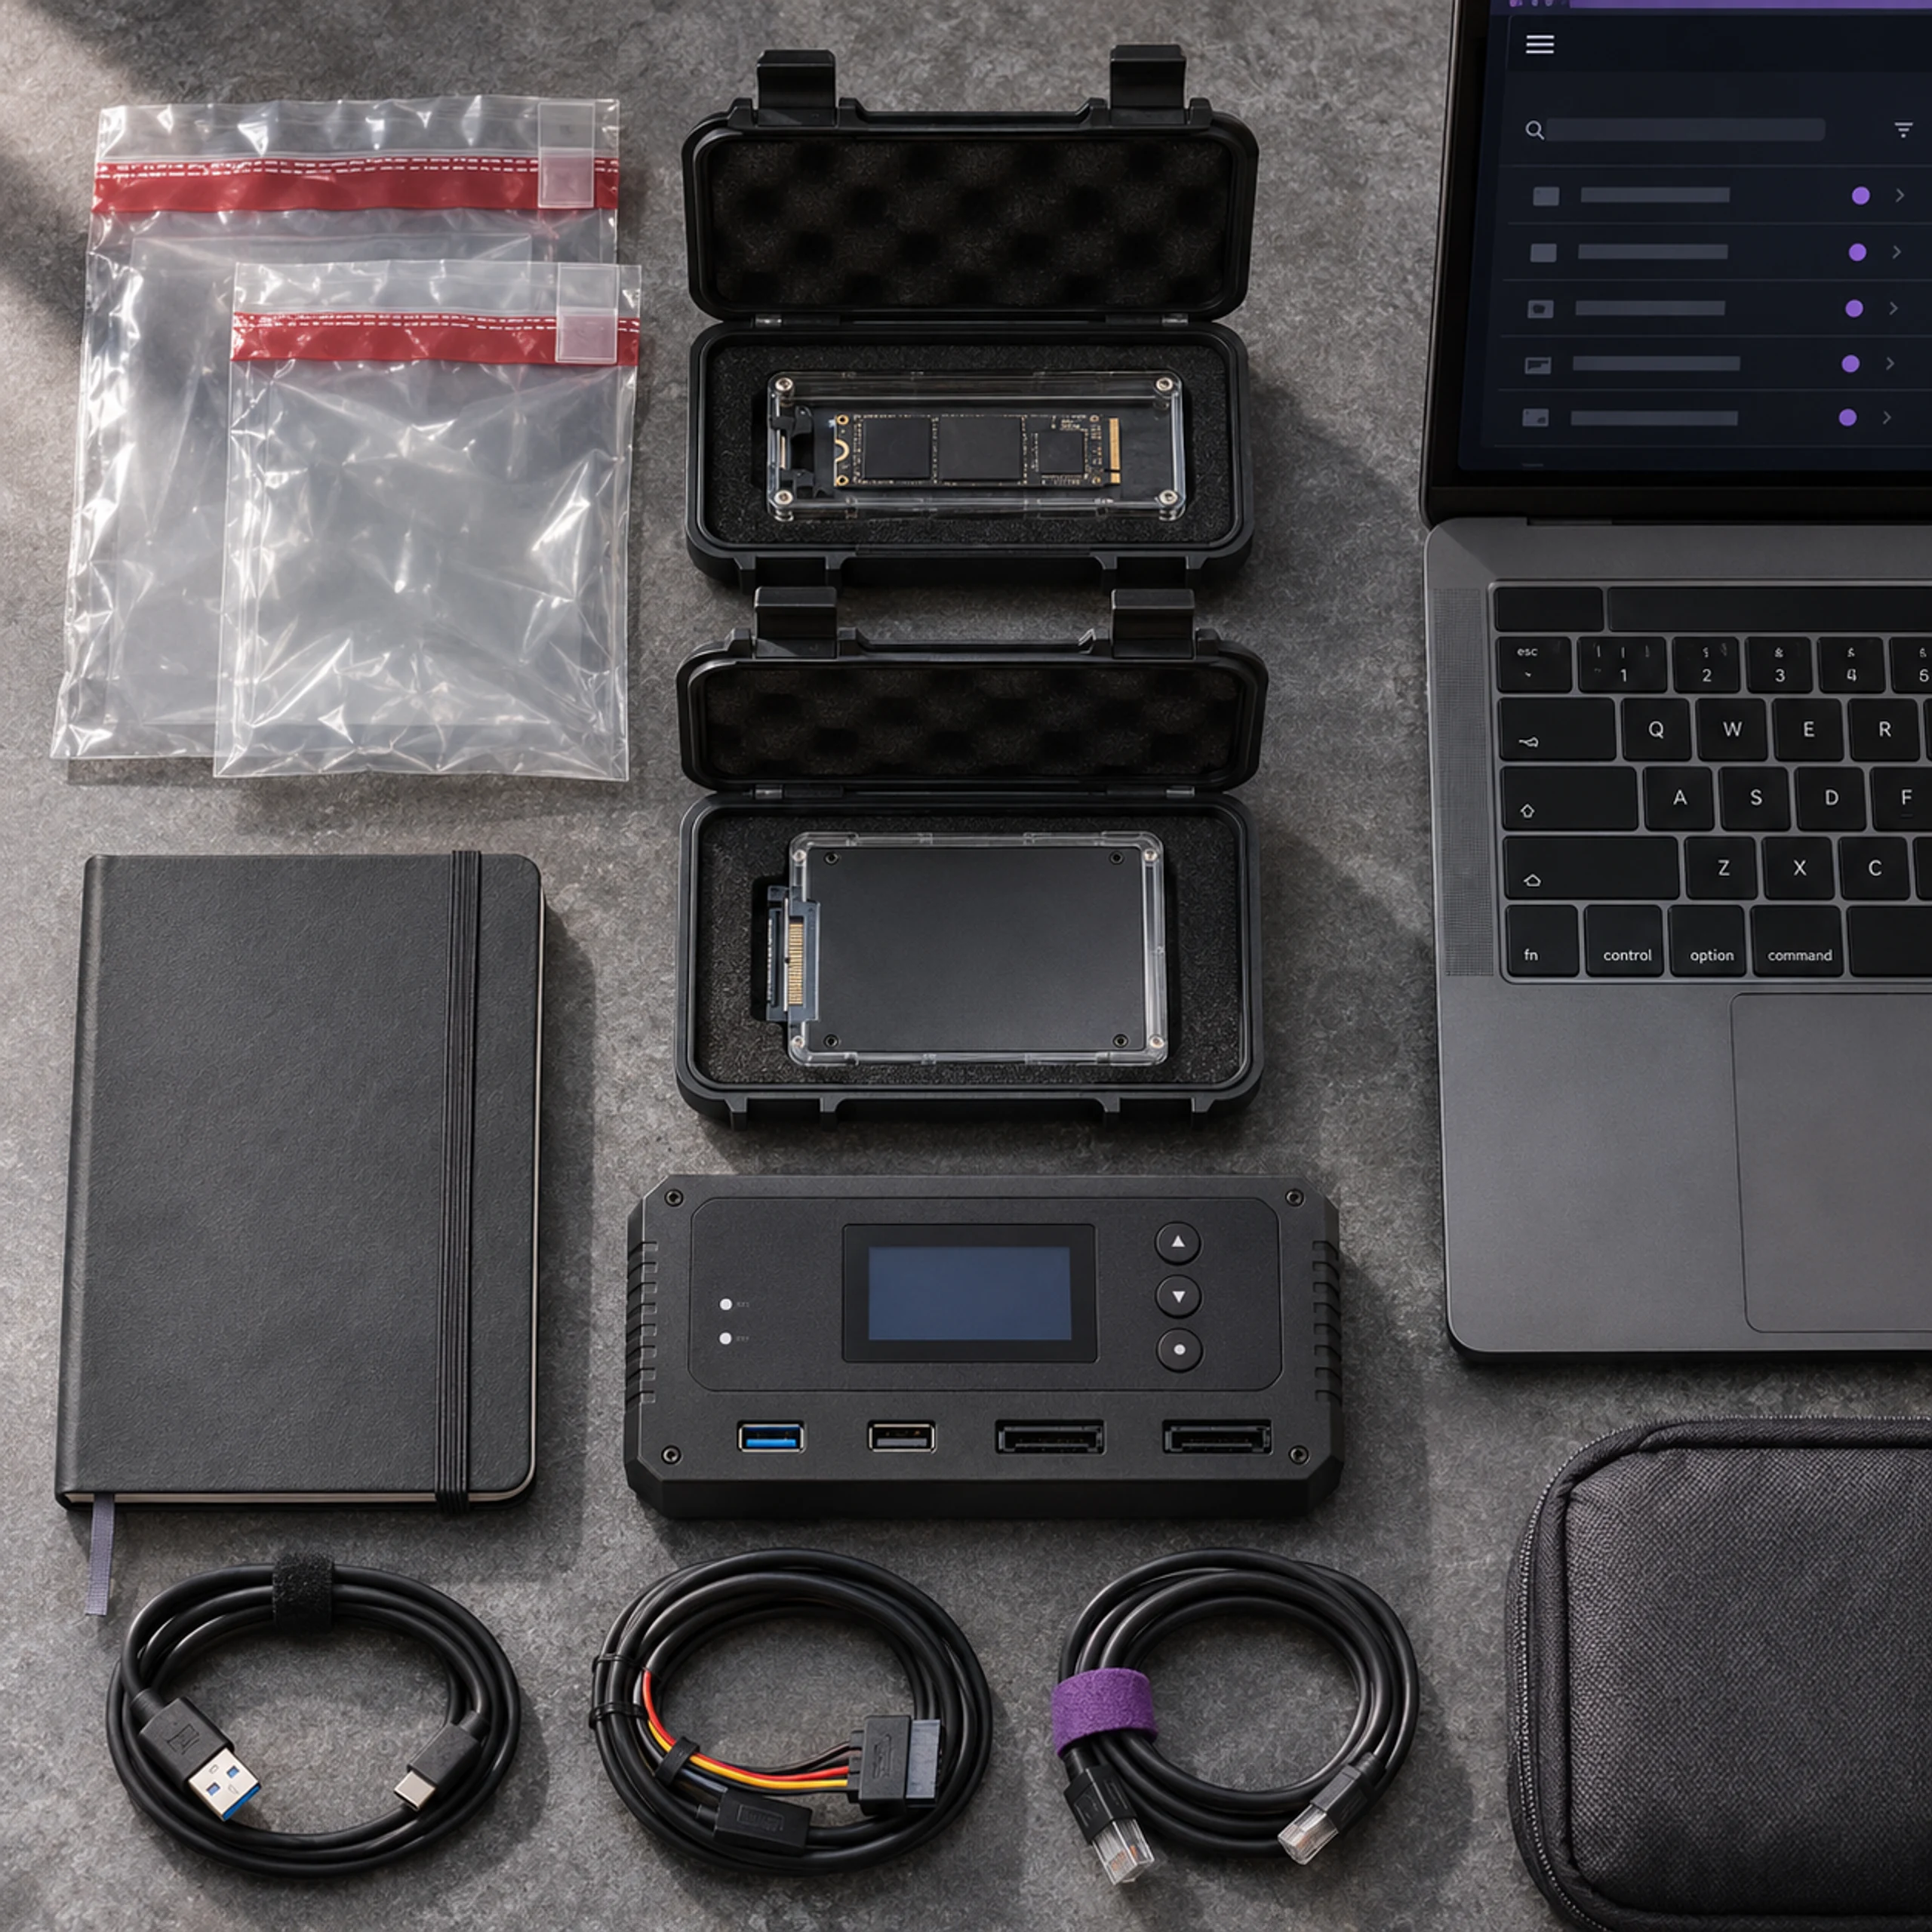
Breach readiness assessments, compromise assessments, and rapid incident response from DFIR experts. Be ready before the incident. Recover faster after.
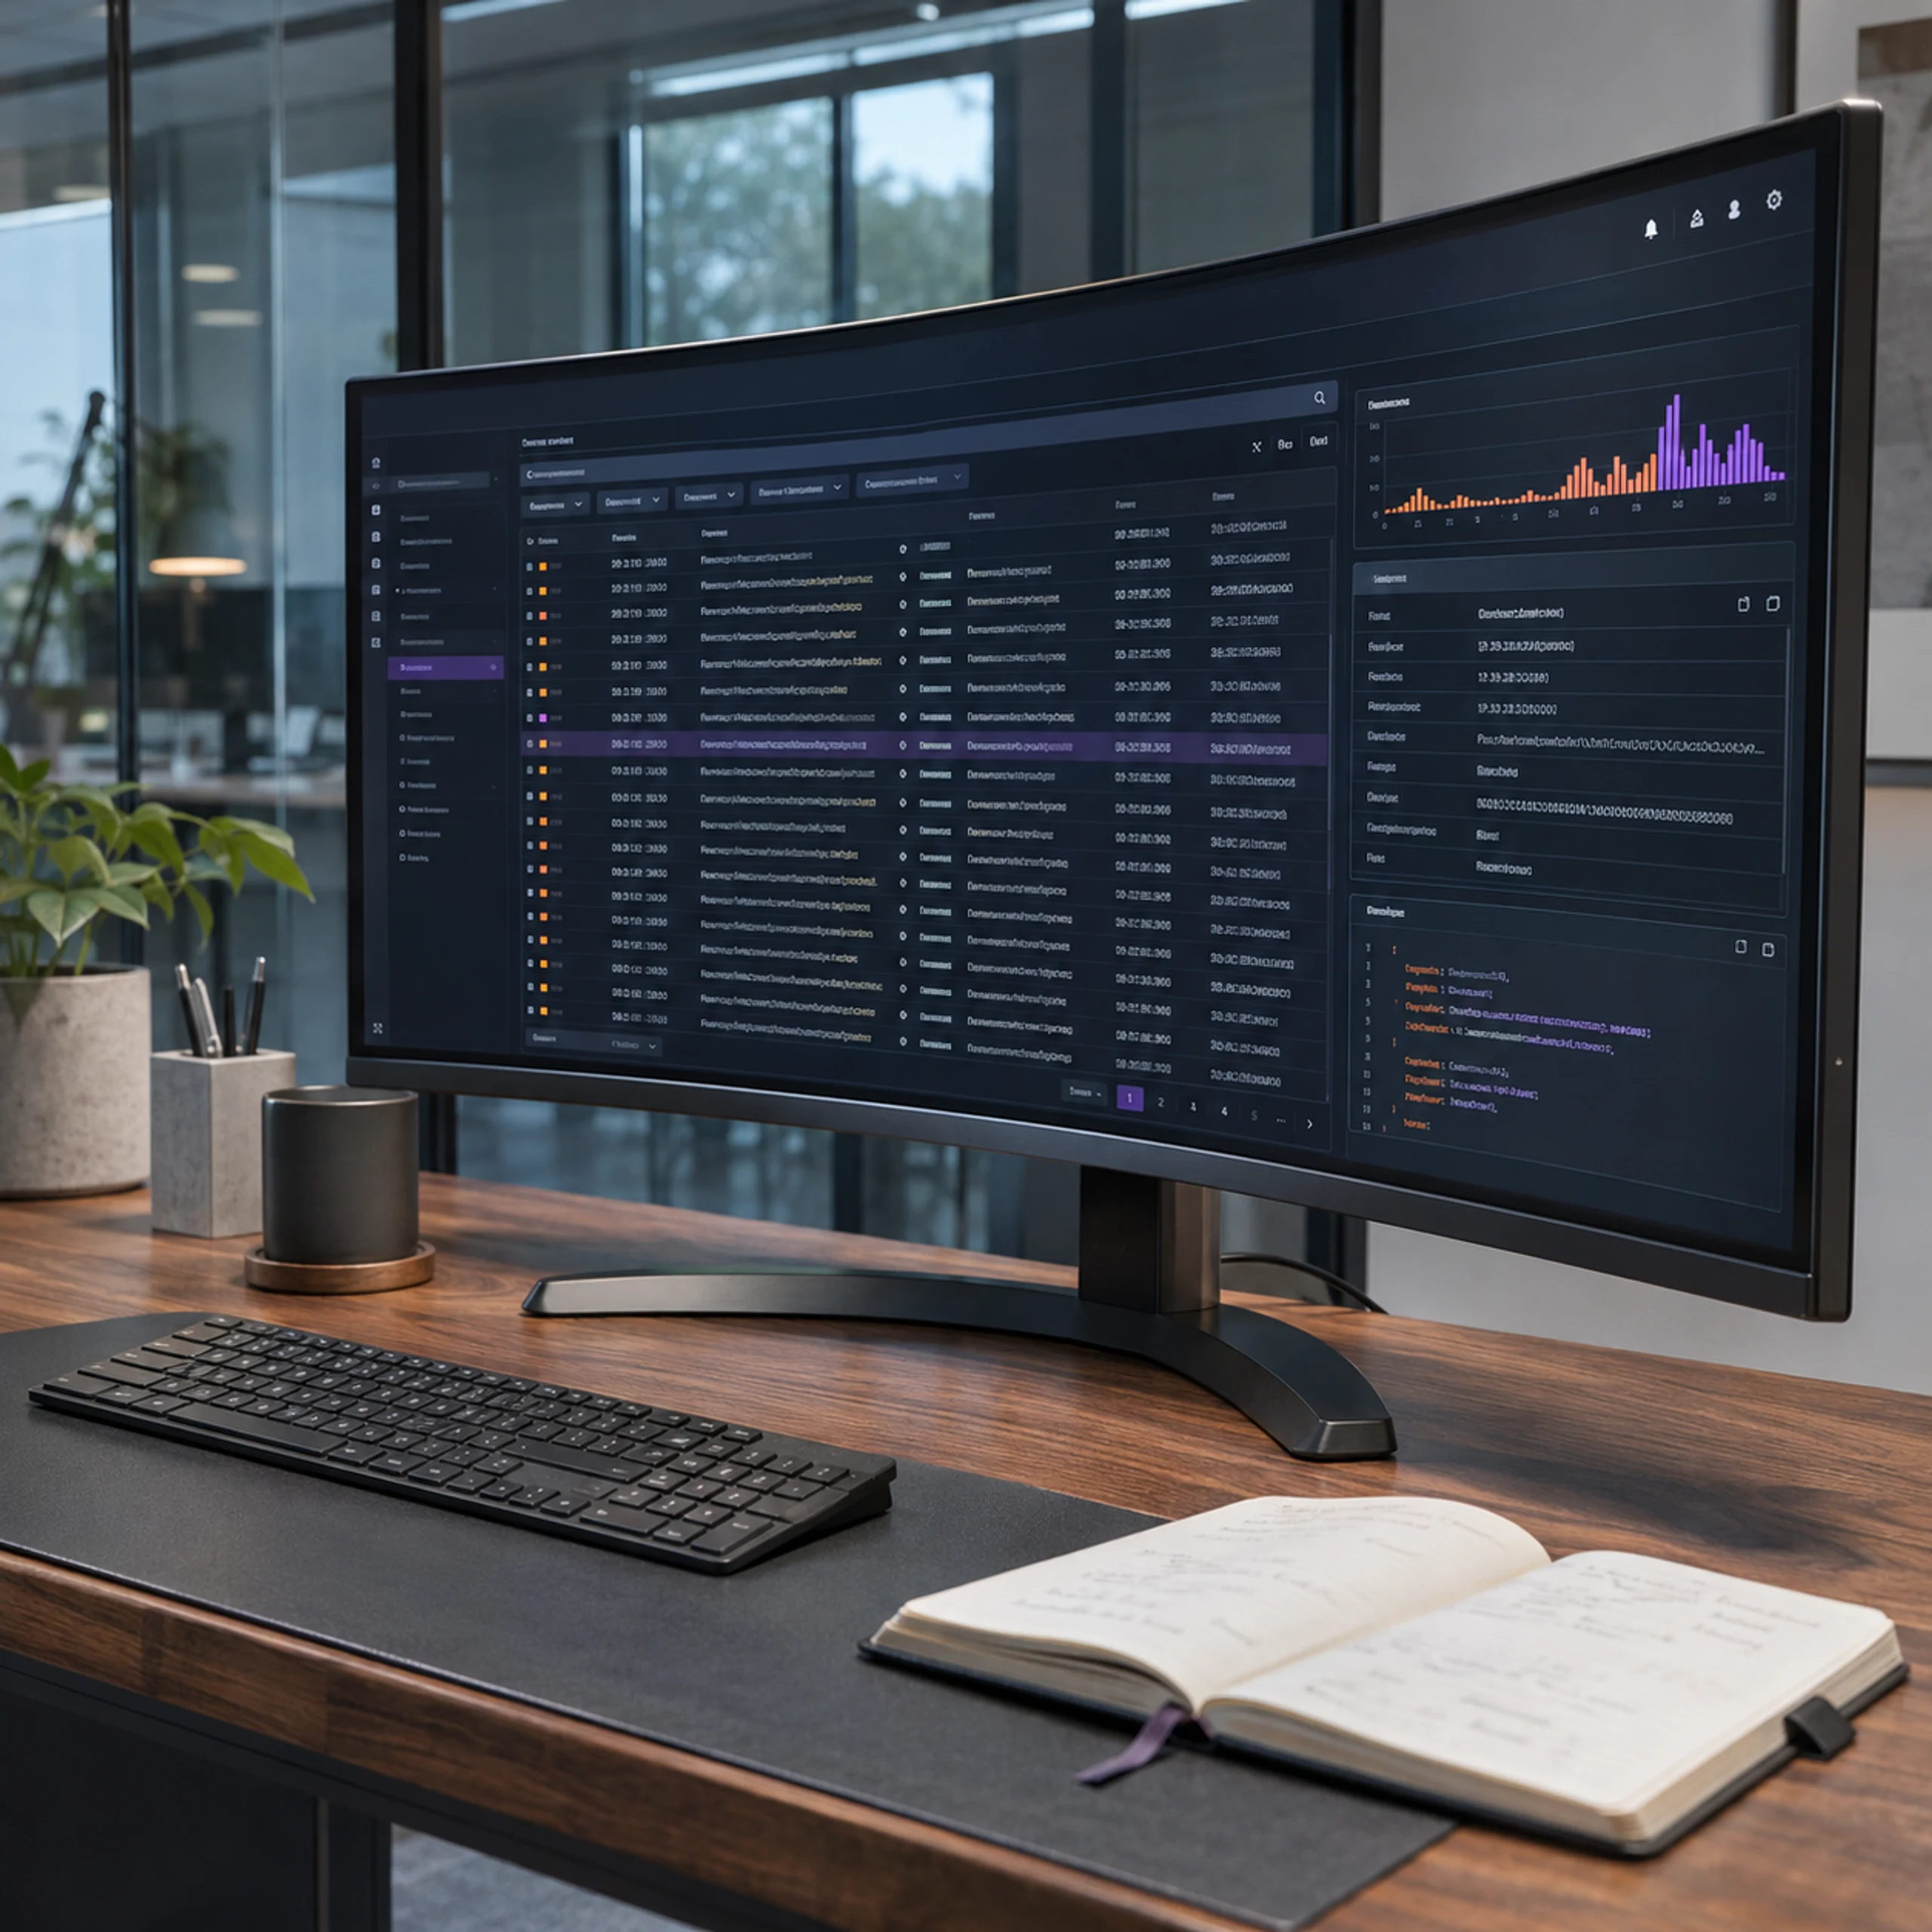
Proactive, intelligence-led hunting powered by elite analysts and Google Threat Intelligence. Behavioral and emerging threat hunts validated against your telemetry.
Choose your coverage
Service Priorities
Agree on monitoring coverage, relevant event sources, and escalation responsibilities before deployment.
Prepare Your Incident Escalation Plan
Incident Readiness
Set Focused Investigation Objectives
Threat Hunting
Resources
Next Steps