Vulnerability Management

See Every Vulnerability.
Own Every Risk.

Discover every asset across your network the moment it appears. Continuously scan every protected endpoint. Prioritize what attackers actually exploit — not what a spreadsheet says. One platform. Total visibility. Zero blind spots.

Cybersecurity dashboard UI titled Dashboards; tabs include Overview… Vulnerabilities (selected). Open vulnerabilities chart and Top 10 risky apps table

Today's Reality

01
Man in gray sweater with white earbuds using an open dark laptop indoors; faint “4.5” marker and dotted panel overlay

Scanning

One Agent. Zero Extra Infrastructure.

Vigilant Vulnerability Management runs on the same agent already protecting your endpoints. No new scanner to deploy, license, or maintain.

  • Continuous and on-demand scanning across Windows, macOS, and Linux

  • Full discovery of managed and unmanaged devices — close every inventory gap

  • Zero added infrastructure, zero added agents
02
Security dashboard “Dashboards” with tabs (Vulnerabilities selected), “Last year” filter, three donut summary cards and a table of CVEs and scores

Prioritization

Fight What's Exploitable, Not What's Loud

Stop drowning in raw CVE counts. DeepSafer ranks vulnerabilities by real exploitation risk, not theoretical severity.

  • Vulnerabilities and threats correlated natively, in real time

  • DeepSafer Risk Score ranks every finding by actual remediation urgency

  • Your team fixes what matters, first — every time

03
Dark security dashboard in a browser showing “Vulnerabilities” with a filter bar, CVE/severity chips, and a table listing assets and “Critical” alerts

Unified platform

One Console. Full Context. No Gaps.

Built natively into the Vigilant Platform, vulnerability findings sit side-by-side with live threat detections and full EDR context — not in a separate tab, not in a separate tool.

  • Vulnerability findings and threat detections correlated natively in the Vigilant Platform

  • One agent, one dataset, one console to investigate and act

  • One agent, one dataset, one place to investigate and act

04
Man with laptop on light green sofa in bright lobby; translucent overlay lines and faint “Oct. 2014” text near right center

Consolidation

Reduce Your Vendor Stack

Drop your standalone scanner. Vulnerability management is already built into the Vigilant Platform. Fewer vendors, fewer contracts, lower operating cost.

  • Eliminate infrastructure and maintenance overhead

  • One agent covers endpoint protection and vulnerability scanning

  • Cut the cost of separate scanner licensing

Decorative background gradient

Get Started

Symmetrical 3D geometric open box of glossy translucent panels around a glowing light-blue cube on a white background

Use Cases

One Agent. Multiple Outcomes.

Know What You Have. Protect What Matters.

Scheduled and on-demand vulnerability scanning across every protected endpoint, with Vigilant Network Control to identify coverage gaps of unmanaged devices.

Abstract purple/blue 3D blocks with translucent panels and white grid outlines; faint text B0B0 and T1021 visible

Managed Endpoints

Assess application and OS vulnerabilities across your entire managed fleet with automated scans.

Explore the Platform
Purple smartphone protected by a translucent security shield

Distributed Environments

Cover remote, hybrid, and branch office endpoints with agent-based visibility that doesn't require network access or proximity to a scanner.

Explore the Platform
Futuristic blue-purple office scene: man at desk facing back-view monitor with Apple logo, overlay text T1486 T1602 443

Unmanaged Devices

Discover endpoints operating outside your managed inventory, including IoT devices, personal devices, and unknown assets.

Explore the Platform

Vulnerability management in practice

Understand exposure. Prioritize and follow through.

Vigilant Vulnerability Management helps teams review software and exposure context, and coordinate remediation around organizational needs.

  1. 01

    Discover

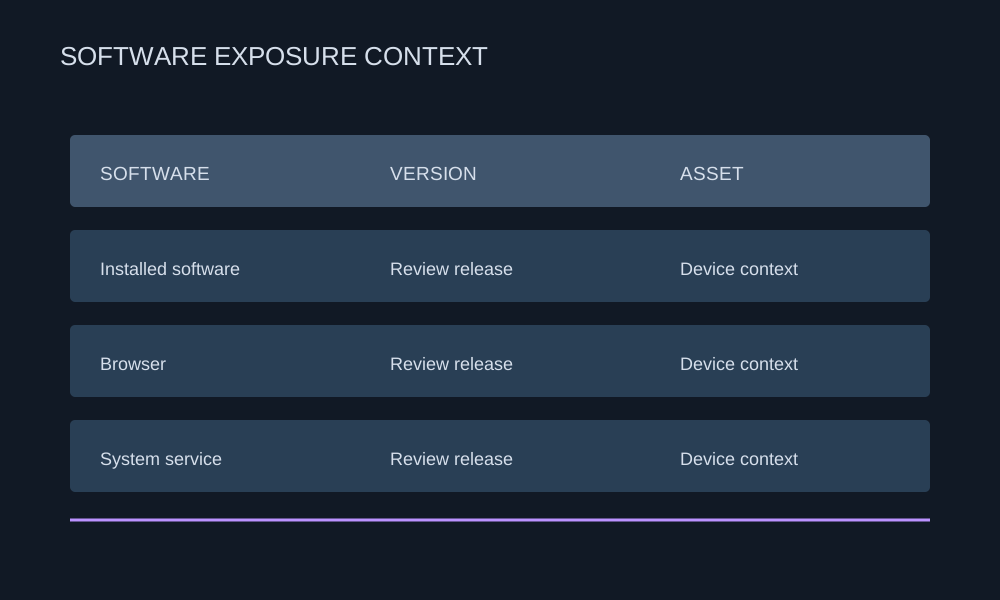
    Review software and version context to identify findings that need validation on your assets.

    Illustrative software inventory with versions and asset context
  2. 02

    Prioritize

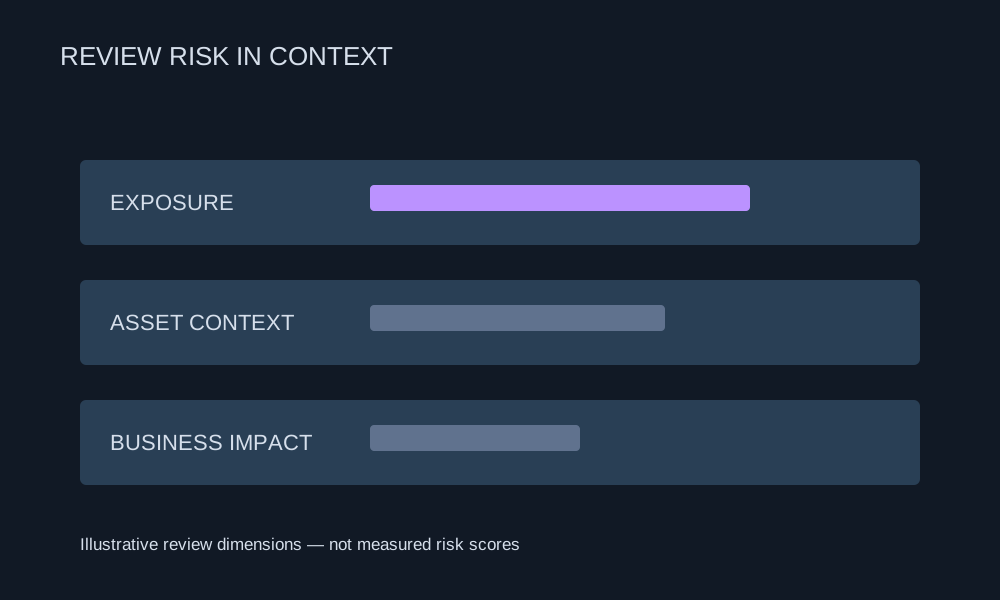
    Consider exposure, asset importance, and business needs when deciding what requires attention first.

    Illustrative exposure, asset context, and business impact review dimensions
  3. 03

    Verify

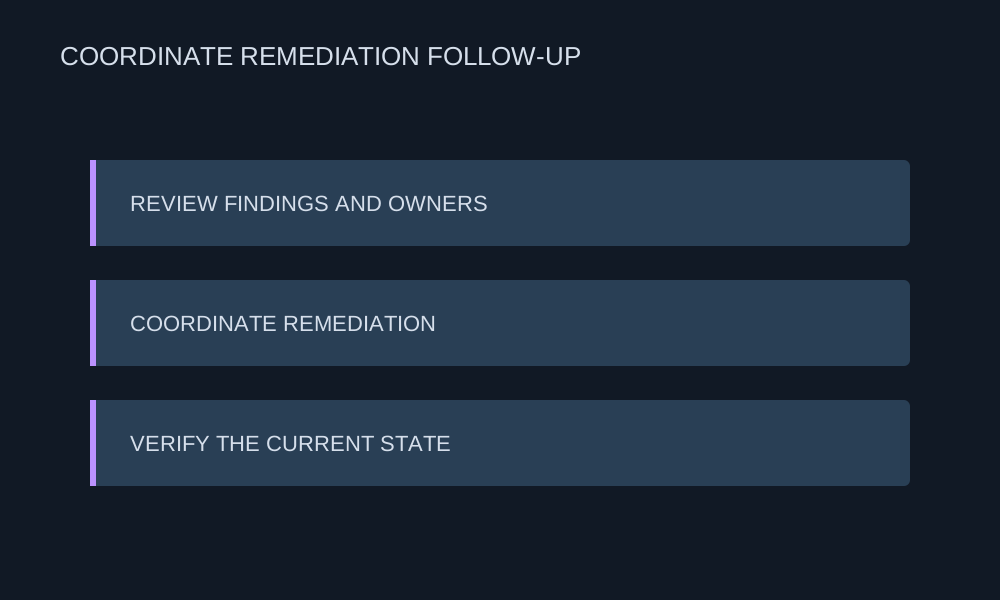
    Coordinate remediation with the responsible teams and review the current state after changes.

    Finding review, remediation coordination, and verification workflow

Customer & industry focus

Security for the organizations that connect Yemen.

From telecom infrastructure to mobile services, explore local security priorities and the DeepSafer capabilities that address them.
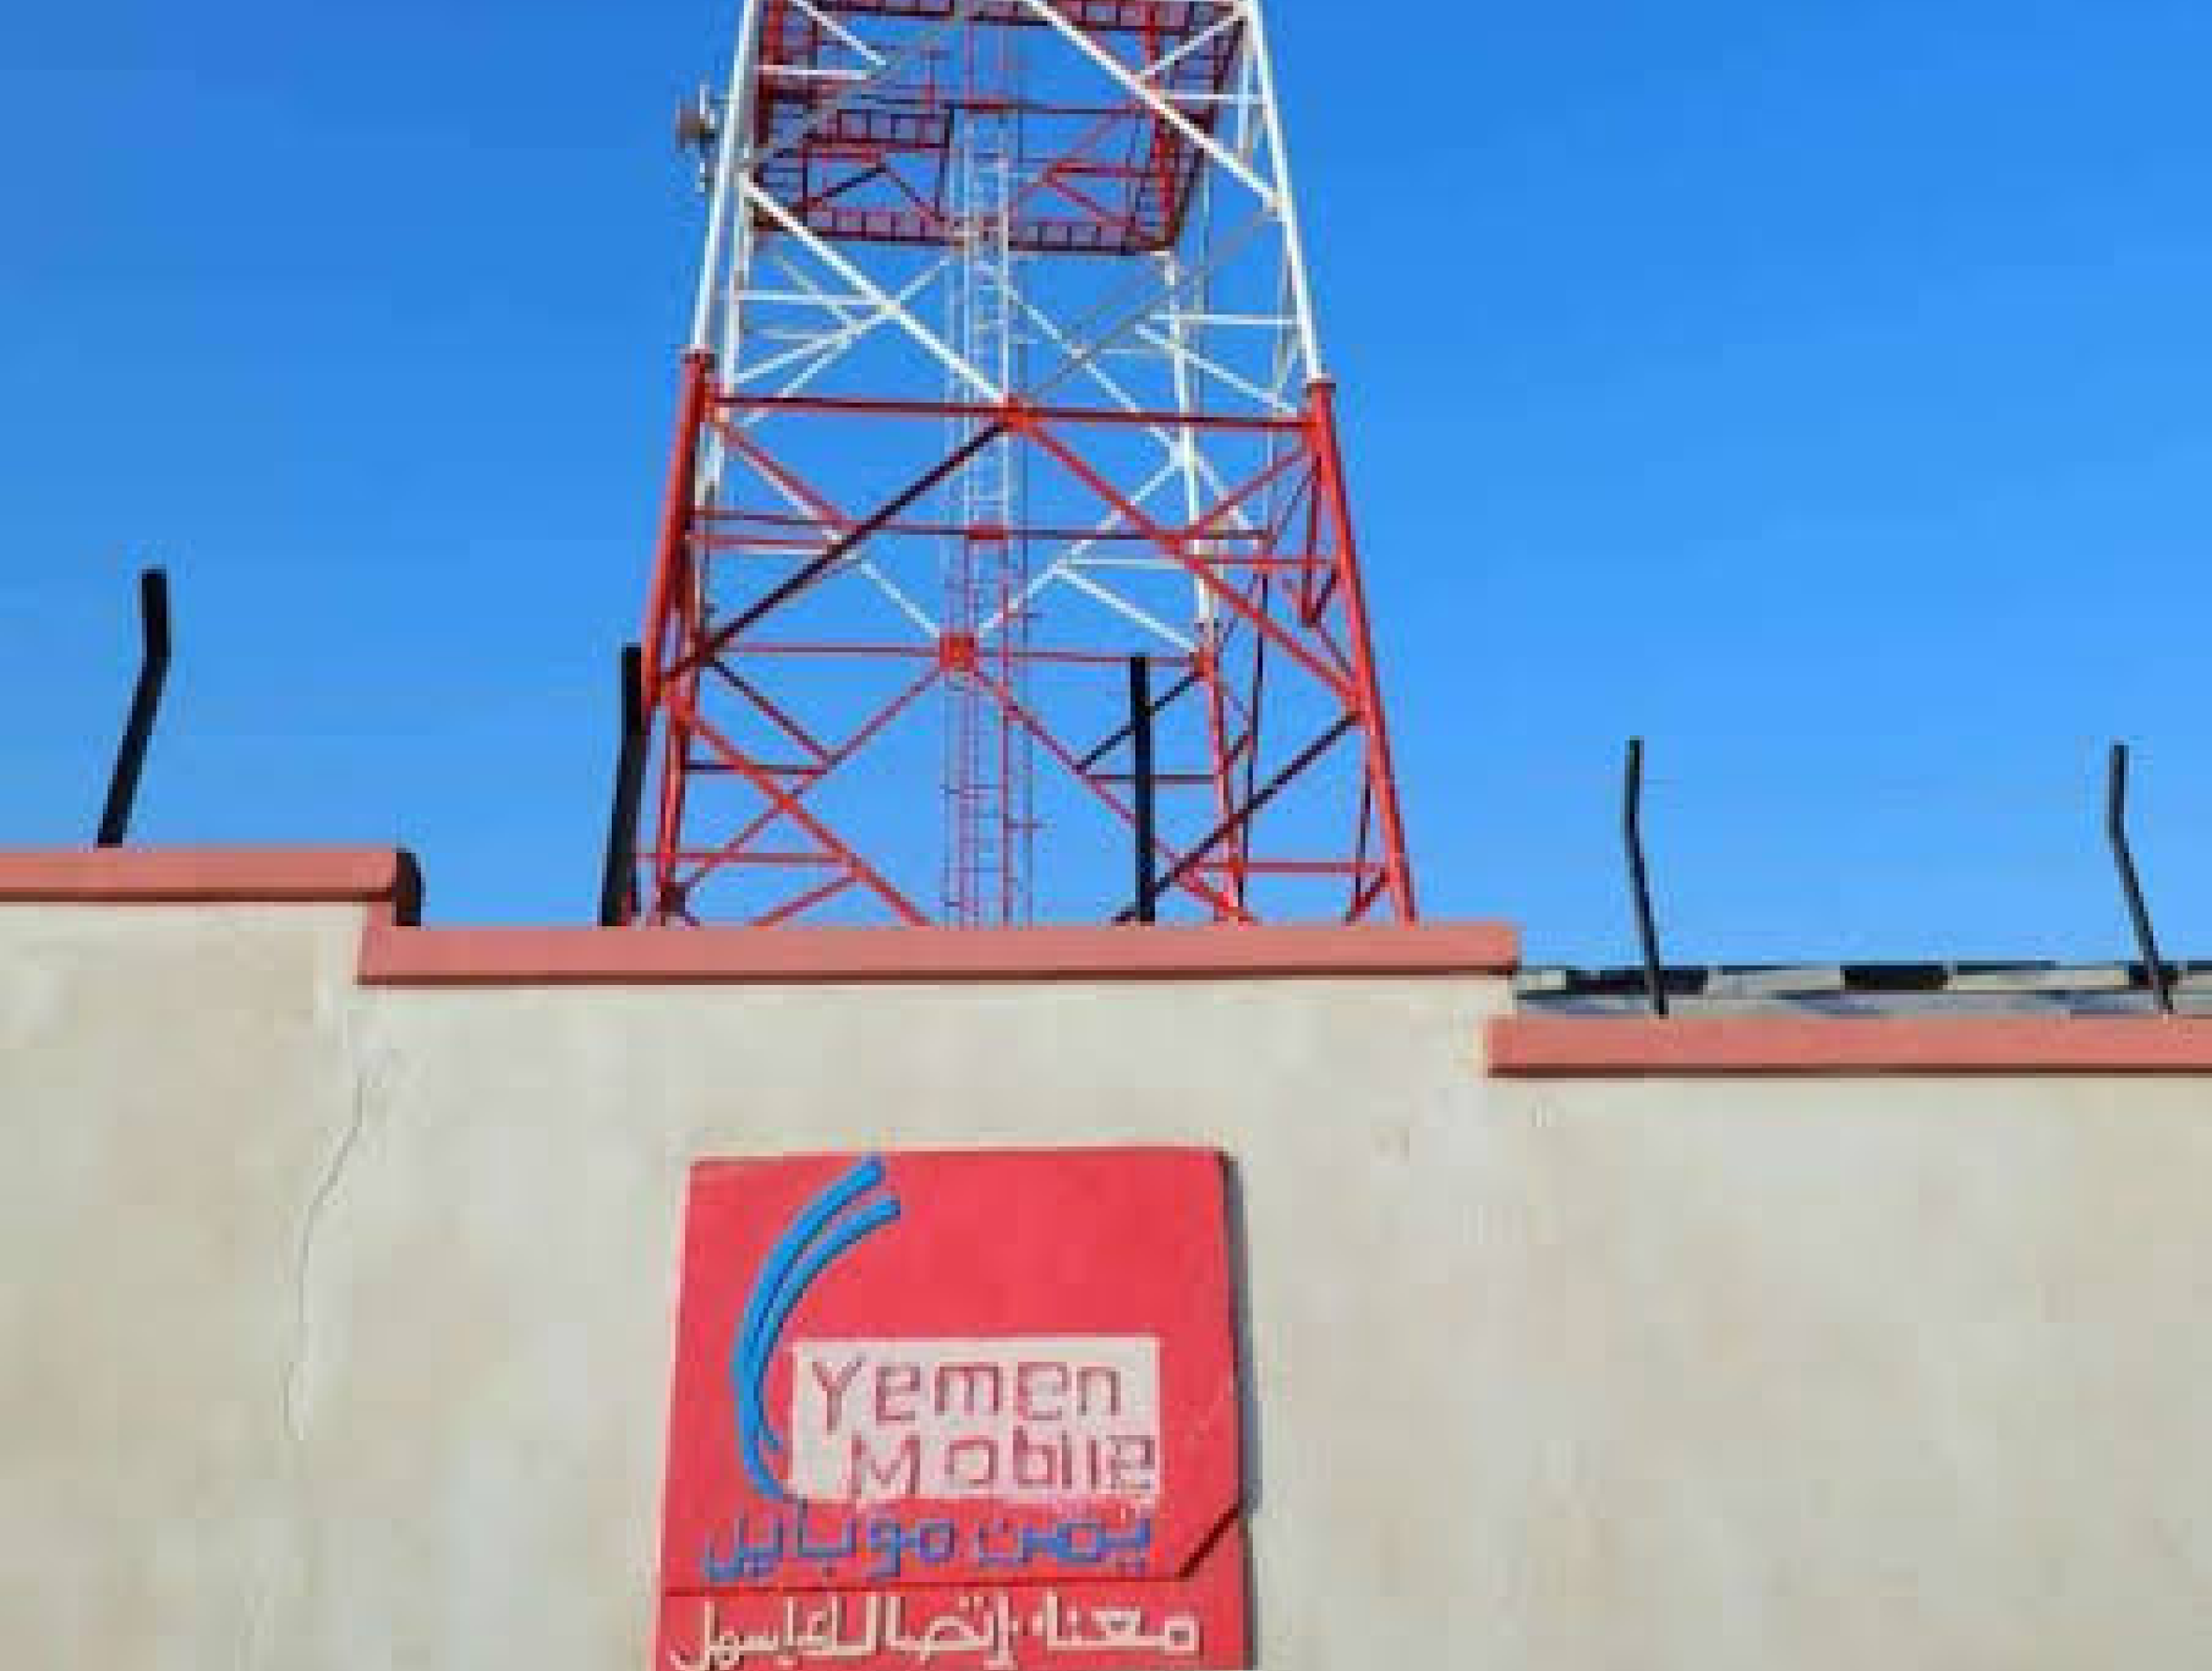
Yemen Mobile telecommunications tower and site

Clearer context for endpoint exposure.

Yemen Mobile

Mobile services & endpoint protection

Review software and versions associated with endpoints to identify what needs validation or remediation.


Explore the solution
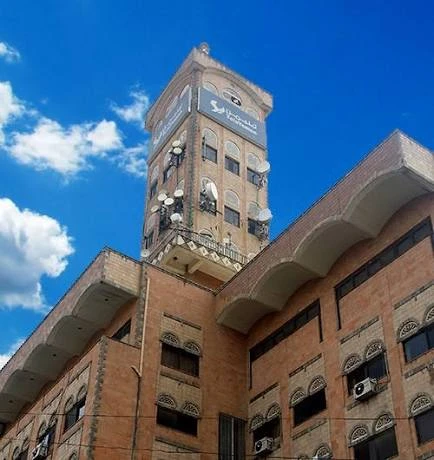
TeleYemen building and telecommunications tower

Remediation priorities with operational context.

TeleYemen

Telecommunications & infrastructure

Connect findings to assets and business needs to guide remediation discussions with IT teams.


Explore the solution
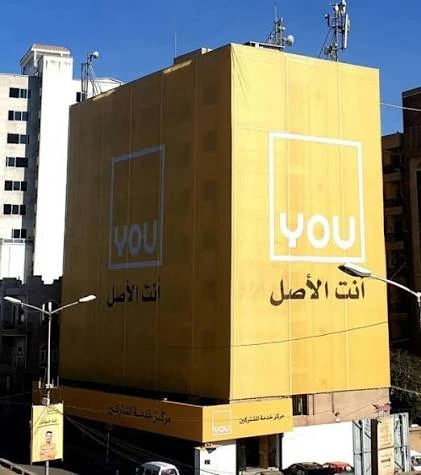
YOU company building with its yellow facade and logo

Shared follow-up after change.

YOU

Yemen Omani United telecommunications

Review remaining findings after remediation and coordinate responsibilities across security and operations.


Explore the solution

Why DeepSafer

Context that supports remediation and follow-up.

Review software, versions, and asset context to prioritize remediation with the teams responsible for change.
Exposure Across Your Workforce

Exposure Across Your Workforce

Review software and asset context across office and remote working environments.

Findings That Need Validation

Findings That Need Validation

Review affected software, observed versions, and supporting context before planning action.

Risk Beyond a Severity Label

Risk Beyond a Severity Label

Consider exposure and asset importance alongside the needs of your business.

Coordinate With the People Who Own the Change

Coordinate With the People Who Own the Change

Discuss remediation options, operational impact, and responsibilities with the teams managing the assets.

Review What Changed

Review What Changed

Follow up after remediation and review remaining findings as the environment evolves.