Optimized Incident Readiness
Every second counts. Our simulations fine-tune your team’s response, ensuring faster detection, quicker containment, and minimized impact during real incidents.
PenTest & Red Team
Stay ahead of threats with DeepSafer’s advanced Penetration Testing and Red Teaming. We simulate real-world attacks to uncover hidden vulnerabilities, test your defenses under pressure, and deliver sharp, actionable insights to strengthen your security.
The Threat Hunting Advantage
Every second counts. Our simulations fine-tune your team’s response, ensuring faster detection, quicker containment, and minimized impact during real incidents.
Navigate regulations with ease. Our assessments ensure your practices align with key industry standards, simplifying compliance and demonstrating your commitment to data protection.
Get a holistic, attacker-centric view. We uncover hidden vulnerabilities across all your assets—endpoints, networks, applications, and cloud—providing MITRE ATT&CK-mapped insights and clear remediation guidance.
Go beyond compliance. We don’t just find flaws; we provide actionable insights to build an unshakeable security framework, significantly reducing your risk. patterns across telemetry, automating repetitive workflows, and compressing the time from detection to confirmed finding.
Why Choose DeepSafer Services?
Our team understands the local threat and regulatory landscape in ways no distant foreign vendor can match.
We test your systems using genuine attacker techniques, not shallow automated scans or generic reports.
From networks and applications to endpoints and cloud, we leave no entry point unchecked.
Findings ranked by severity, with practical remediation steps both technical and executive teams understand.
We uphold the highest data protection and sovereignty standards throughout testing, with zero leaks.
We don't stop at the report — we help close gaps and verify every fix works.
The DeepSafer Portfolio
24/7 expert protection, investigation, and response across your entire environment.
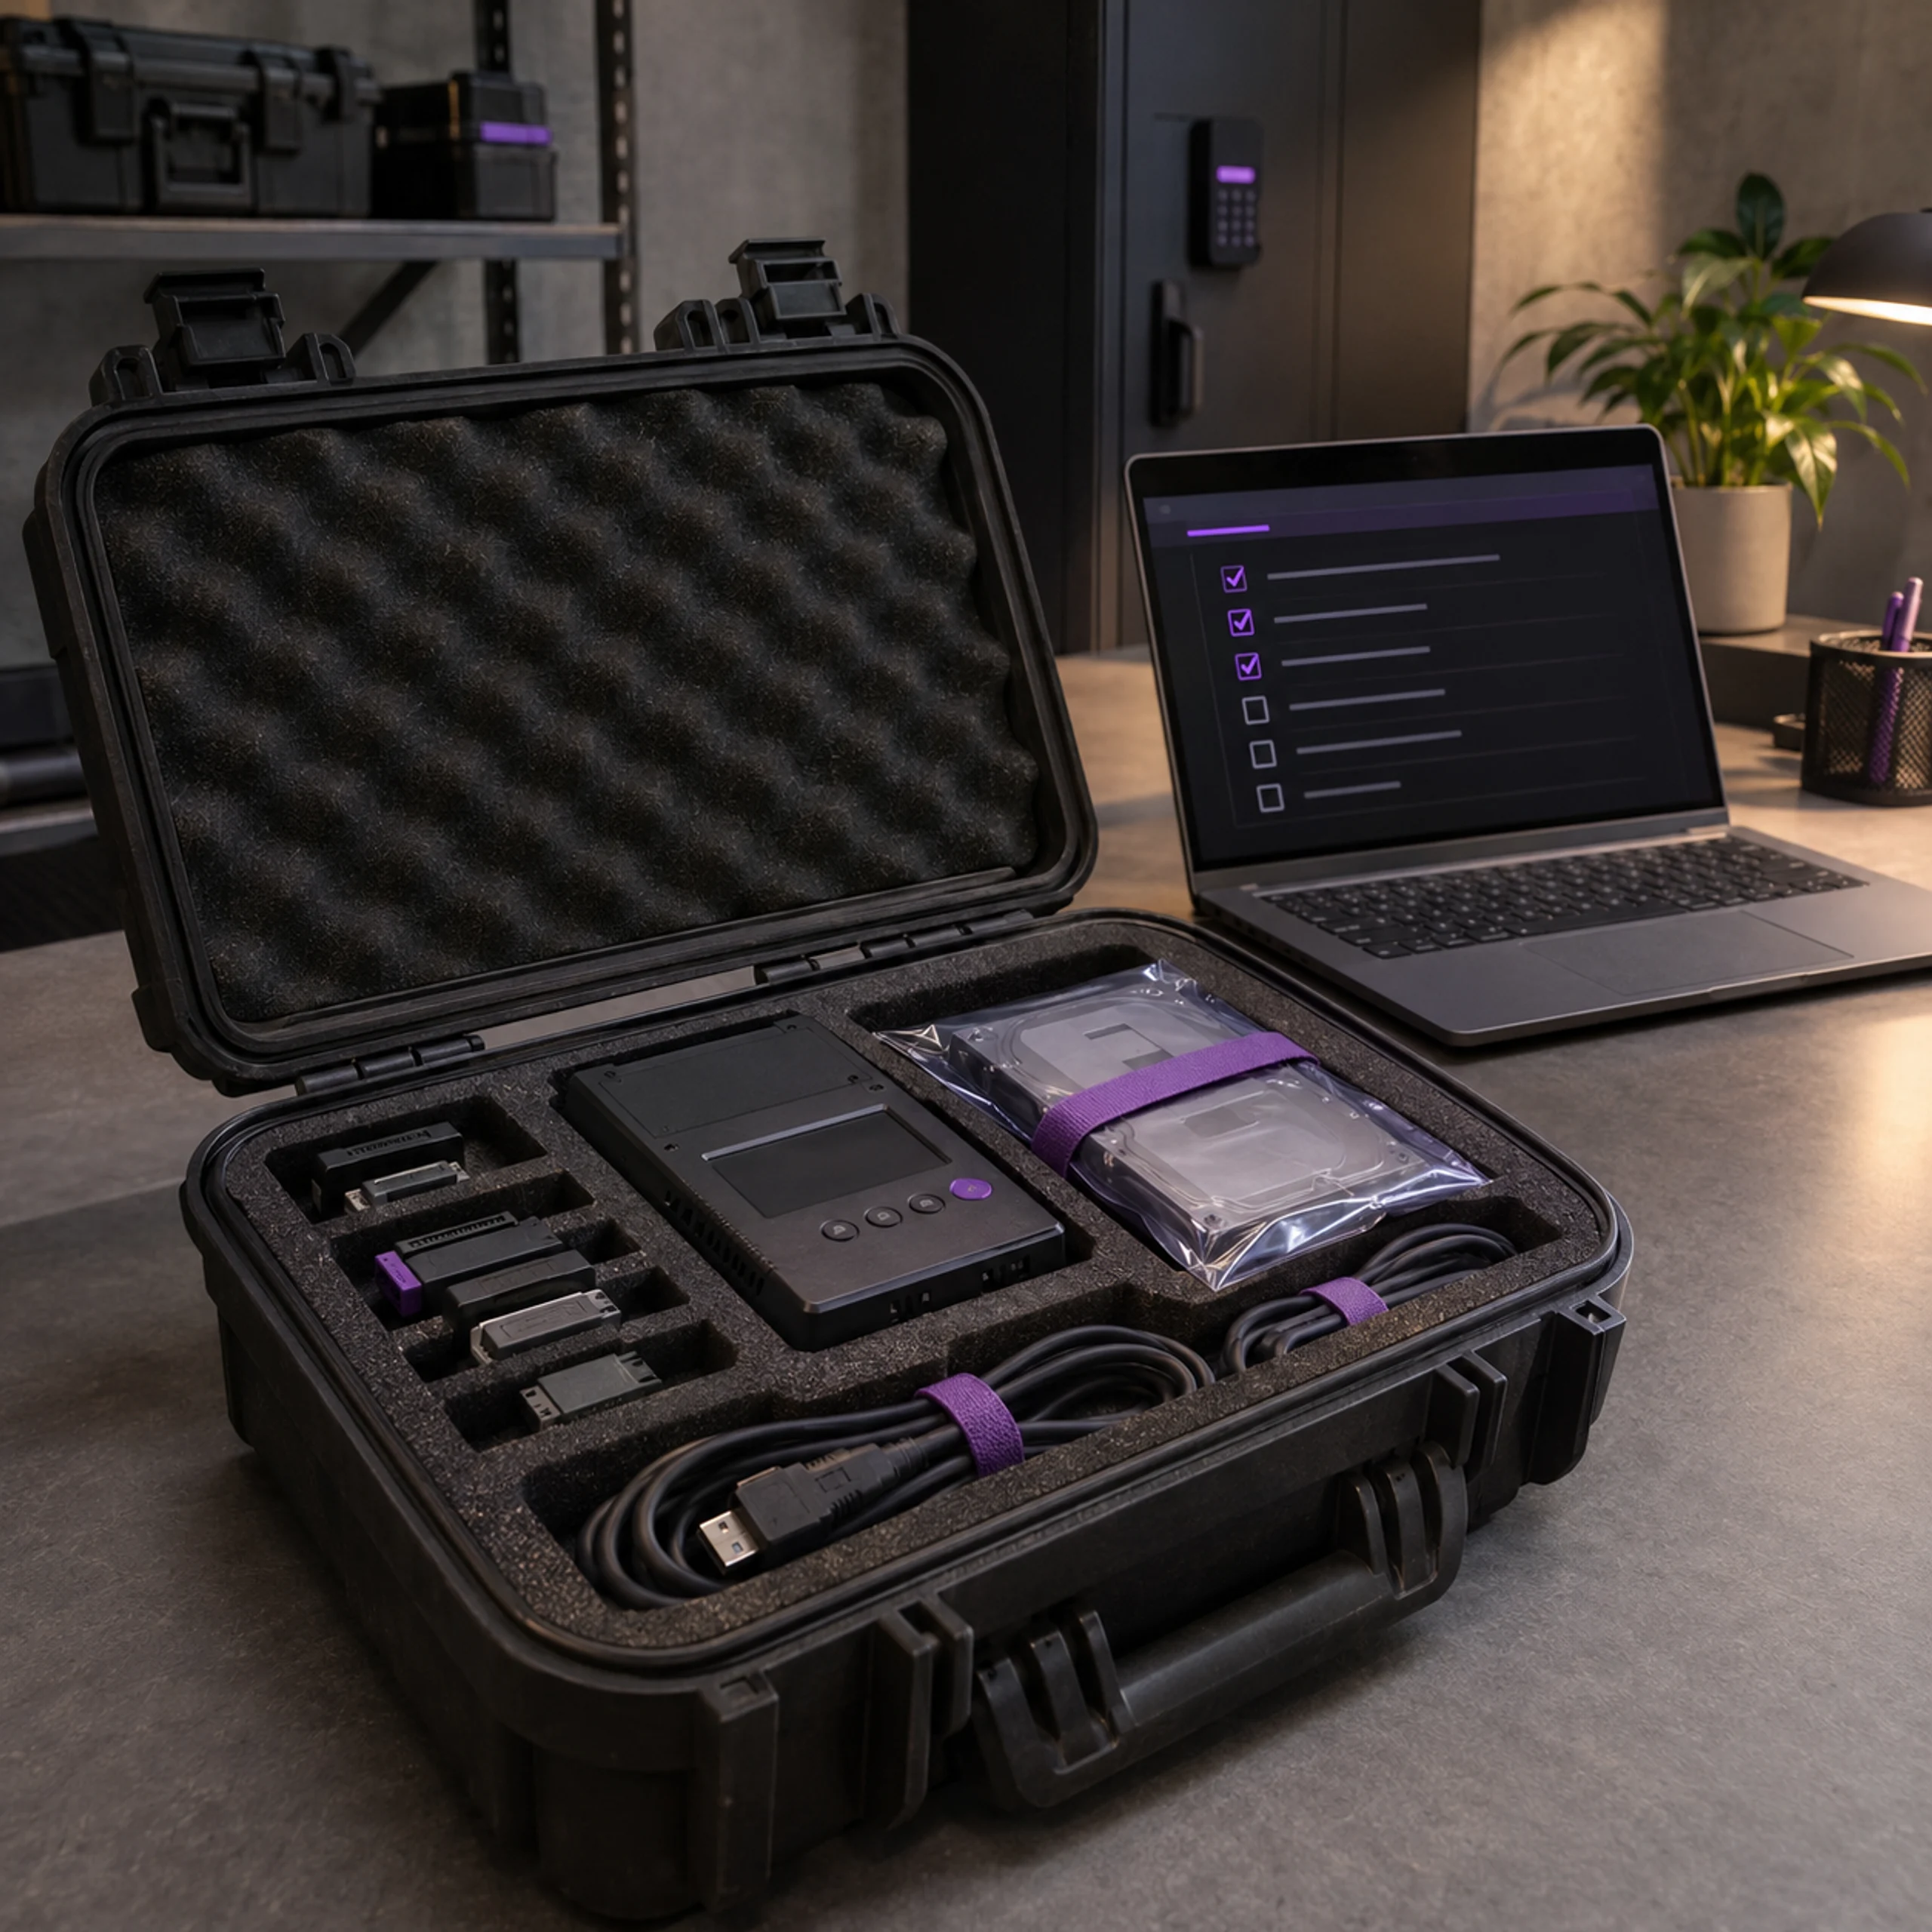
On-demand breach readiness, expert-led compromise assessments, and rapid incident response.
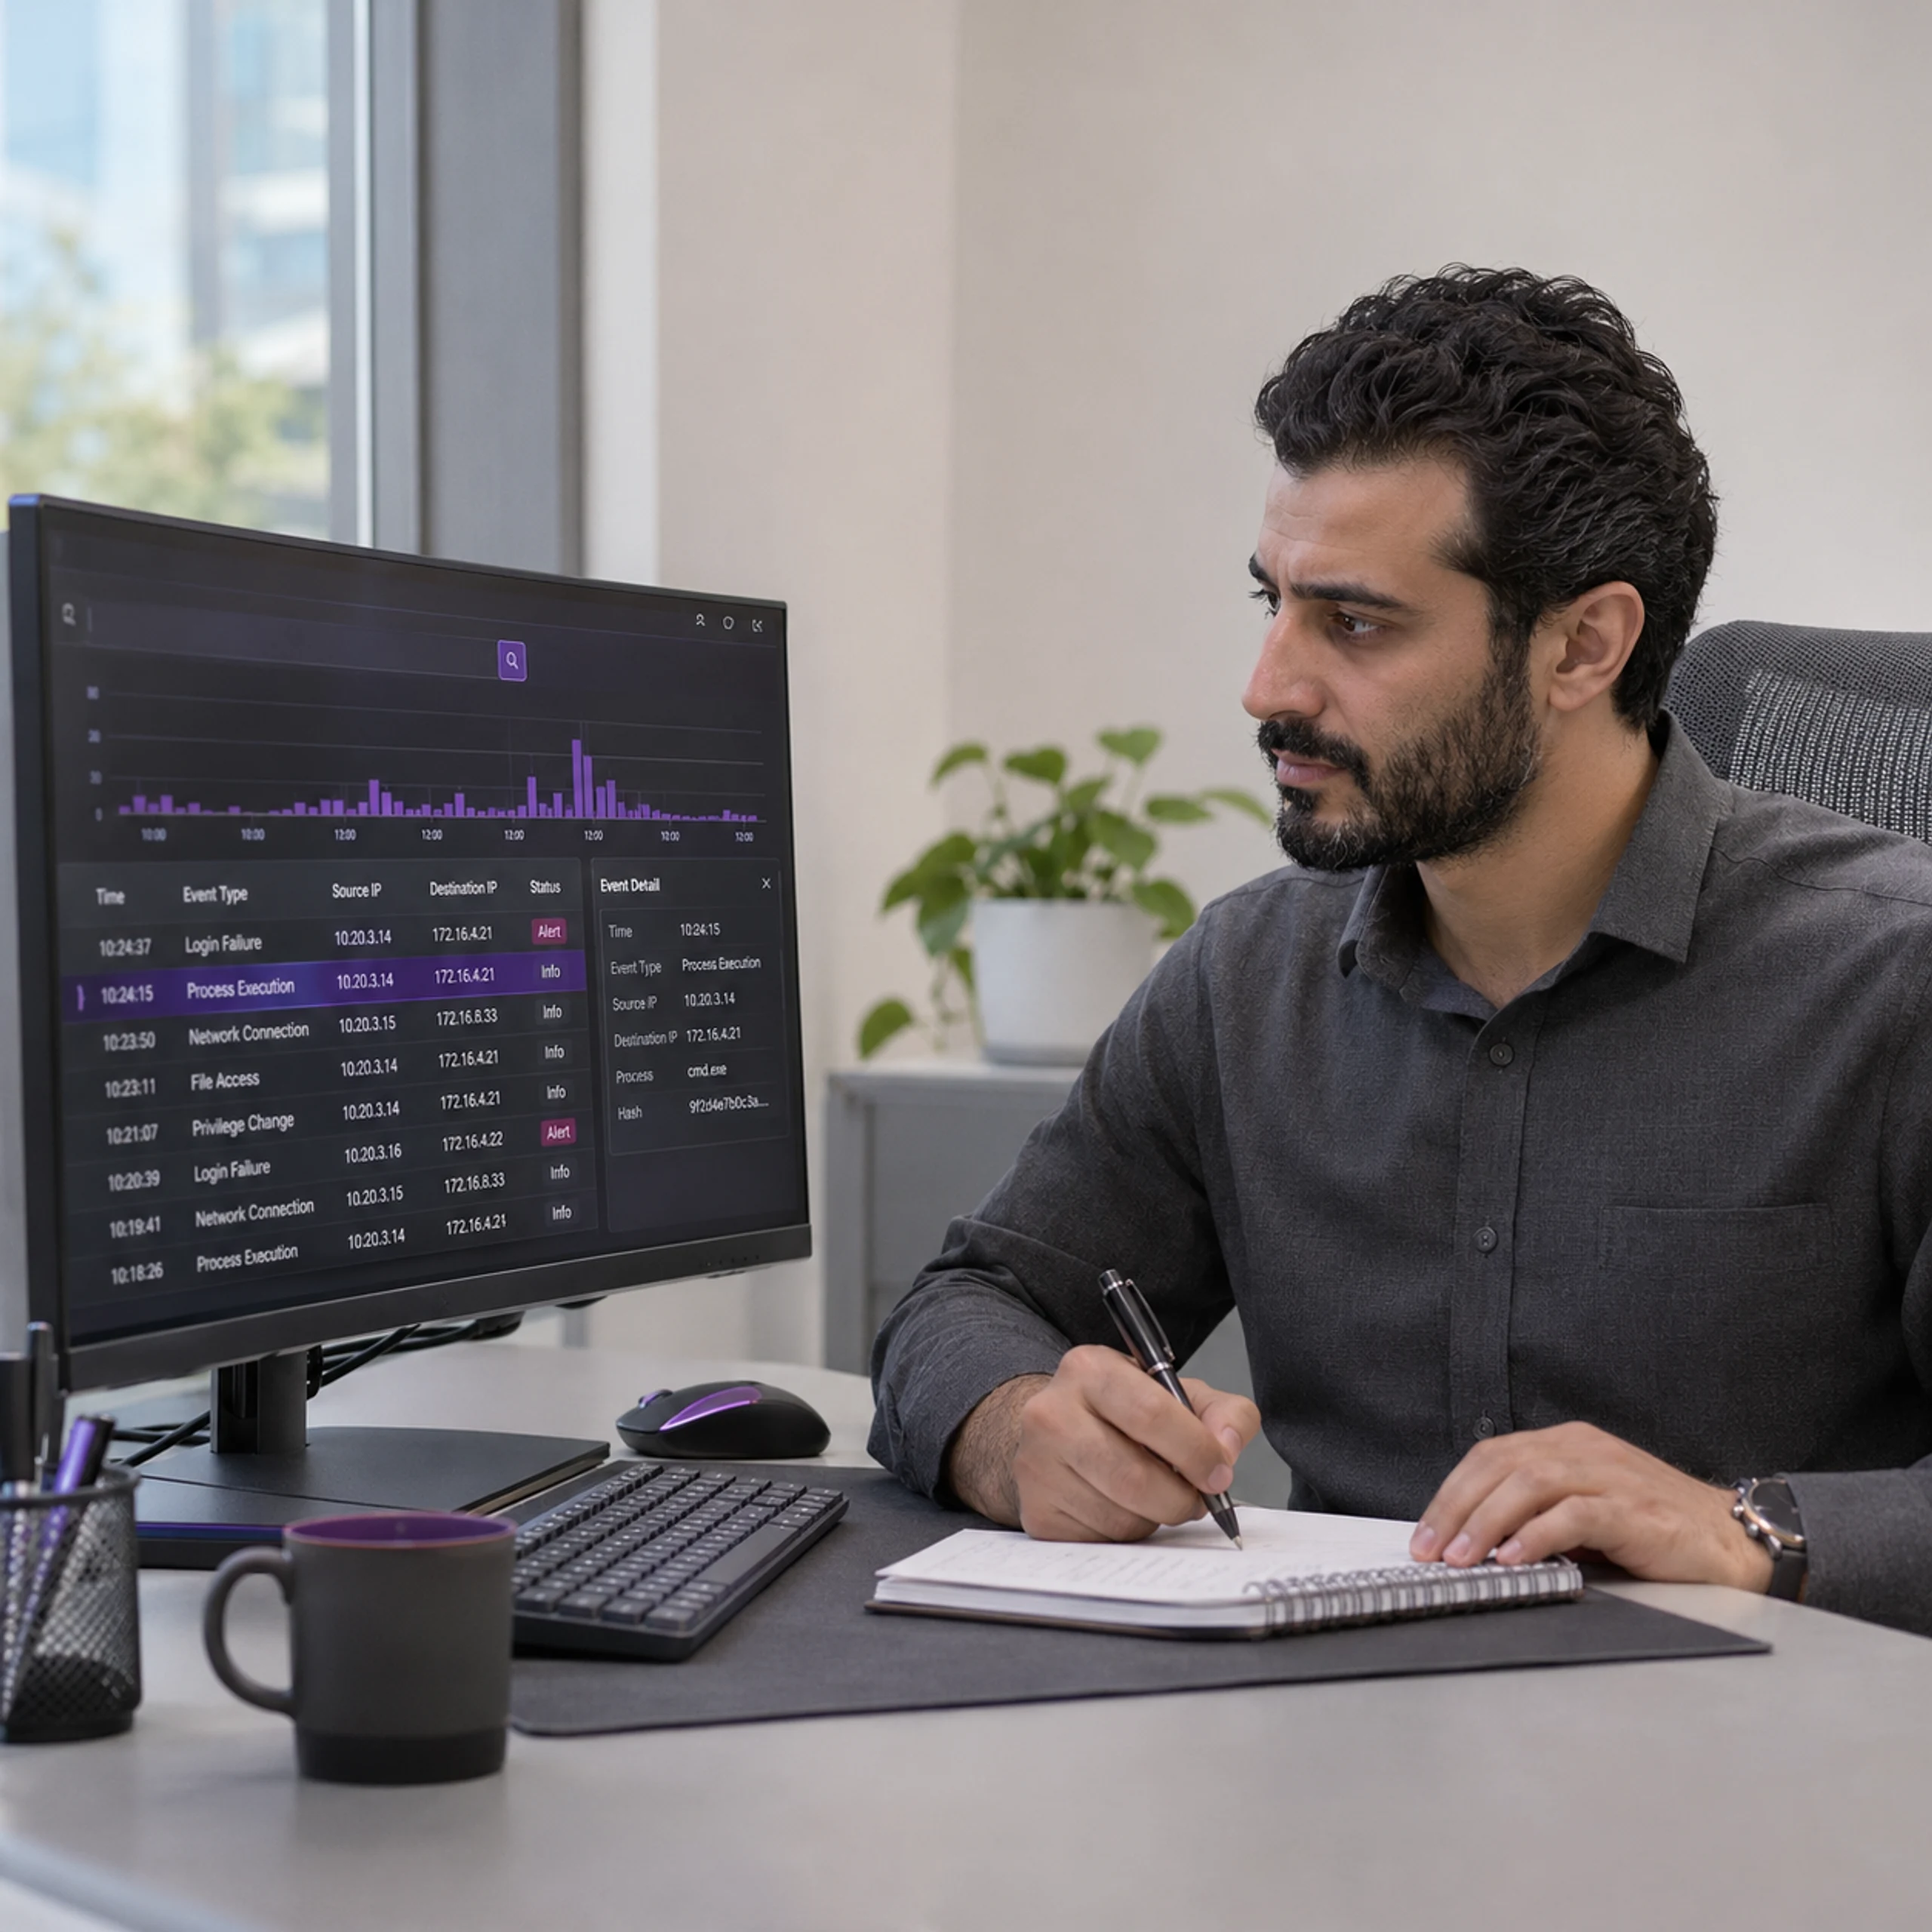
Focused investigations use available telemetry and threat context to review suspicious activity and guide follow-up.
Industry Focus
Investigate endpoint and network activity to review suspicious connections and prioritize follow-up in a telecom environment.
Connect Network and Endpoint Evidence
YOU — Yemen Omani United
Review Activity Across Business Systems
Yemenia
Resources
Next Steps