Extended detection and response

See the Full Attack.
Respond as One.

Sophisticated attacks move across endpoints, identity, and cloud. DeepSafer unifies data from any source to give teams full attack context, AI-driven workflows, and the advantage of acting as one.

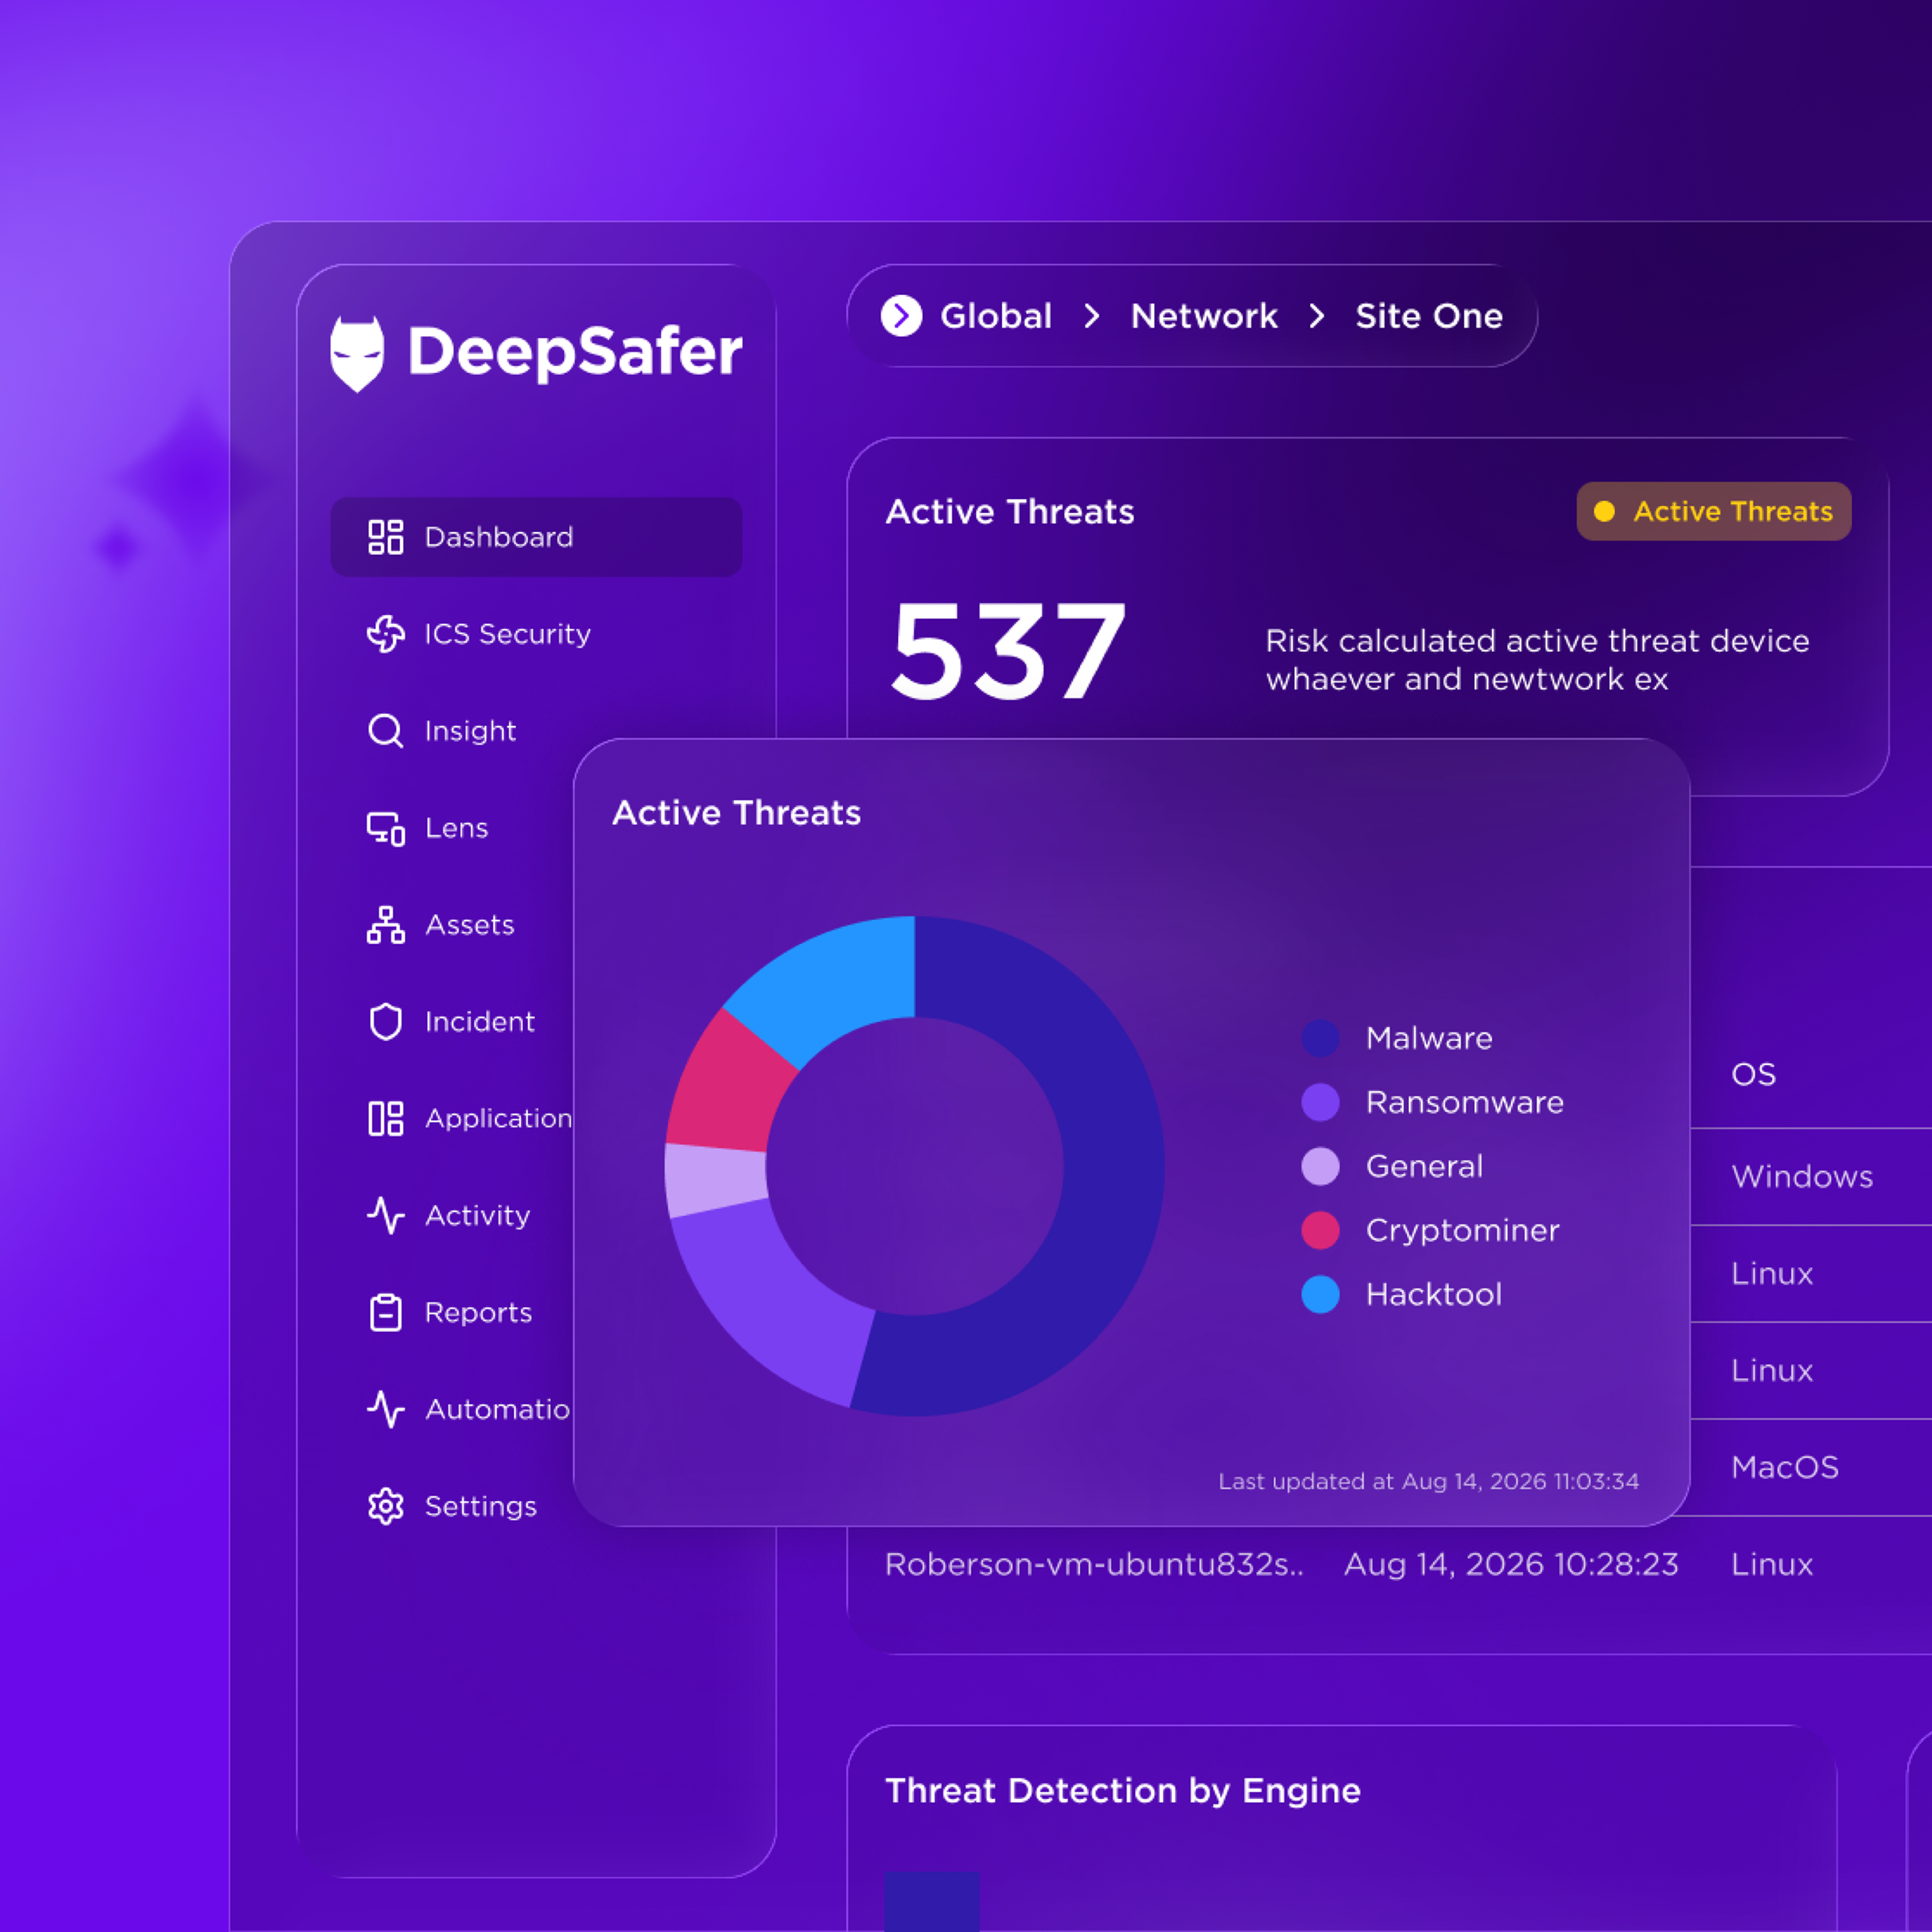
Dark security dashboard UI in a browser window on purple background, showing Dashboards tabs and a chart “Log Volume by Source” with table “Top high-value assets with alerts”

Today's Reality

01
Dark security dashboard showing “LockBit_Ransomware.hta detected as Ransomware”, tabs and a network graph of green device node linked to colored alert nodes

Cross-surface Correlation

See the Full Attack. Not Just the Alert.

Ingest and normalize data across endpoint, identity, cloud, AI systems, and third-party tools into a single correlated view.

  • Correlate signals across all four pillars automatically

  • Eliminate blind spots that fragmented tools create

  • Extend visibility through one-click Marketplace integrations
02
Dark analytics dashboard in black window on purple background, showing “Critical + High Alerts Over Time” chart, metrics 75, 12,000, 2,440, alerts table, and donut “Alerts by Classification”

Ai-powered Response

Detect Instantly. Contain Automatically.

Stop attacks before they land and instantly prioritize incidents when something breaks through. AI-powered workflows and automated response contain threats in seconds.

  • Prioritize incidents by severity and impact automatically

  • Trigger containment and remediation across surfaces

  • Reduce mean time to respond from hours to minutes

03
Dark analytics dashboard in a browser window: Global, My Accounts, DeepSafer, Warner Cyber, Select Group; “5 results found” with Table view showing Agent UUID, EventCount, and BehavioralIndicatorNames

Operational Advantage

Consolidate the Stack. Maximize the Investment.

Replace tool sprawl with a single platform, keep data hot, and use Purple AI to surface actionable insights faster. Fewer tools, lower overhead, more value from every dollar.

  • Unify point tools into a single platform

  • Surface insights faster with Purple AI investigation

  • Reduce operational overhead and total cost of ownership

04
Dark Marketplace web UI in a browser: “Marketplace”, tabs (Catalog selected), “Catalog (18)”, grid of AWS cards like Amazon RDS/S3 and Cloud labels

Native and Open XDR

Your Ecosystem. Not Another Silo.

Native protection across endpoint, cloud, and identity, plus open integrations through the Vigilant Marketplace. XDR outcomes that fit your environment, not the other way around.
  • Native detection and response across DeepSafer surfaces

  • One-click integrations with third-party tools via Marketplace
  • Extend XDR outcomes without ripping and replacing your stack

Decorative background gradient

Get Started

Symmetrical 3D geometric open box of glossy translucent panels around a glowing light-blue cube on a white background

Use Cases

One Platform. Every Workflow. Total Advantage.

Every Signal in One Place. Noise Gone.

Ingest and normalize data from any source to correlate across surfaces and prioritize what actually matters.

Security workstation with connected investigation views

Unify Alerts Across Every Surface

Endpoint, identity, cloud, email, and network alerts in a single prioritized view. No more console hopping.

Explore the Platform
Security analyst reviewing priority findings

Cut Through Noise with AI Prioritization

AI-powered triage surfaces the incidents that matter and suppresses the ones that don't.

Explore the Platform
Analyst reviewing connections between assets

Normalize Third-Party Data Automatically

Ingest from any source through the Vigilant Marketplace. Data is normalized and ready to correlate on arrival.

Explore the Platform

Explore the capabilities

Evaluate what fits your team’s needs.

Security signals and data

Security signals and data

Explore how security data context supports event review and investigation with Vigilant SIEM.


Explore the capability
Context for investigation

Context for investigation

Explore Vigilant Insight and the role of connected events and observations in analyst review.


Explore the capability
Detection and response support

Detection and response support

Review managed detection and response services and discuss your team’s support and coordination requirements.


Explore the capability

Customer & industry focus

Security for the organizations that connect Yemen.

From telecom infrastructure to mobile services, explore local security priorities and the DeepSafer capabilities that address them.
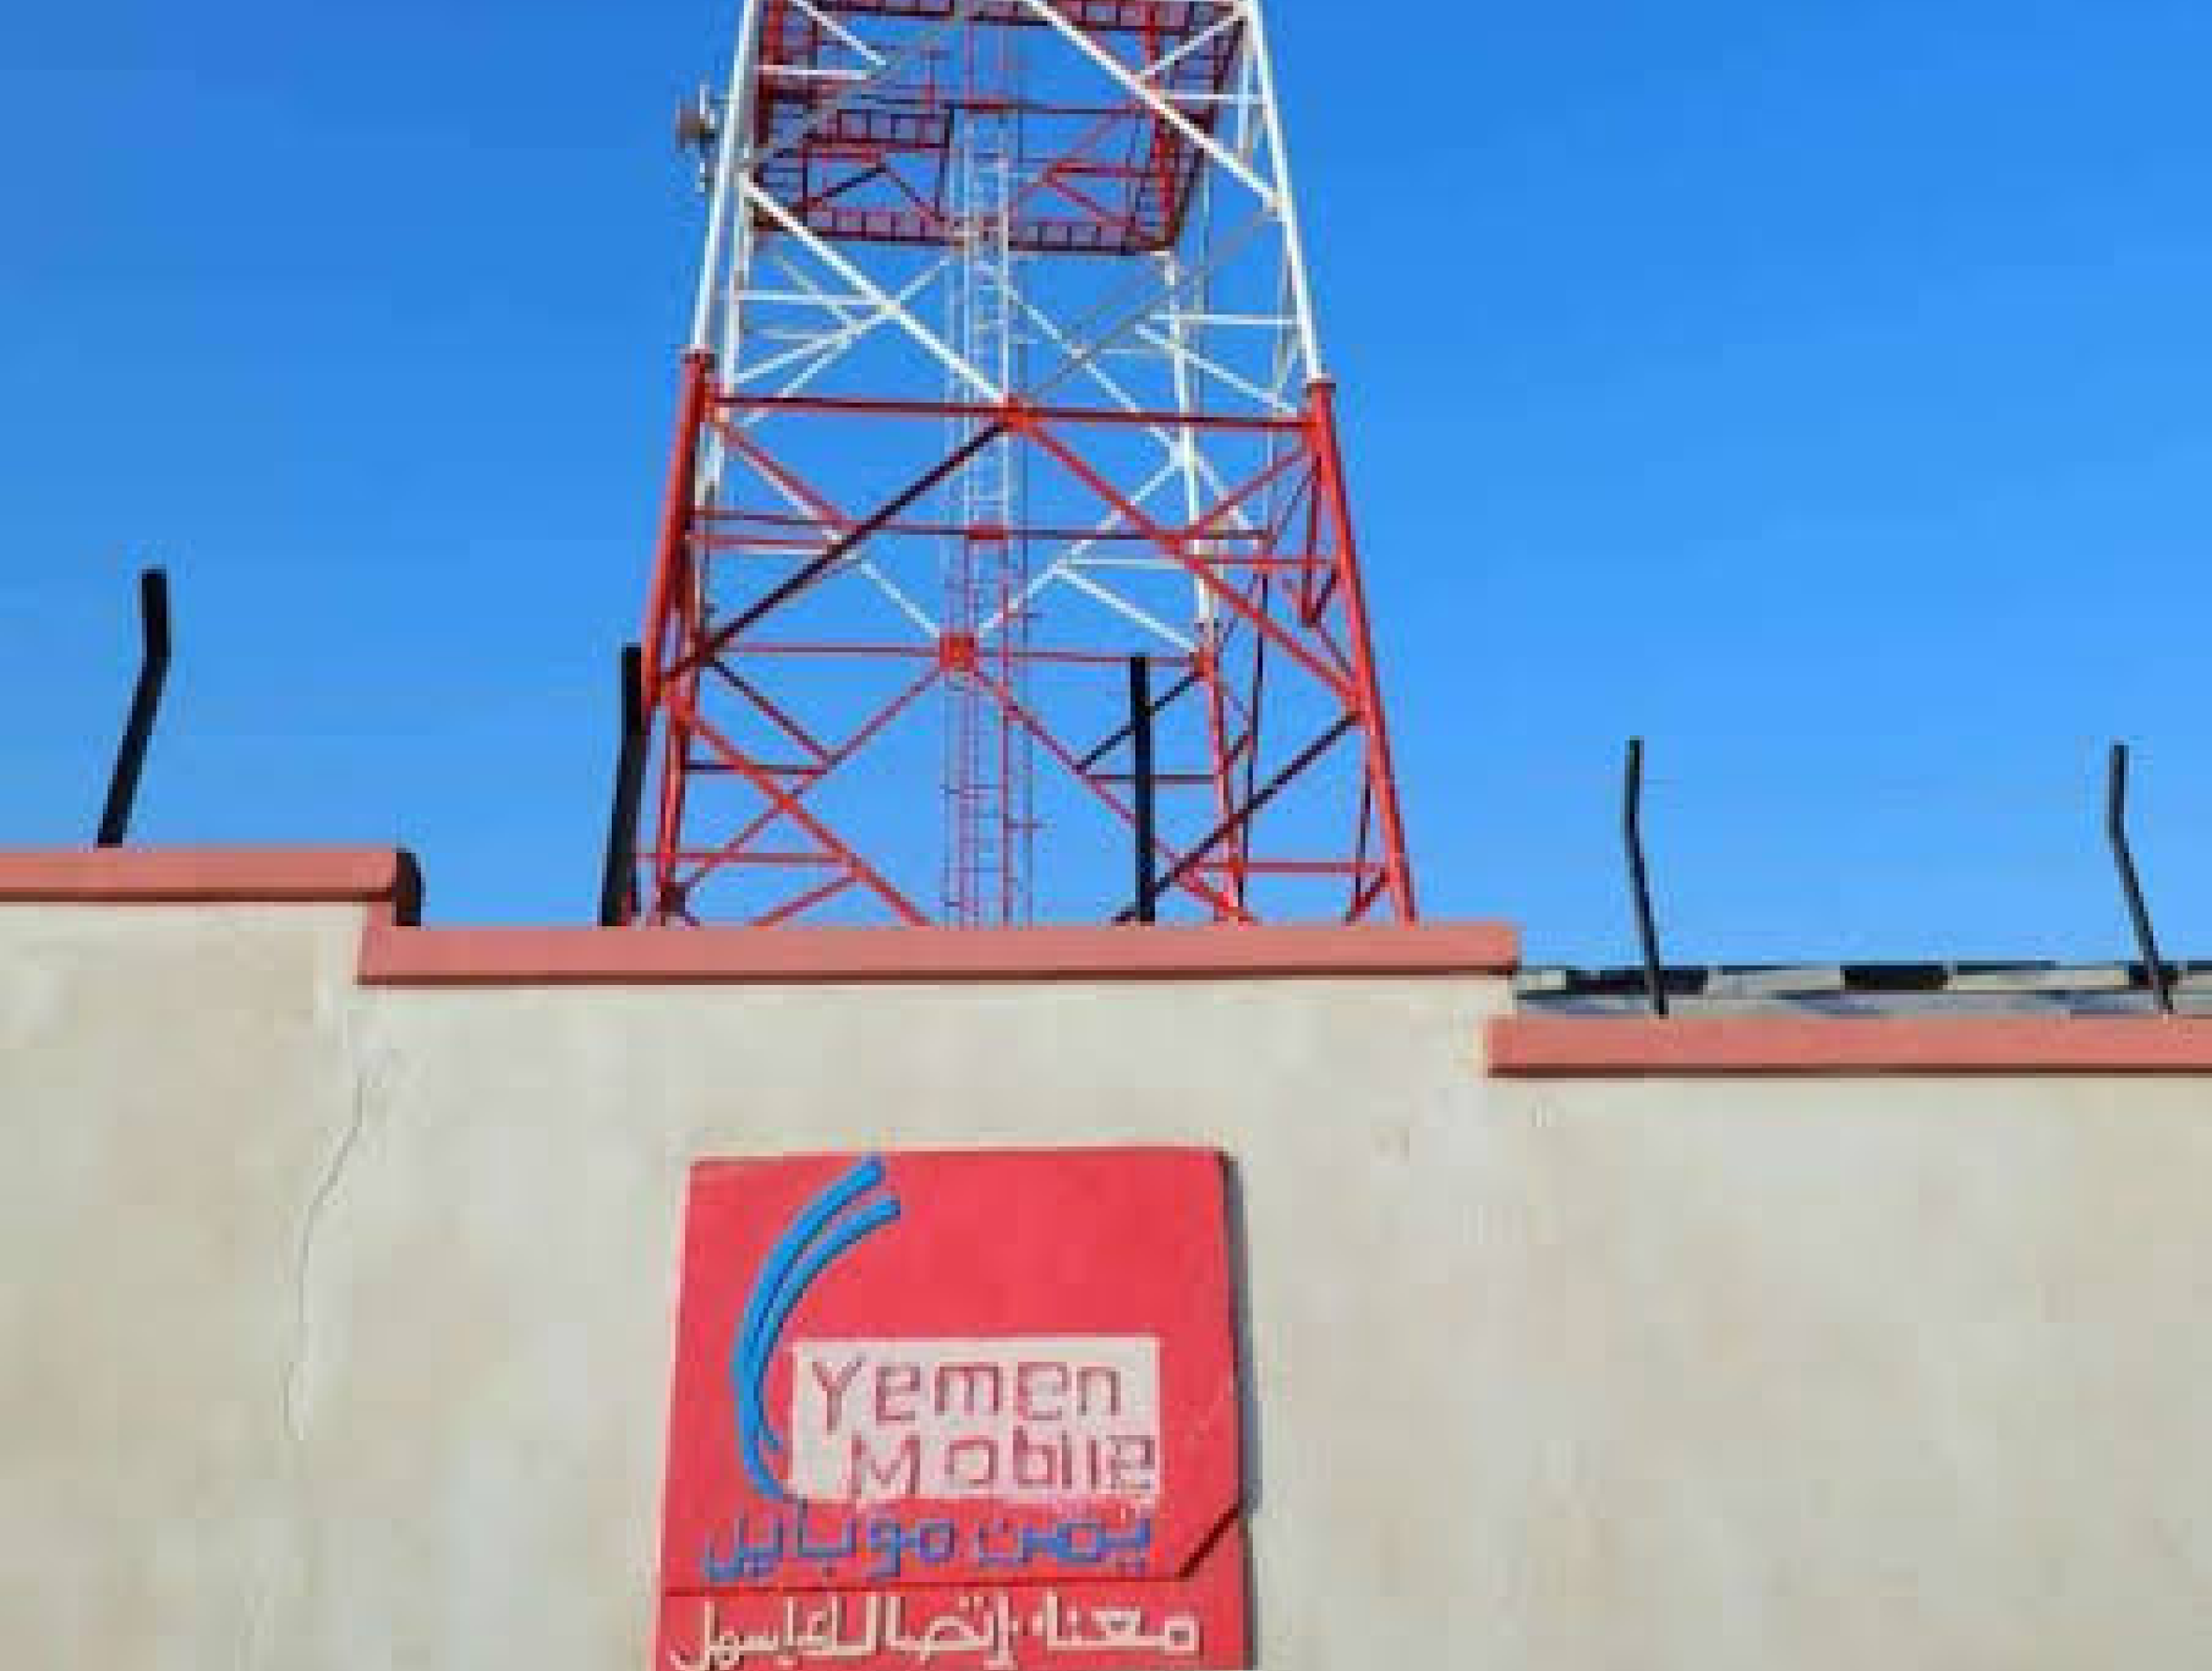
Yemen Mobile telecommunications tower and site

Connected security context across endpoints.

Yemen Mobile

Mobile services & endpoint protection

Review device signals and related services to guide investigations and identify what needs follow-up.


Explore the solution
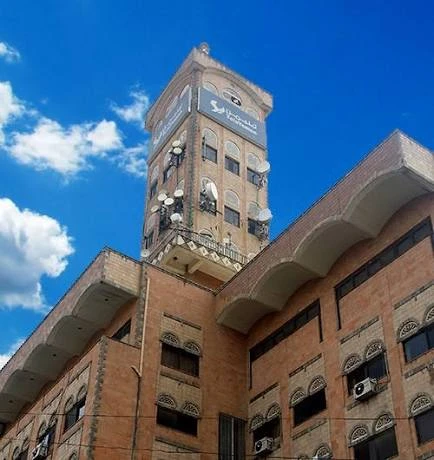
TeleYemen building and telecommunications tower

A shared view of infrastructure and services.

TeleYemen

Telecommunications & infrastructure

Bring event and asset context together for a clearer picture of activity relevant to security operations.


Explore the solution
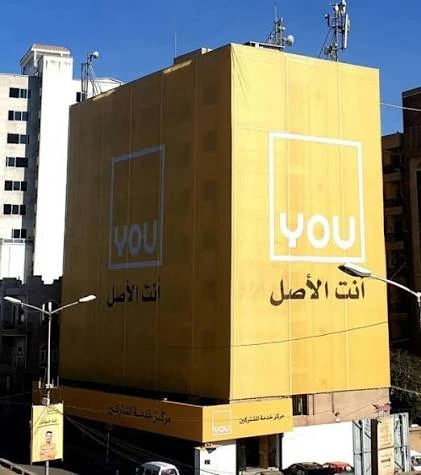
YOU company building with its yellow facade and logo

Response coordinated across teams.

YOU

Yemen Omani United telecommunications

Share evidence and context with the responsible teams to review options and coordinate next steps.


Explore the solution

Why DeepSafer?

XDR Without the Asterisk

Most vendors bolt what they call XDR onto legacy architectures. DeepSafer delivers XDR outcomes natively, from a platform designed to correlate and act across every surface from day one.
Connect Signals Across Your Tools

Connect Signals Across Your Tools

Bring relevant security signals into a shared workflow while keeping the context needed to investigate.

Explore the Platform
Bring Related Evidence Together

Bring Related Evidence Together

Review events, assets, and supporting observations together to build a clearer picture of suspicious activity.

Explore the Platform
Keep Analysts at the Center of Response

Keep Analysts at the Center of Response

Use connected context to support triage, review response options, and coordinate action with the responsible teams.

Explore Purple AI
Extend Coverage in Practical Stages

Extend Coverage in Practical Stages

Start with your available signals and review additional sources, integrations, and operational requirements as coverage develops.

Explore Endpoint Security

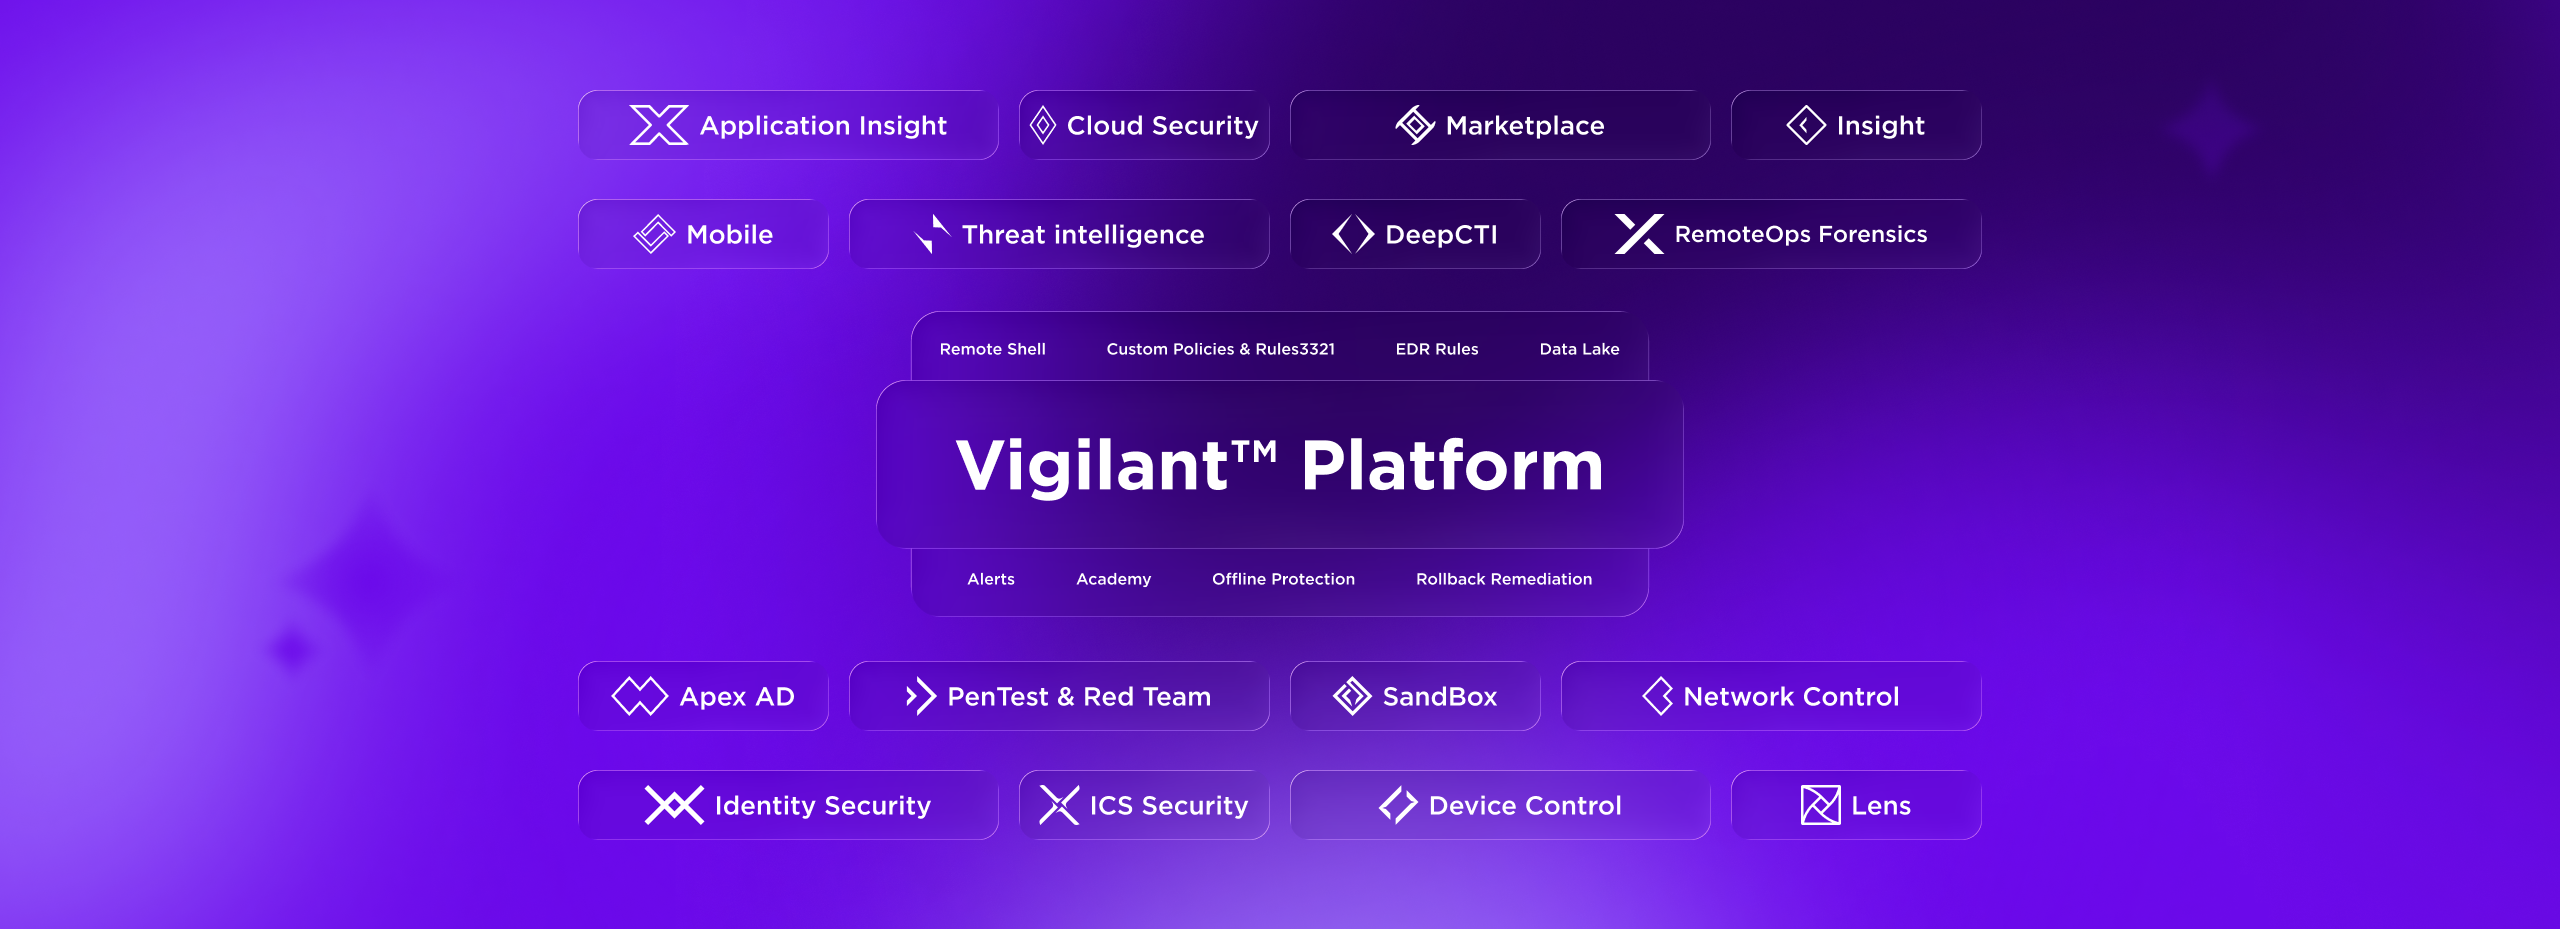
Platform Integration

Built on the Vigilant Platform. Not Bolted Onto It.

Futuristic UI mockup titled “Vigilant Platform” with neon platform, orb, labeled sections, and sidebar “DeepSafer”

Endpoint and Identity. The Native Foundation.

Behavioral AI across devices and credentials. Cross-surface correlation starts here.

AI SIEM. XDR With Retention and Scale.

XDR outcomes plus long-term log retention, compliance reporting, and queryable data for up to 7 years.

Hyperautomation. Response Without the Runbook.

Automated containment, remediation, and investigation across every connected surface. No manual playbooks.

Getting Started

XDR Outcomes. Faster Than You Think.

Setup

Start With What You Have

Deploy Vigilant Endpoint and connect existing data sources through the Marketplace. XDR value starts on day one.

Build

Add Surfaces. Extend Correlation.

Bring in identity, cloud, and third-party sources. Every new signal strengthens detection and response across the platform.

Evolve

Scale Into AI SIEM When Ready

Add long-term retention, compliance reporting, and advanced querying as your program matures. Same platform, broader outcomes.

Resources

Explore the Capabilities Behind XDR

Need Answers?

Frequently Asked Questions

XDR is a security approach that unifies detection, investigation, and response across multiple attack surfaces, including endpoint, identity, cloud, email, and network, giving security teams full attack context from a single platform.

Unlike standalone EDR, which focuses on endpoints alone, XDR correlates signals across surfaces so teams can detect and respond to attacks that span their entire environment.

On the Vigilant Platform, XDR outcomes scale with your program. Start with endpoint, extend to additional sources as your needs mature, and move to AI SIEM when retention and compliance requirements grow.

DeepSafer delivers XDR outcomes through the Vigilant Platform, not as a separate SKU. Customers typically start with Vigilant Endpoint or Vigilant Complete and extend XDR capabilities by connecting additional data sources such as identity, cloud, and third-party integrations through the Vigilant Marketplace.

For teams that also need long-term log retention and compliance reporting, Vigilant AI SIEM converges XDR and SIEM capabilities in a single platform, giving organizations a choice that fits their security maturity and operational needs.

Yes, through Vigilant Network Control. Network Discovery identifies every device visible on your internal network, including unmanaged endpoints, IoT devices, and assets outside your managed inventory. Vulnerability scanning applies to DeepSafer-protected endpoints. Unmanaged devices can be brought under protection and scanning by deploying a DeepSafer agent directly from the discovery workflow.

EDR detects and responds to threats on endpoints. SIEM collects and stores logs for correlation, compliance, and historical analysis. SOAR orchestrates response actions through manual playbooks. XDR unifies detection, investigation, and response across multiple surfaces in a single platform, replacing the need to stitch these tools together.

DeepSafer's Vigilant SIEM converges SIEM and XDR capabilities, while Hyperautomation replaces traditional SOAR with automated workflows that don't require manual playbook creation.

The Vigilant Platform ingests and normalizes data from any source into a unified data layer, then correlates signals across endpoint and identity, cloud, AI systems, and third-party tools automatically.

AI-native workflows prioritize incidents by severity, and automated response actions contain threats across surfaces from a single console. Purple AI accelerates investigation by letting analysts query across all connected data in natural language.

The Vigilant Platform delivers native coverage across endpoint, identity, and cloud workloads. Through the Vigilant Marketplace, teams extend XDR outcomes to third-party sources including email, network, firewall, and SaaS applications with pre-built integrations.

Every connected source feeds the same unified data layer, strengthening correlation and response across the full environment.

XDR focuses on real-time detection, correlation, and automated response across multiple security surfaces. AI SIEM converges those same XDR capabilities with long-term log retention, compliance reporting, and enhanced querying for up to 7 years.

Teams that need XDR outcomes without extended retention requirements can start with EDR plus additional sources. Teams that also need retention and compliance can deploy AI SIEM, which includes full XDR capabilities on the same platform.

Decorative background gradient

Next Steps

See Every Surface. Own the Advantage.

Dark dashboard UI with purple-highlighted nav, summary cards showing 149, 7, 78, 56, 1.2 h, and a status table with linked purple text