Vigilant SIEM

One Platform. Every Signal. Instant Clarity.

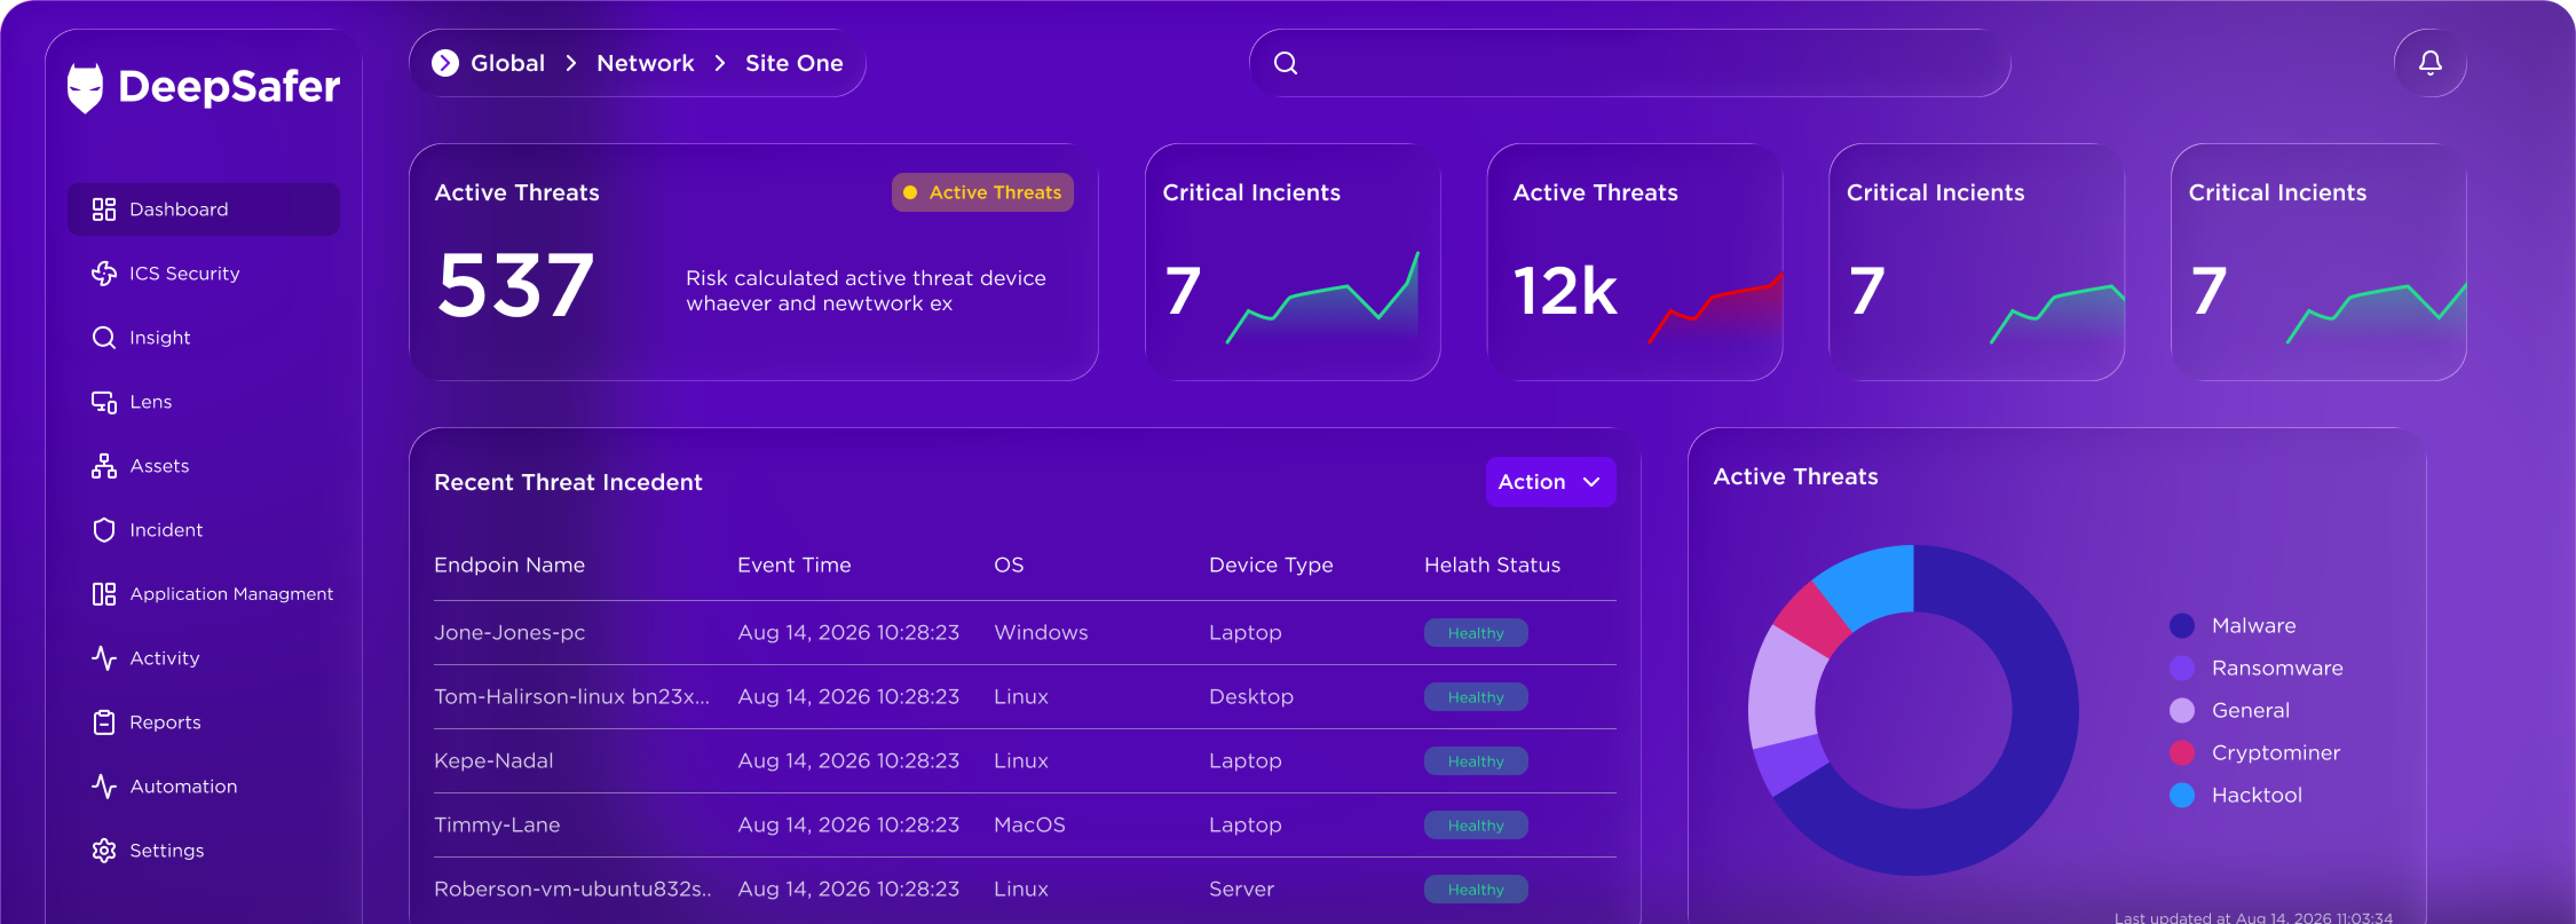
Security data piles up across disconnected tools, slowing detection and burying analysts in manual correlation. Vigilant SIEM brings every log, alert, and signal into one intelligent platform — turning scattered noise into decisive action before threats take hold.

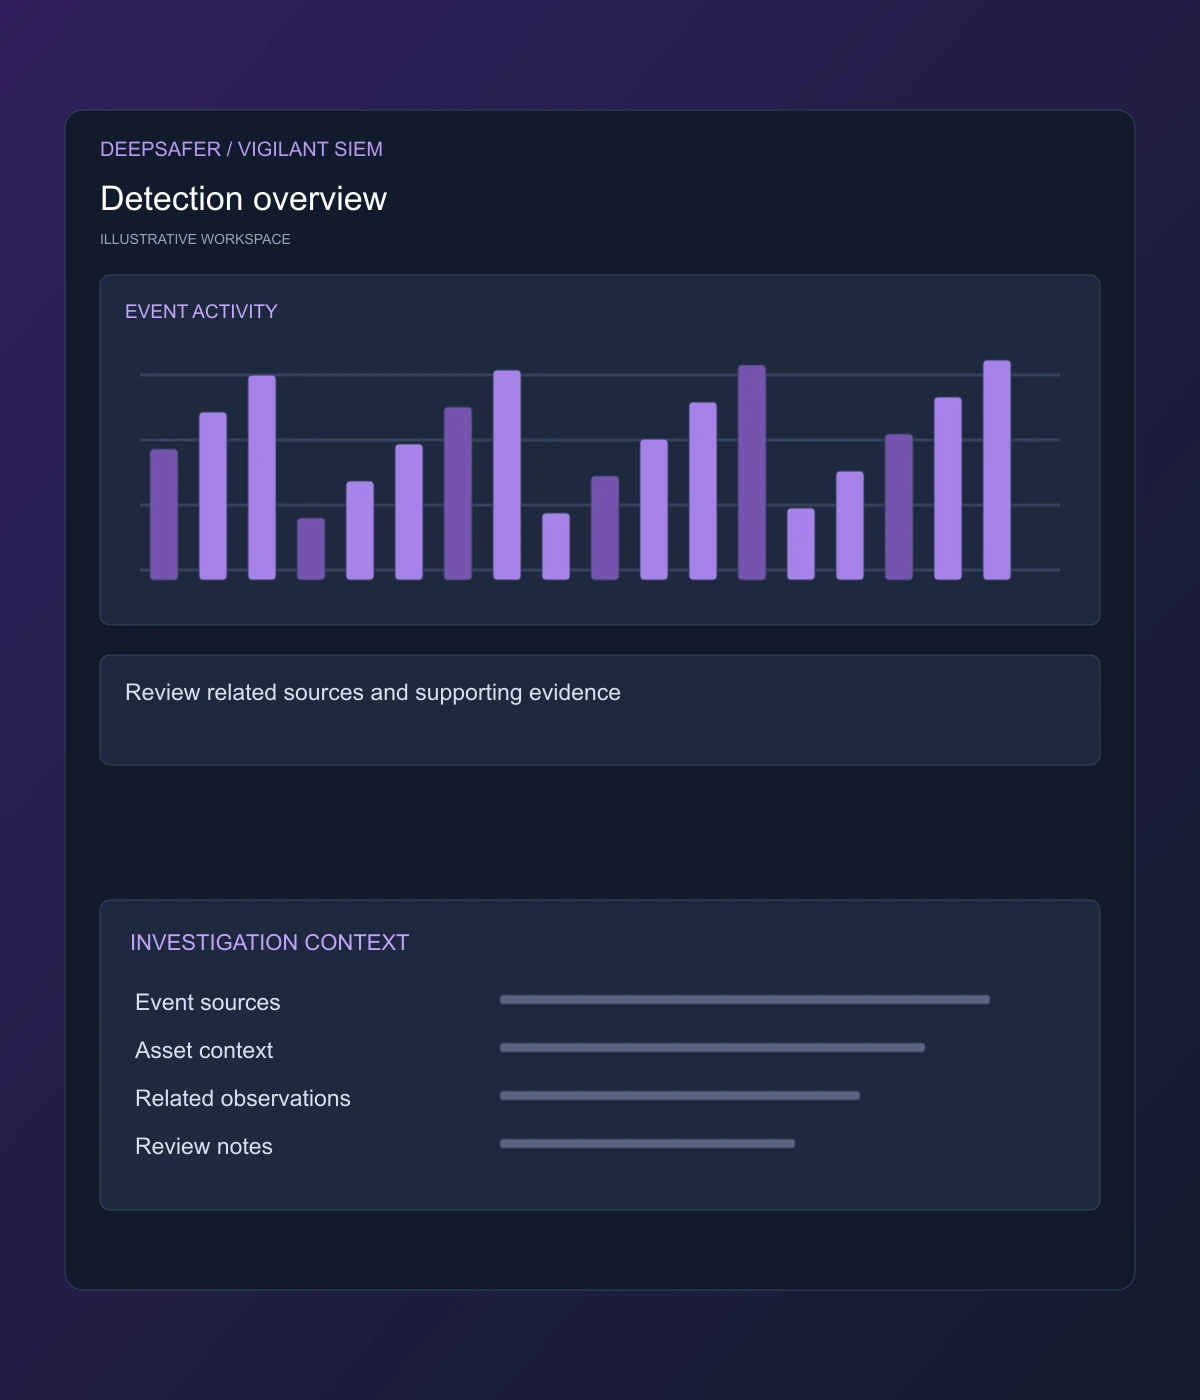
Illustrative SIEM detection overview and investigation context

Today's Reality

01
Dark navy abstract geometric design with stacked translucent neon hexagons and layered glowing isometric diamond tiles

Vigilant Detection & Correlation

Fewer Alerts. Only the Ones That Matter.

Thousands of daily alerts drown real threats in noise. Vigilant correlates events in real time and applies risk-based scoring, surfacing the handful of incidents that truly demand your teams attention

  • Correlate millions of events into a handful of real risks

  • Prioritize incidents automatically based on real business risk

  • Cut false positives and give analysts back their time
02
Abstract geometric 3D wireframe hexagon with purple-blue panels, neon glows, and a gray dot perspective grid background

Vigilant Data Pipelines

Stop Fighting Data. Start Finding Threats.

End the toil of manual log cleanup. Vigilant Data Pipelines normalize, enrich, and route security data cleanly the moment its ingested — turning raw, messy logs into clean, decision-ready intelligence from the start.

  • Ingest data seamlessly across cloud, identity, endpoints, and tools

  • Reclaim hours of manual log parsing every single week

  • Feed every AI model with clean, high-fidelity security data

03
Abstract digital network on a dark background: glowing tilted platform with hexagon outlines and pink glowing nodes on a grid

Vigilant Response Orchestration

From Alert to Action, Automatically.

Stop switching between tools mid-incident. Vigilant orchestrates response with automated playbooks and maps every threat to the MITRE ATT&CK framework, so your team acts fast with full context, every time.

  • Trigger automated playbooks the moment a threat is confirmed

  • Map every incident directly to the MITRE ATT&CK framework

  • Respond consistently from a single unified workspace

Decorative background gradient

Get Started

Glowing translucent light-blue 3D cube with symmetrical neon starburst prism bars on a white background, futuristic abstract

Where it makes a Difference

The AI SIEM Advantage. At Every Stage.

Detect Faster. Investigate Smarter.

Connect data and apply AI-driven investigation to surface real threats quickly, without manual correlation or tool switching.

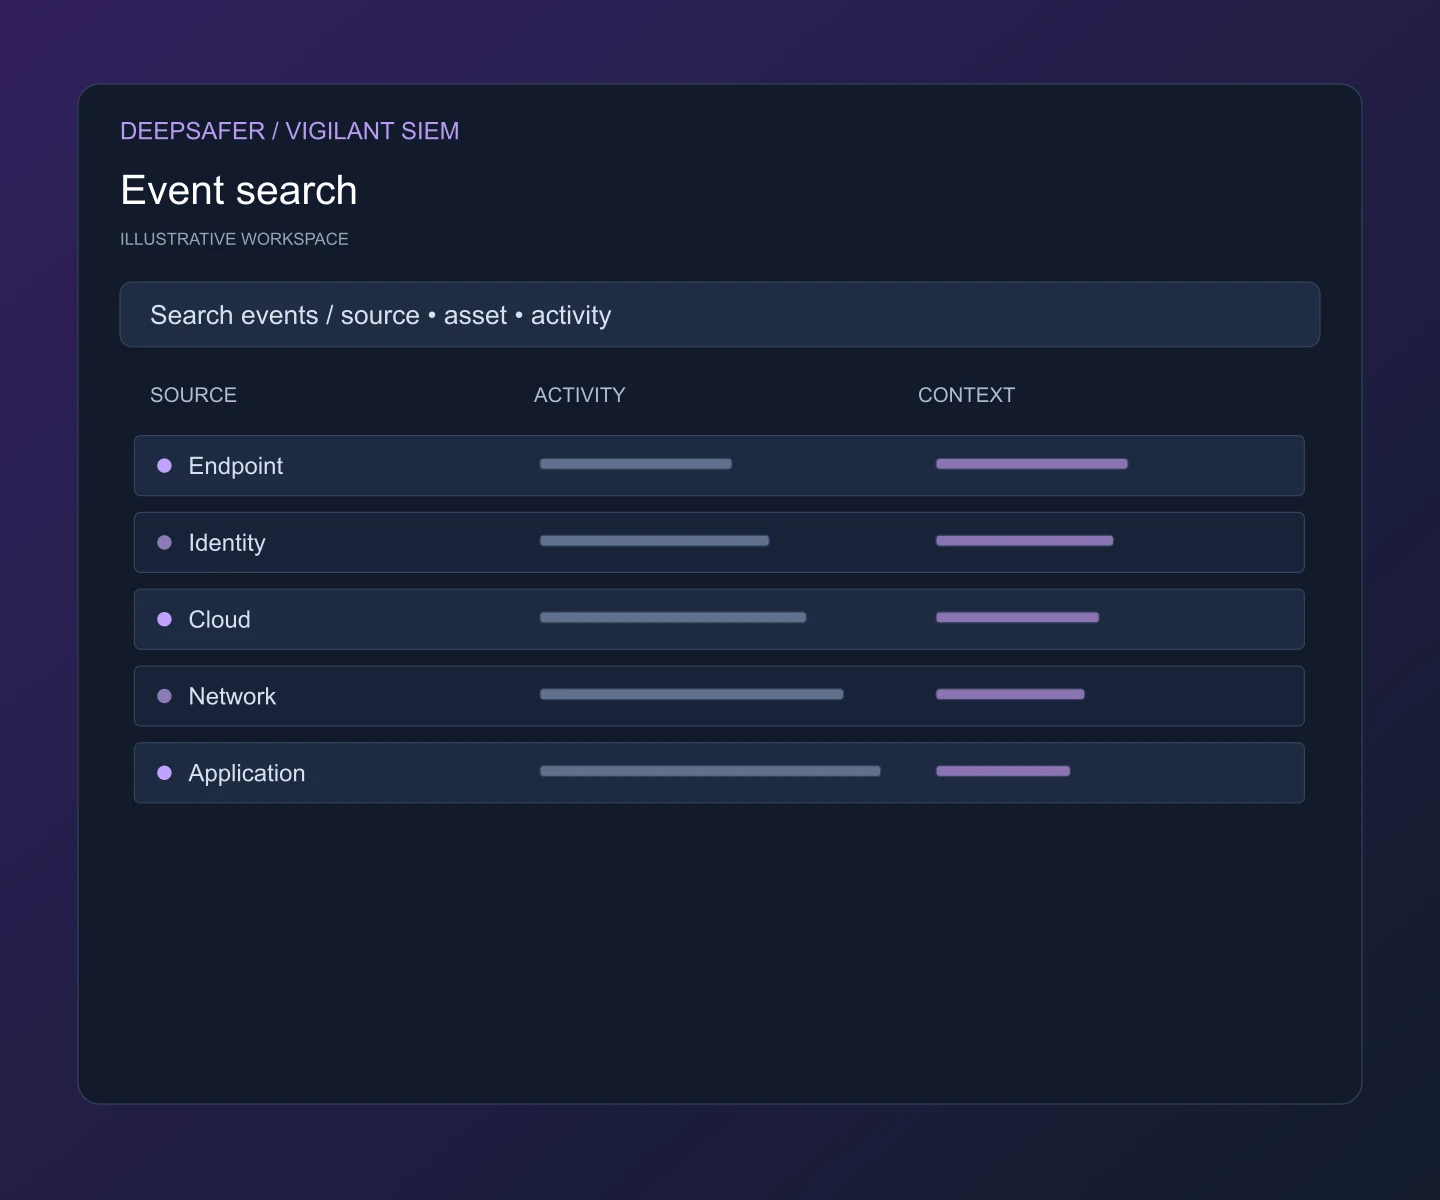
Illustrative SIEM event search

Hunt Threats Across Your Entire Environment

Uncover hidden threats with full context. Search and uncover insights in security data across cloud, identity, endpoints, and tools.

Explore threat hunting
Illustrative alert review queue

Cut the Noise. Pick Up the Pace.

Use AI to enrich alerts, reduce false positives, and surface the incidents that actually require action.

Request a demo
Illustrative investigation timeline

Investigate with Full Context

Automatically connect signals, timelines, and evidence to understand what happened.And what to do next.

Request a demo

SIEM in practice

From scattered events to a shared investigation.

Vigilant SIEM helps security teams bring event context together, review activity, and coordinate follow-up across their environment.

  1. 01

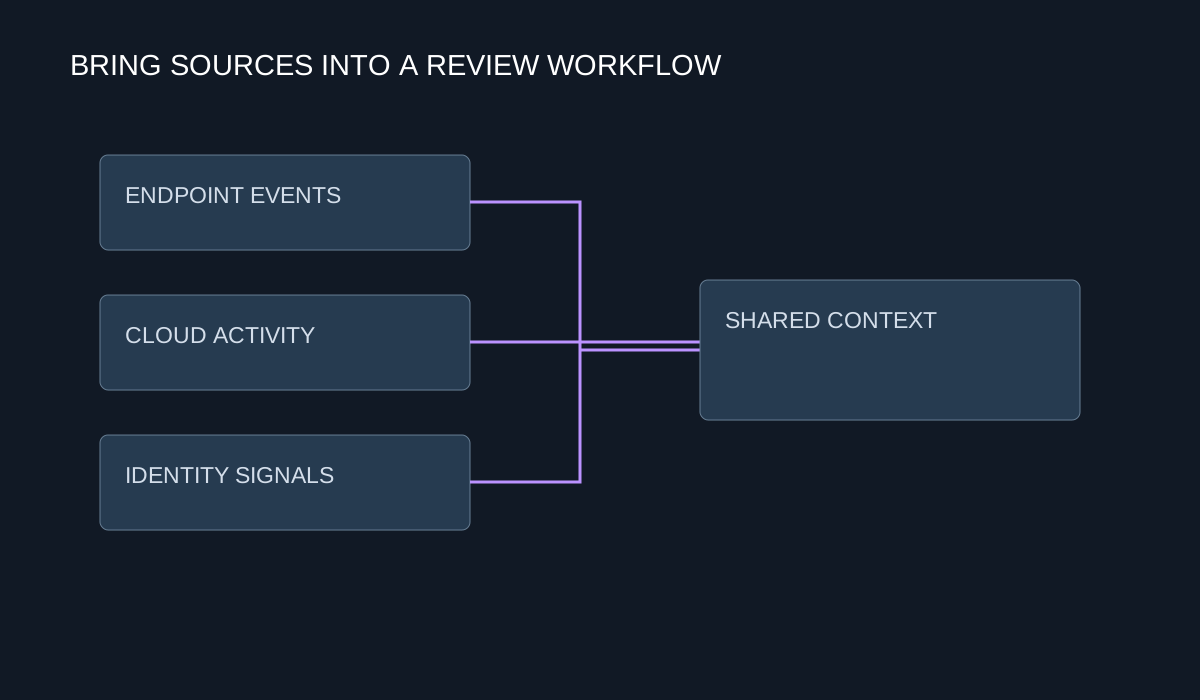
    Collect

    Bring relevant event sources into a shared data workflow and review how their fields are represented.

    Endpoint, cloud, and identity sources connected to shared security context
  2. 02

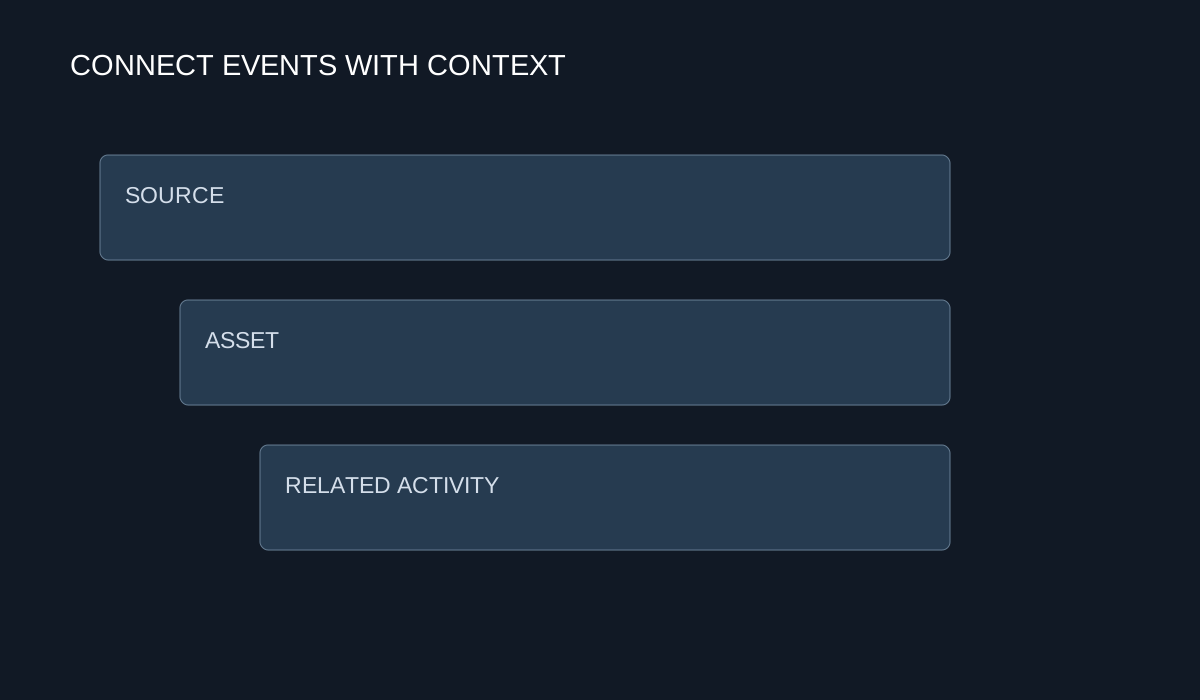
    Correlate

    Connect source, asset, and activity context to support a more complete investigation.

    Source, asset, and related activity context brought together
  3. 03

    Coordinate

    Validate findings and share the evidence needed to review response options with the responsible teams.

    Evidence review, finding validation, and coordinated response workflow

Customer & industry focus

Security for the organizations that connect Yemen.

From telecom infrastructure to mobile services, explore local security priorities and the DeepSafer capabilities that address them.
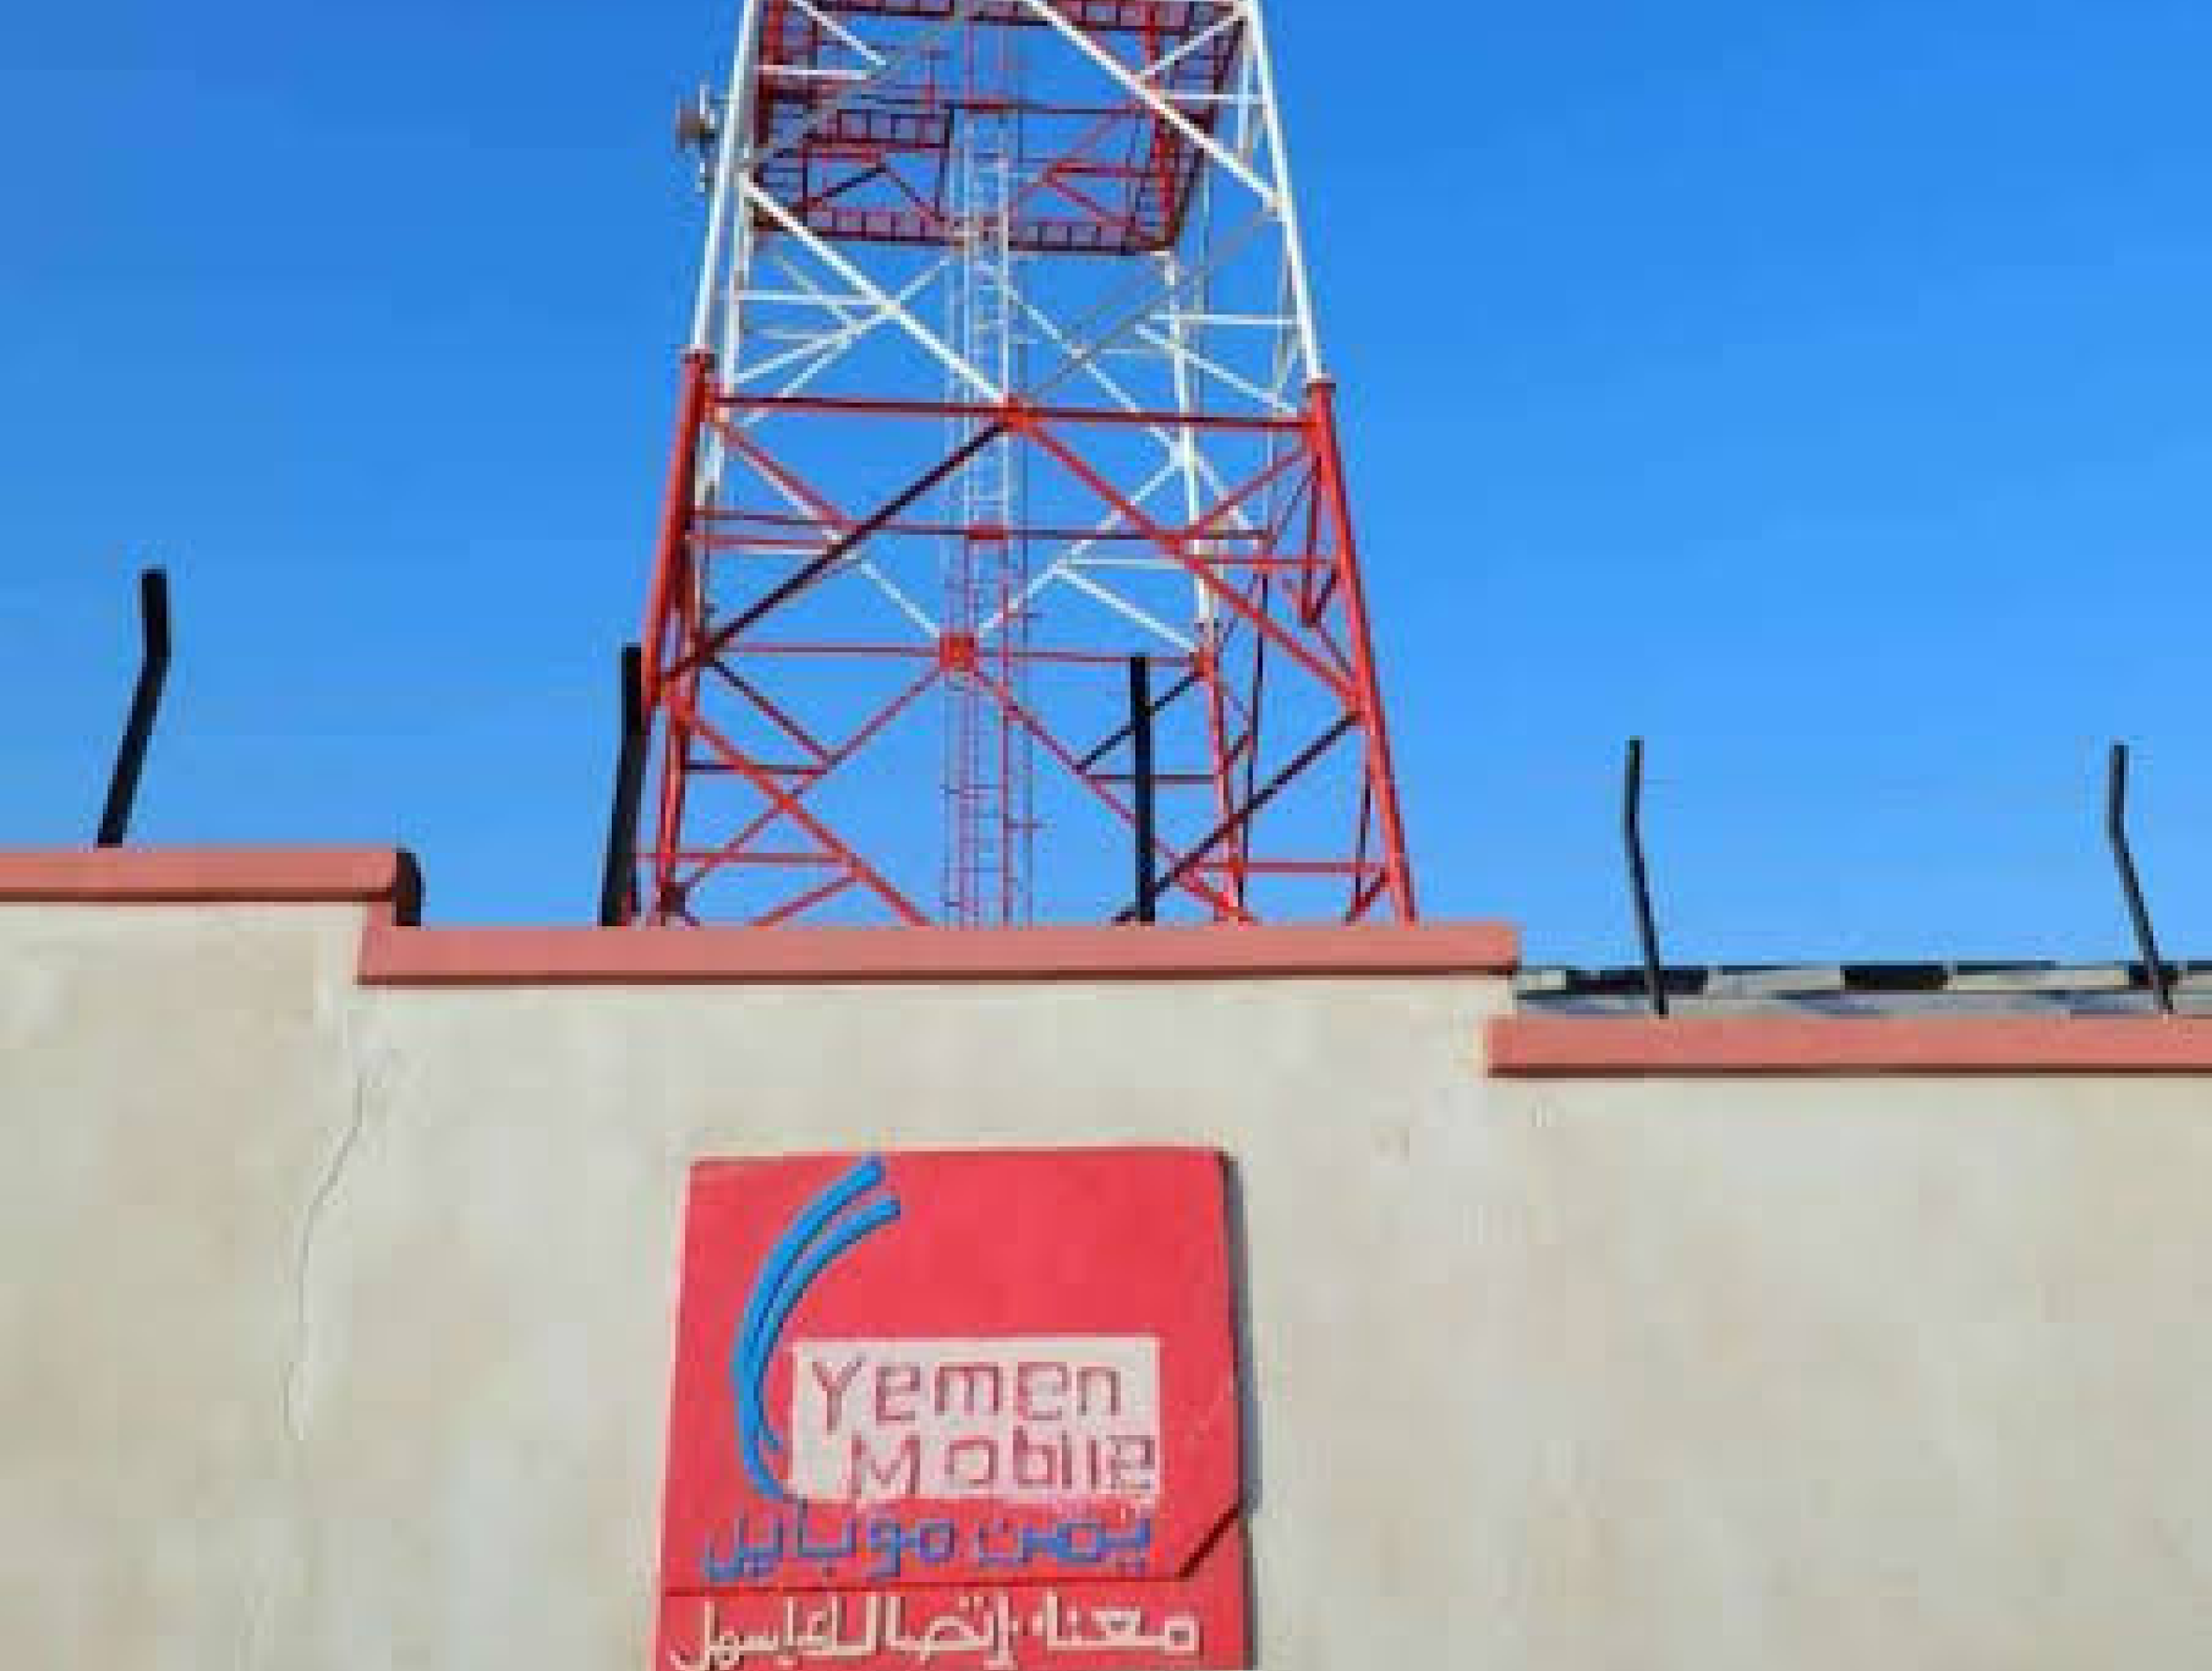
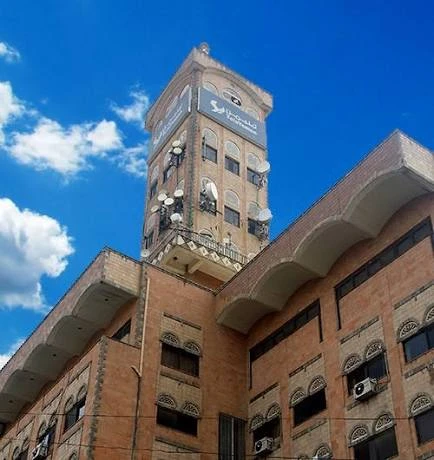
Yemen Mobile telecommunications tower and site

Clearer event context for protection teams.

Yemen Mobile

Mobile services & endpoint protection

Bring device and service signals together to support alert review and investigation into relevant activity.


Explore the solution
TeleYemen building and telecommunications tower

A connected view of infrastructure.

TeleYemen

Telecommunications & infrastructure

Relate events to assets and sources to guide investigation and share evidence with responsible teams.


Explore the solution
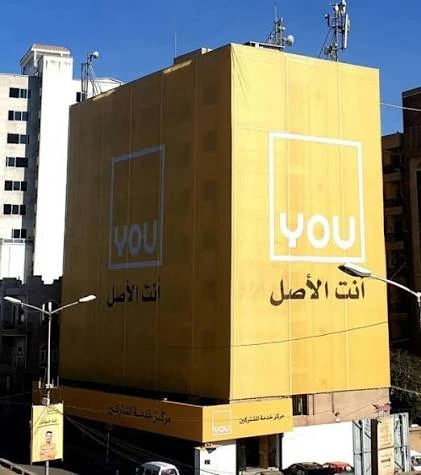
YOU company building with its yellow facade and logo

Follow-up across security and operations.

YOU

Yemen Omani United telecommunications

Review findings and share investigation context to support response decisions and operational next steps.


Explore the solution

Why DeepSafer?

It’s Not the Same Old SIEM

Vigilantᵀᴹ AI SIEM eliminates fragmented investigation workflows by unifying data, intelligence, and response into a single operational system.
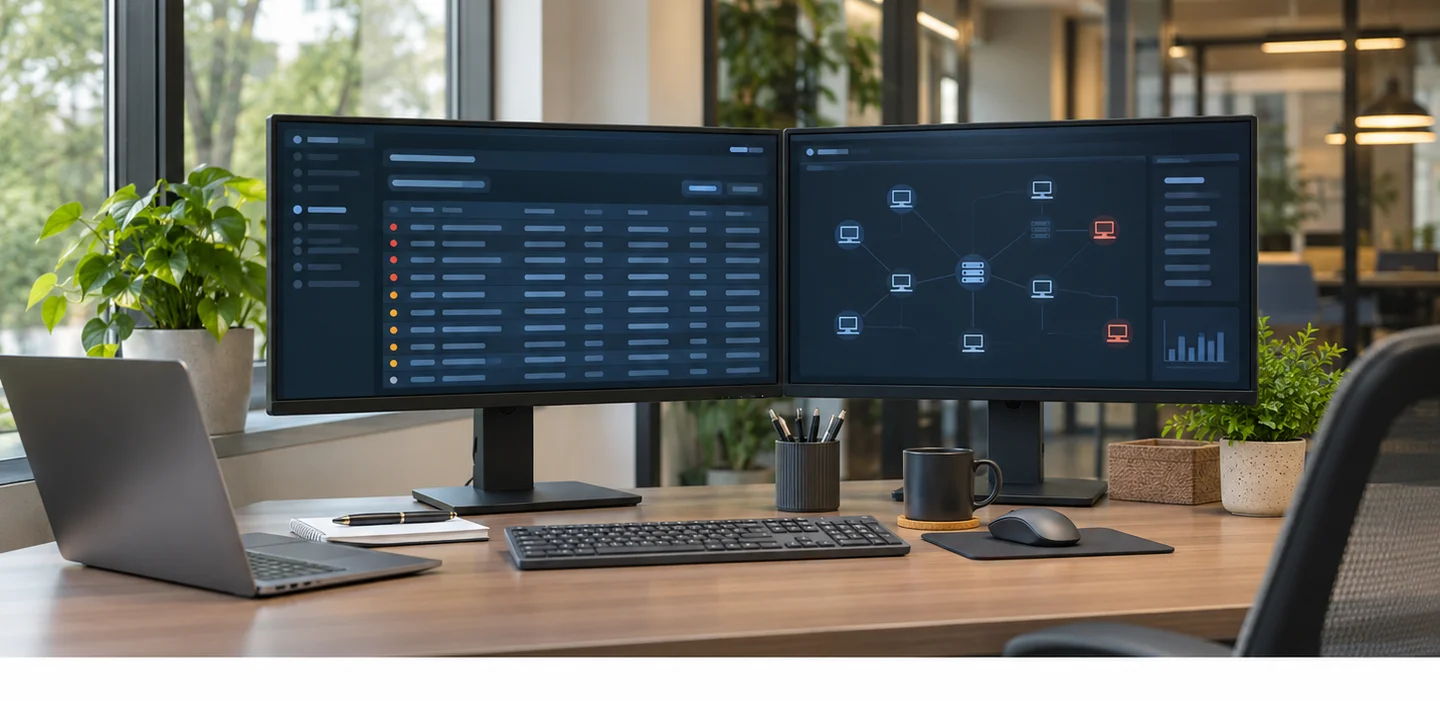
Connected security workstation showing investigation context

Unified by Design

Security data from across your environment lives on one shared foundation. No swivel-chair workflows or jumping between tools. Get complete context for every investigation, decision, and response.

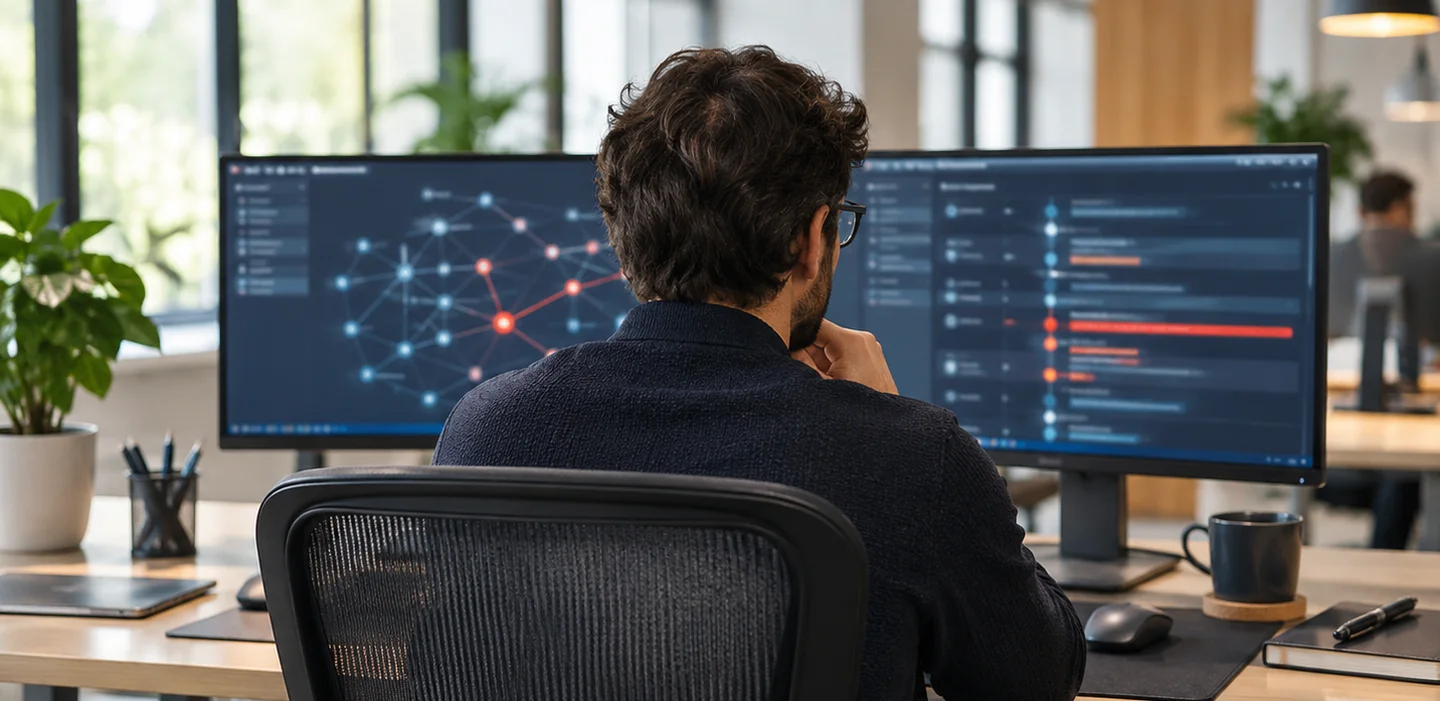
Male security analyst reviewing related activity across two screens

AI That Amplifies Every Analyst

Deploy AI to handle contextual enrichment and investigation automatically, so analysts can focus on judgment and action instead of manual work.

Male security analyst reviewing priority findings

Action Without Friction

Containment, remediation, and workflows happen in the same system, eliminating handoffs and accelerating action when it matters most.

Organized enterprise IT operations workspace

Less Sprawl. More Signal.

Shared intelligence, workflows, and visibility replace fragmented tooling. Operations get simpler as environments grow, not more complex.

Platform Integration

Connected Across the Platform. Built to Act as One.

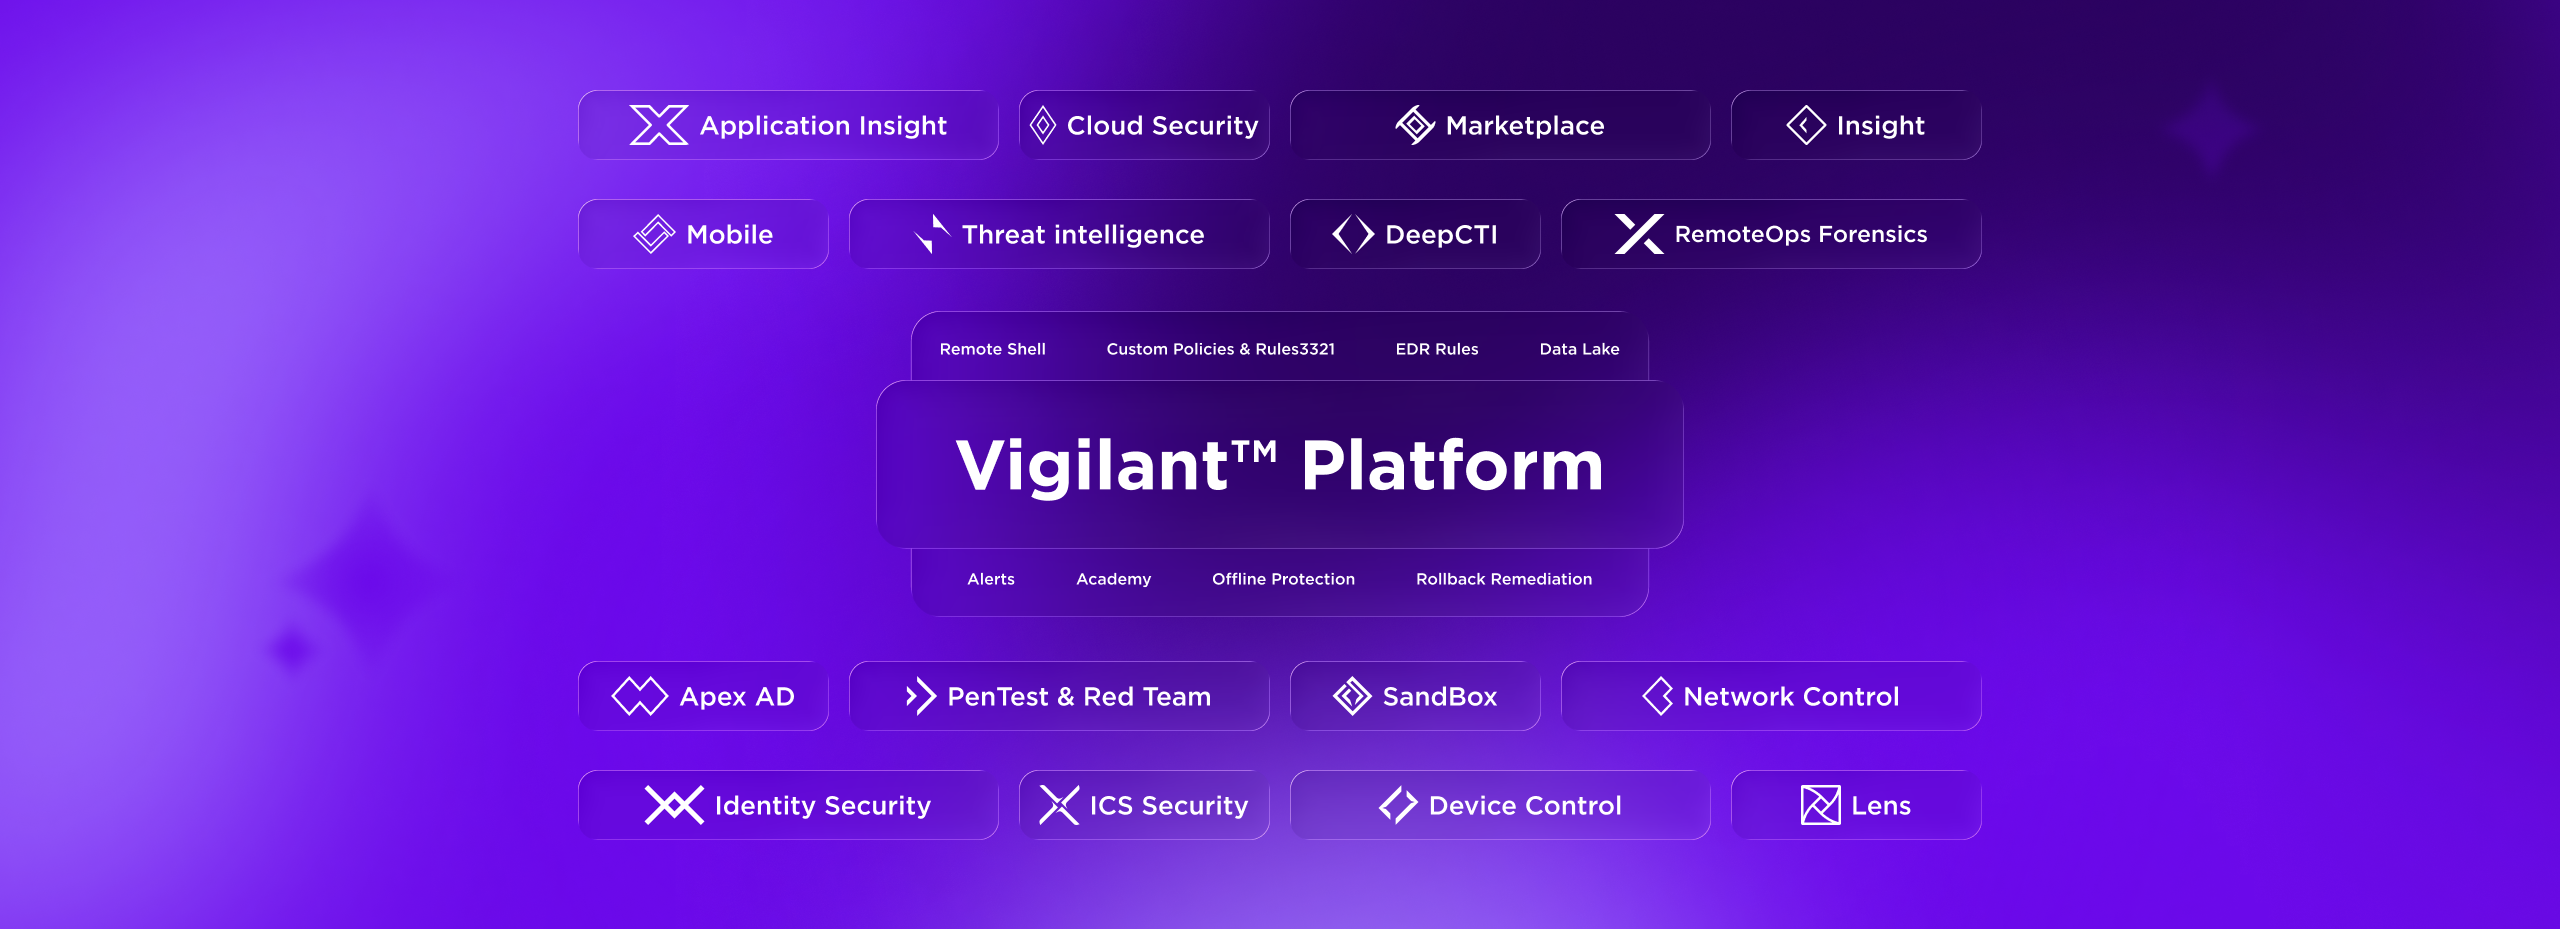
Futuristic UI mockup titled “Vigilant Platform” with neon platform, orb, labeled sections, and sidebar “DeepSafer”

Every Source. One Pipeline.

Ingest telemetry from endpoints, cloud workloads, identity, and third-party tools through a single data pipeline. No manual normalization, no visibility gaps.

AI That Works Across Every Data Source

AI delivers context on activity across the full platform, automatically surfacing clear, actionable incidents.

Response That’s Built-In, Not Bolted On.

Eliminate the need for handoffs. Expedite response with full context. Containment, remediation, and workflows execute natively within the platform.

Getting Started

Success Doesn’t End at Deployment

Implementation and Onboarding

Our experts help you deploy Vigilant SIEM and configure workflows aligned to your environment and operational goals from day one.

Learn more

Training and Enablement

Flexible, on-demand and instructor-led training helps your team adopt AI SIEM confidently and apply it effectively across real security operations.

Explore training

Ongoing Support and Success

Professional services, proactive health monitoring, and a dedicated Customer Success Manager support long-term outcomes as your needs evolve.

Learn More

Measure, Optimize, Evolve.

Ongoing guidance helps you continuously improve visibility, investigation speed, and response effectiveness as threats change.

Learn more

Need Answers?

Frequently Asked Questions

Vigilant SIEM collects, correlates, and analyzes security data from across your entire environment in one platform, detecting threats in real time and giving your SOC the clarity to respond before incidents escalate.

Traditional SIEMs bury analysts in raw alerts and complex queries. Vigilant uses AI-driven pipelines, risk-based correlation, and natural-language investigation to cut the noise and deliver decisive answers in seconds, not hours.

No. Vigilant SIEM integrates seamlessly with your existing cloud, identity, endpoint, and security tools, ingesting data from all of them without disrupting your current infrastructure or workflows.

DeepSafer's expert SOC team runs Vigilant SIEM on your behalf around the clock, using AI-driven detection, real-time correlation, and automated response to catch threats early, investigate instantly, and stop attacks before they reach your critical systems.

Vigilant automatically generates detailed reports on threat activity, incidents, and network health, and maps findings to frameworks like MITRE ATT&CK, making audits and compliance reporting fast and effortless.a

Decorative background gradient

Next Steps

Give Your SOC the Advantage. Turn Data Into Defense.

Dark dashboard UI with purple-highlighted nav, summary cards showing 149, 7, 78, 56, 1.2 h, and a status table with linked purple text