The Modern SOC Crisis: Drowning in Disconnected Telemetry
Modern Security Operations Centers face an unprecedented surge in alert volume. The average enterprise generates over 11,000 security alerts per day across hundreds of disparate tools.
This noise inevitably leads to alert fatigue, with up to 45% of critical security signals left uninvestigated, allowing determined adversaries weeks of undetected dwell time.
What is SOC Hyperautomation?
Hyperautomation represents a paradigm shift beyond brittle custom scripts. It combines:
- Automated Cross-Domain Correlation: Stitching endpoint, network, identity, and cloud logs into unified forensic story graphs.
- AI-Driven Threat Scoring: Instantly mapping active tactics to the MITRE ATT&CK framework.
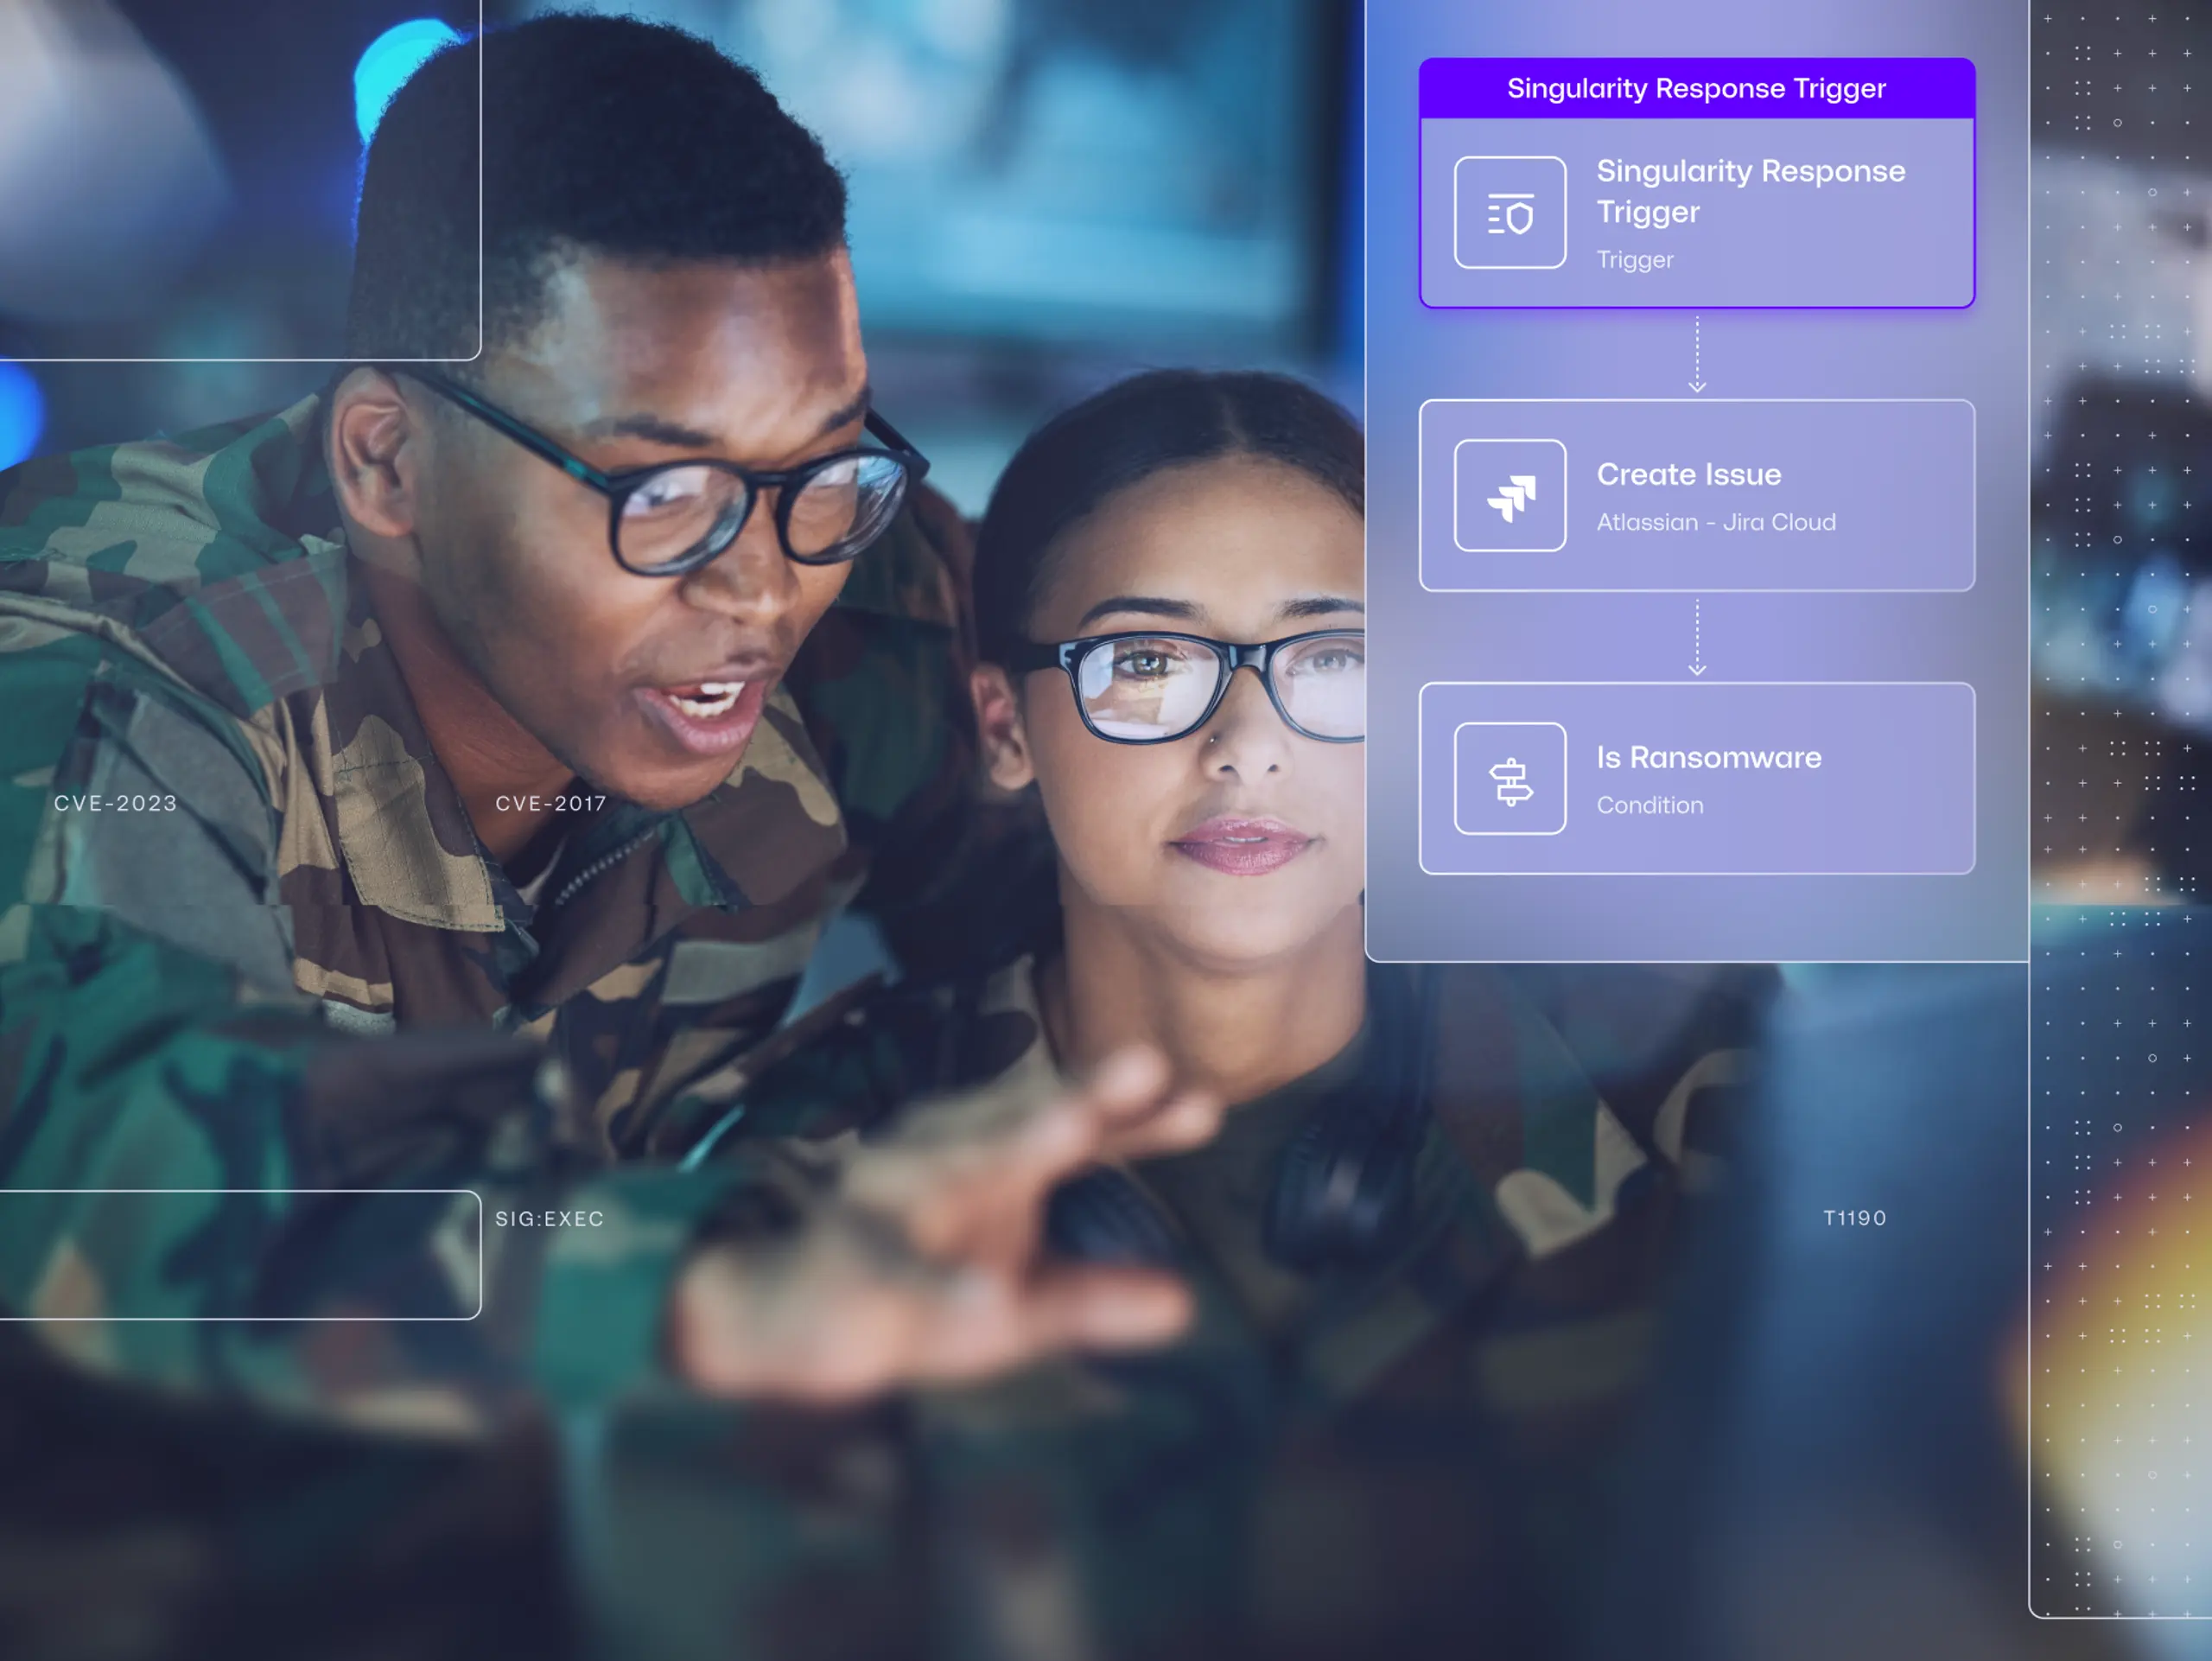
- Autonomous Playbook Execution: Containing ransomware, revoking compromised sessions, and quarantining endpoints in milliseconds.
# DeepSafer Autonomous Playbook Configuration
name: Critical Ransomware Mitigation
trigger: high_fidelity_ransomware_signal
actions:
  - isolate_endpoint: immediate
  - terminate_malicious_process: active_tree
  - rotate_compromised_credentials: automated_iam
  - snapshot_memory_forensics: cloud_vault
Measurable Impact with DeepSafer
Organizations powered by DeepSafer SOC achieve remarkable operational efficiency gains:
- Mean Time to Remediate (MTTR): Dropped from 4.2 hours to under 35 seconds.
- Noise Reduction: False positives decreased by more than 88%.
- Analyst Empowerment: Shifts security staff focus from repetitive alert triage to proactive threat hunting and continuous resilience engineering.